Notfallmanagement: Vorbereitung auf den Ernstfall mit ISO 27001 und ISO 9001 Zertifizierung
Emergency management (Notfallmanagement) is the systematic process of preparing an organization to prevent, respond to, and recover from disruptive incidents that threaten operations, information availability, or client service delivery. Effective preparation reduces financial loss, preserves reputation, and ensures contractual commitments remain met, while also aligning with procurement expectations for supplier resilience. This article explains how ISO 27001 (information security / ISMS) and ISO 9001 (quality management) work together to strengthen business continuity, incident response, and client trust. Readers will learn the core components of an emergency management program, practical steps for building crisis and continuity plans, how ISO 27001 and ISO 9001 map to those activities, and trends showing why certification matters for resilience in 2024 and beyond. Throughout, we provide actionable checklists, EAV-style comparison tables, and concise templates you can adapt for internal risk assessment, business impact analysis, incident response playbooks, and certification readiness. The guidance emphasizes a risk-based approach, measurable recovery objectives (RTO/RPO), and alignment with procurement and regulatory drivers so organizations can both protect operations and satisfy client requirements.
Indeed, the broader landscape of ISO standards offers comprehensive guidance for organizations aiming to enhance resilience and establish robust business continuity management processes.
ISO Standards for Crisis Preparedness & Business Continuity
This chapter focuses on preparing for crises by enhancing resilience as defined by ISO standards, and adopting management disciplines that contribute towards preparing for crisis, with an emphasis on business continuity management. This chapter will offer advice on how to prepare your organization to respond to a disruption and enhance resilience through business continuity management processes as defined by ISO 22301:2019. A road map to enhancing resilience by establishing business continuity management and its processes is presented to the reader.
Preparing for Crises: Enhancing Resilience: The Concept of ISO Standards, 2022
Why is Emergency Preparedness Essential for Organizations?
Emergency preparedness is the proactive capability to identify risks, limit exposure, and restore critical services when incidents occur; it works by combining risk assessment, continuity planning, and tested response procedures to reduce downtime and financial harm. Being prepared preserves contractual service levels and client trust, limits regulatory exposure, and enables faster, measured recovery that minimizes reputational damage. Organizations that embed preparedness into management systems benefit from clearer roles, documented processes, and continuous improvement cycles that make responses repeatable and auditable. Recent surveys show a majority of firms face disruptions that affect revenue and client confidence, reinforcing that preparedness is no longer optional for suppliers in regulated or competitive markets.
What are the key components of effective emergency management?
Effective emergency management comprises a small set of interlocking components that create resilience through documentation, practice, and improvement. Risk assessment identifies threats and vulnerabilities, while Business Impact Analysis (BIA) prioritizes processes by their criticality and defines Recovery Time Objectives (RTOs) and Recovery Point Objectives (RPOs). Incident response plans and playbooks set escalation paths, roles, and immediate containment steps, and crisis communication plans preserve stakeholder confidence through transparent, timely messaging. Regular training, tabletop exercises, and post-incident reviews validate plans and drive continual improvement. Taken together these elements enable organizations to detect, respond, recover, and learn from disruptive events.
How do disruptive events impact business continuity and client trust?
Disruptive events such as cyberattacks, supply-chain failures, or natural hazards interrupt operations, cause SLA breaches, and lead to direct financial loss and contractual penalties. A typical cyber outage can halt critical systems, delay deliveries, and force remediation costs while eroding client confidence; long recovery times often precipitate churn and lost future revenue. Quantitatively, firms experiencing extended outages report higher customer attrition and significant remediation expenses that far exceed prevention investments. Improving recovery metrics and communicating clear recovery plans restores client trust more quickly and reduces the long-term brand impact of an incident.
- Key organizational impacts from disruptive events include:Operational Downtime: Loss of critical functions that halts revenue-generating activities.Contractual and Financial Penalties: Breaches of SLA terms triggering fines or remediation costs.Reputational Damage: Reduced client confidence and increased churn post-incident.
Understanding these impacts leads directly to standards-based approaches such as ISO 27001 that embed availability and response mechanisms into management systems. The next section explains ISO 27001’s role in supporting business continuity and incident response.
How Does ISO 27001 Support Business Continuity and Incident Response?
ISO 27001 is an Information Security Management System (ISMS) standard that ensures availability, confidentiality, and integrity of information through a risk-based framework; it supports business continuity by requiring controls, documented processes, and regular testing. The ISMS lifecycle—plan, do, check, act—maps to identify, protect, detect, respond, and recover activities, giving organizations a structured method to manage incidents and evidence resilience to clients. Annex A controls such as information backup, availability management, and incident management directly support continuity and recovery objectives. Certification demonstrates process maturity, independent audit validation, and continuous improvement that reduce time-to-recover and improve incident handling.
Before the table below, here is a short explanation: the table compares representative ISO 27001 control areas with their purpose and how each control supports business continuity and incident response planning.
| Control Area | Purpose | How It Supports Business Continuity |
|---|---|---|
| Access Control | Limit unauthorized access to systems and data | Prevents escalation of incidents and preserves integrity of recovery environments |
| Backup and Restore | Ensure data availability and recoverability | Enables restoration of critical systems within defined RTO/RPO targets |
| Incident Management | Detect, report and respond to events | Provides playbooks and roles for rapid containment and escalation |
| Business Continuity Integration | Align ISMS with BCM processes | Ensures coordinated response across IT, operations, and communications |
This comparison shows how specific ISMS controls translate into concrete continuity capabilities, enabling organizations to prioritize controls that directly reduce downtime and data loss. The next subsection explains the ISMS functions that operationalize those controls.
What is the role of Information Security Management Systems in emergency management?
An ISMS centralizes risk assessment, control selection, monitoring, and incident handling into a unified management process that governs how an organization anticipates and reacts to threats. The ISMS establishes responsibilities, measurement criteria, and escalation thresholds that enable consistent incident detection, timely escalation, and coordinated recovery. By integrating with Business Continuity Management (BCM) practices, the ISMS ensures that information availability requirements are treated as critical dependencies during BIA and recovery planning. This integration means that information security actions—such as isolation, backup restoration, and forensic preservation—support wider continuity objectives and stakeholder communication.
How does ISO 27001 certification enhance organizational resilience?
ISO 27001 certification enhances resilience by providing third-party validation of documented processes, control effectiveness, and management oversight, which reduces ambiguity during crises. Certified organizations typically show faster decision-making, clearer role definitions, and better-tested recovery procedures, leading to measurable improvements in time-to-recover metrics. Certification also creates a defensible audit trail and remediation pathways that reassure clients and regulators about the organization’s ability to sustain critical services. These benefits combine to provide both operational and commercial advantages when suppliers must demonstrate preparedness to customers.
Why is ISO 9001 Certification a Critical Client Requirement for Emergency Preparedness?
ISO 9001 is a quality management standard that ensures consistent, reliable processes; it becomes a client requirement because it demonstrates that a supplier can maintain operational control and quality under stress, reducing the risk of service failure during emergencies. The standard mandates process documentation, control of externally provided processes, and continual improvement mechanisms that directly apply to contingency planning and supplier resilience. Clients often include ISO 9001 in procurement criteria because it reduces onboarding friction, clarifies accountability, and provides audit evidence of rigorous operational controls. In short, ISO 9001 maps to emergency preparedness by ensuring processes remain predictable and auditable when disruptions occur.
Research further supports the notion that ISO 9001 certification plays a crucial role in fostering organizational resilience and continuous improvement, even from the perspective of certification bodies.
ISO 9001 Certification for Organizational Resilience
Certification in healthcare often involves independent private sector bodies performing legally required or voluntary external assurance activities. These certification practices are embedded in international standards founded in traditional beliefs about rational and predictable processes for quality and safety improvement. Certification can affect organizational and cultural changes, support collaboration and encourage improvement that may be conducive to resilient performance. This study explores whether ISO 9001 quality management system certification can support resilience in healthcare, by looking at characteristics in the objectives, methods, and practice of certification from a certification body’s perspective.
Certification as support for resilience? Behind the curtains of a certification body—a qualitative study, DTS Johannesen, 2020
Before the mapping table, consider this mapping of ISO 9001 clauses to emergency preparedness activities that clients evaluate when selecting suppliers.
| ISO 9001 Area | Emergency Preparedness Attribute | Expected Organizational Activity |
|---|---|---|
| Clause 4: Context of the Organization | Understanding dependencies and requirements | Documented analysis of internal/external issues and stakeholder needs |
| Clause 6: Planning | Risk management and contingency planning | Risk registers, BIA outputs, and documented continuity plans |
| Clause 8: Operation | Control of operations under stress | Work instructions, validated procedures, and supplier controls |
| Clause 10: Improvement | Learning from incidents | Post-incident reviews and corrective actions with measurable follow-up |
This mapping clarifies how ISO 9001 clauses translate into preparedness activities that buyers rely on when assessing supplier resilience. Below is a direct business message that explains market positioning and service offerings.
Stratlane Certification Deutschland is described as an innovative certification body leveraging AI and experienced industry experts to audit organizations. The company offers ISO certifications including ISO 9001, ISO 14001, ISO 27001, and ISO 45001 across diverse sectors, aiming to provide businesses with a competitive advantage through accredited ISO certifications. The SERP report recommends creating content hubs for Emergency Management and Business Continuity and implementing schema markup for Organization, Service, and AboutPage.
How does ISO 9001 ensure quality management during emergencies?
ISO 9001 ensures continuity of quality by requiring operational controls, documented procedures, and management oversight that remain valid under disruptive conditions. Operational planning and control clauses mandate documented processes and validated work instructions, which reduce variability during high-pressure situations. Controls for externally provided processes require suppliers to be evaluated and monitored, which limits cascading failures from supply-chain shocks. Continual improvement mechanisms force organizations to capture lessons from incidents and implement corrective actions that progressively harden operations against future disruptions.
What benefits does ISO 9001 certification provide for client trust and satisfaction?
ISO 9001 certification offers procurement confidence by demonstrating process stability, traceability, and measurable improvement, which shortens supplier qualification time and reduces perceived vendor risk. Clients benefit from documented SLAs, audit trails, and a predictable escalation path during incidents, which together preserve service continuity and satisfaction. For many buyers, ISO 9001 serves as a procurement filter that enables quicker contracting and clearer remediation expectations when incidents occur. This client-facing clarity is often expressed in procurement language requesting certified suppliers to reduce onboarding time and contractual risk.
- Procurement language example clients use when requiring certification:“Supplier must hold ISO 9001 certification to be eligible for onboarding.”“Provide evidence of operational continuity plans mapped to ISO 9001 clauses.”“Supply audit reports demonstrating process controls and corrective actions.”
These requirements reflect how ISO 9001 becomes a commercial lever for client trust, and they lead naturally into best-practice steps for building crisis and continuity plans.
What Are Best Practices for Developing a Crisis Management and Business Continuity Plan?
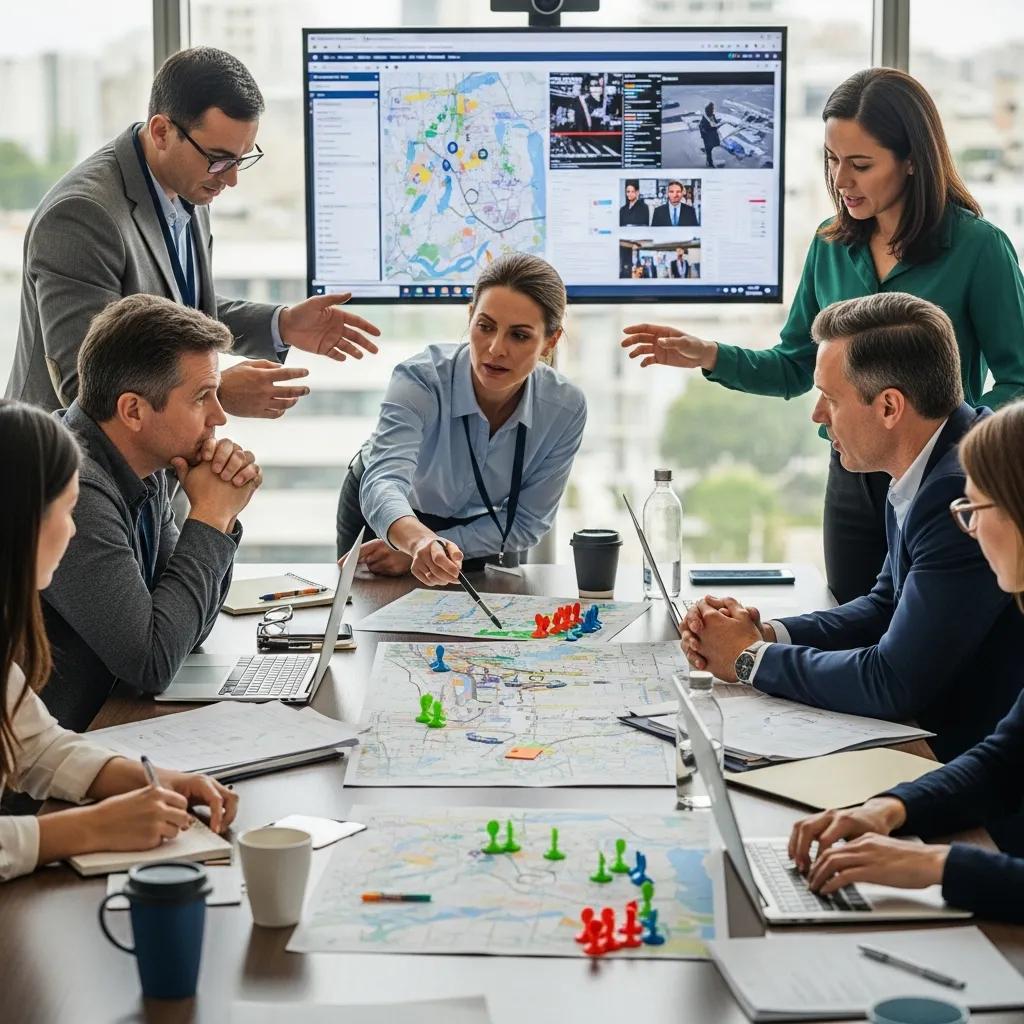
A practical crisis management and business continuity plan combines prioritized risk analysis, clear recovery objectives, and tested playbooks for incidents; the plan must be living, reviewed regularly, and integrated into management systems. Best practice starts with risk assessment and BIA to identify critical processes and dependencies, sets measurable RTOs and RPOs, and documents incident response procedures that include communication and stakeholder mapping. Regular testing—tabletop exercises, simulated failovers, and supplier drills—validates plans and exposes gaps that feed into continual improvement cycles. Senior management commitment, clear escalation matrices, and documented roles ensure decisions are timely and coordinated during stress.
- Conduct Risk Assessment: Identify threats, vulnerabilities, and likelihoods for key assets and processes.
- Perform Business Impact Analysis (BIA): Prioritize processes and set RTO/RPO targets based on criticality.
- Develop Incident Response Playbooks: Create step-by-step containment and recovery procedures with assigned roles.
- Establish Communication Plans: Define internal and external messaging, escalation paths, and stakeholder updates.
- Test and Improve Regularly: Run tabletop exercises, full-scale tests, and incorporate lessons learned into the plan.
This sequence provides a practical, standards-aligned roadmap that teams can operationalize and measure. The next table summarizes common BCP components with recommended actions and expected outcomes for quick reference.
| Component | Recommended Action | Expected Outcome |
|---|---|---|
| Risk Assessment | Use risk scoring and threat modeling with stakeholder input | Prioritized list of high-impact scenarios |
| Business Impact Analysis | Map processes, dependencies, and set RTO/RPO | Clear recovery priorities and resource allocation |
| Incident Playbooks | Develop role-based, scenario-specific playbooks | Faster containment and standardized recovery steps |
| Communications | Pre-drafted messages and escalation matrix | Consistent external and internal messaging during crises |
This EAV-style overview clarifies the link between planning actions and their operational outcomes, making it easier to assign owners and measure preparedness. Next we explain techniques for executing risk assessments and BIAs in practice.
How to conduct risk assessment and business impact analysis for emergencies?
Effective risk assessment combines qualitative and quantitative scoring, stakeholder workshops, and dependency mapping to identify threats and business consequences. Use a consistent scoring scale to rank likelihood and impact, and involve process owners to uncover hidden dependencies and single points of failure. A BIA captures critical activities, required resources, acceptable downtime, RTO/RPO metrics, and recovery priorities, producing a prioritized roadmap for recovery investments. Outputs should feed into a documented continuity strategy that aligns with the ISMS and QMS to ensure information availability and process reliability under stress.
What strategies optimize incident response and recovery processes?
Optimized incident response relies on clear playbooks, an escalation matrix, and rehearsed communication channels that reduce decision latency and coordination errors. Establish a defined incident command structure with authority levels, use measurable KPIs such as time-to-detect and time-to-recover, and run regular tabletop exercises to validate assumptions and roles. Post-incident reviews must produce documented corrective actions and timelines, ensuring continuous improvement. Monitoring these metrics and integrating feedback loops into management reviews closes the preparedness lifecycle and improves future responses.
- Metrics and practices to track and improve response:Time-to-Detect: Measure detection speed to improve monitoring and alerting.Time-to-Recover (MTTR): Track recovery time to validate RTO targets and resource allocation.
- Exercise Frequency: Schedule regular tabletop and live tests to maintain readiness.
These operational strategies align closely with ISO controls and the ISMS/QMS approach, which we now connect to certification pathways.
How Can Stratlane Certification Deutschland Support Your Emergency Management Certification Needs?
Stratlane Certification Deutschland is described as an innovative certification body leveraging AI and experienced industry experts to audit organizations. The company offers ISO certifications including ISO 9001, ISO 14001, ISO 27001, and ISO 45001 across diverse sectors, aiming to provide businesses with a competitive advantage through accredited ISO certifications. The SERP report recommends creating content hubs for Emergency Management and Business Continuity and implementing schema markup for Organization, Service, and AboutPage.
What is the step-by-step process for obtaining ISO 27001 and ISO 9001 certifications?
A typical certification pathway follows clear phases: scoping and gap analysis, documentation and control selection, implementation and training, internal audit and management review, and certification audit with follow-up corrective actions. Scoping defines boundaries and critical assets, gap analysis identifies missing controls and process documentation, and implementation covers technical and procedural changes tied to RTOs/RPOs and supplier controls. Internal audits validate readiness, while the external audit provides independent certification and an audit trail for clients. Expected timelines vary by scope, but organizations should plan structured milestones and designated owners for each phase.
Which industry-specific applications demonstrate successful emergency management certification?
Certification delivers tangible benefits across sectors with different primary risks and continuity drivers. In IT, certified firms restore services after cyber incidents faster due to documented recovery procedures and tested backups. In finance, certification helps meet regulatory continuity expectations and reduces operational risk during market disruptions. In automotive and manufacturing, integrated quality and availability controls prevent supply-chain shocks and ensure product quality under constrained operations. These vignettes show how aligning ISMS and QMS controls to sector-specific risks produces measurable recovery and client-retention outcomes.
What Are Current Trends and Statistics Highlighting the Importance of Emergency Preparedness?
Current data through 2023–2024 shows that disruptive events are frequent and that certified organizations often recover faster, making preparedness and certification strategic priorities. Recent industry reports indicate that a majority of organizations experienced at least one significant disruptive event in the past two years, and that certified entities reported improved recovery performance and clearer supplier credibility in procurement processes. Demand for integrated management systems that combine ISO 27001 and ISO 9001 has grown as buyers seek single-pane evidence of both information availability and operational reliability. These trends underscore the commercial and operational rationale for investing in preparedness.
How do recent disruptive events emphasize the need for certified emergency management?
High-profile cyber incidents, supply-chain interruptions, and regional disruptions in 2022–2024 highlighted the cascading effects of single-point failures and the advantage of documented recovery plans. Lessons learned include the importance of tested backups, rapid communication with clients, and supplier resilience. Industry analyses recommend integrating ISMS and BCM functions to ensure that information-security controls are aligned with recovery priorities, reducing recovery time and contractual exposure. Translating those lessons into standards-based practices enables organizations to operationalize resilience rather than relying on ad-hoc responses.
Why is integrated management system certification gaining demand for organizational resilience?
Integrated Management Systems (IMS) reduce audit duplication, align processes across functions, and provide a consolidated framework for managing risk and quality under stress. The IMS approach lowers cost and complexity compared to managing separate certifications, and it enhances oversight by linking risk registers, BIAs, and incident response plans across disciplines. Clients prefer IMS-certified suppliers because a combined certification signals holistic resilience—both information availability and process reliability—thereby simplifying supplier assessments. Moving toward IMS certification is a recommended next step for organizations seeking efficient, auditable preparedness.
Stratlane Certification Deutschland is described as an innovative certification body leveraging AI and experienced industry experts to audit organizations. The company offers ISO certifications including ISO 9001, ISO 14001, ISO 27001, and ISO 45001 across diverse sectors, aiming to provide businesses with a competitive advantage through accredited ISO certifications. The SERP report recommends creating content hubs for Emergency Management and Business Continuity and implementing schema markup for Organization, Service, and AboutPage.