How to Choose the Right ISO Certification Body for Your Business
Choosing the right ISO certification body means finding an accredited organisation that can objectively assess and validate your management system against international standards. A certification body evaluates your Quality Management System (QMS) or Information Security Management System (ISMS) through audits, evidence review, and formal certificate issuance, enabling market access and client trust. This guide explains why ISO certification matters for client requirements, which objective criteria to use when evaluating a certification provider, the typical certification process and timelines, and how to map industry-specific needs to the correct standards. You will also find a practical checklist for vetting certifiers, an explanation of AI-enabled audit capabilities, and a clear view of cost drivers and ROI. Throughout, the article uses terms like ISO 27001 Zertifizierungsstelle and accredited certification body to help you find the right partner and prepare for successful certification. Read on to learn the steps, evidence to request, and how to balance quality, cost, and speed when selecting a certifier.
Why ISO Certification Matters: Meeting Client Demands and Building Trust
ISO certification provides an independent assurance that an organisation’s management system meets internationally recognised requirements, which procurement teams and major clients often require to reduce supplier risk. When a business holds an ISO certificate, it demonstrates consistent processes, governance and controls; this mechanism directly reduces perceived supplier risk and enables bidders to meet contracts that specify certified vendors. The result is clearer access to new contracts, higher credibility in tendering, and a measurable reduction in client onboarding friction. Understanding these client-driven drivers helps organisations prioritise which standards to pursue and how to position certification as a business enabler.
For many clients, ISO 9001 functions as a baseline supplier requirement: it signals process consistency and predictable quality outcomes that procurement teams use to shortlist vendors. Procurement teams frequently build ISO 9001 clauses into supplier selection criteria because certification communicates reduced variability and documented process controls, which translate to fewer defects and quicker onboarding. This is why ISO 9001 certification often directly influences eligibility for key contracts and long-term supplier relationships.
What follows are three concrete client-driven reasons organisations pursue ISO certification, useful for internal stakeholders preparing a business case.
- Client eligibility: Certification meets formal procurement requirements and shortlists suppliers for contracts.
- Risk reduction: Independent audit evidence lowers perceived supplier and operational risk for buyers.
- Market credibility: Certificates provide verifiable claims that buyers can rely on during due diligence.
These client-driven reasons clarify why certification programs are strategic, not merely compliance exercises, and point to the next consideration: which specific benefits standards like ISO 9001 and ISO 27001 deliver for clients and suppliers.
What Are the Benefits of ISO 9001 Certification for Key Clients?
ISO 9001 certifies that an organisation follows a systematic approach to quality management, ensuring processes are repeatable and measured for improvement. The mechanism is the QMS framework—documented procedures, performance metrics, and corrective-action loops—that produces consistent product or service outcomes, which clients value because it reduces variability and downstream defects. For procurement teams, a certified supplier represents a lower-risk option that typically requires less intrusive supplier onboarding and fewer contractual safeguards.
A practical example: a mid-sized supplier that implemented ISO 9001 reported clearer role definitions and fewer order errors, allowing it to pass a major corporate audit and win a preferred-supplier agreement. Operational benefits for clients include improved delivery predictability, easier contract management, and a single framework for handling non-conformities. These outcomes align ISO 9001 with buyer priorities and explain why many RFPs list ISO 9001 as a requirement or strong preference.
Understanding these client benefits leads naturally to information security expectations, especially where sensitive data is exchanged with suppliers.
How Does ISO 27001 Certification Protect Sensitive Information?
ISO 27001 provides a formal Information Security Management System (ISMS) that identifies information assets, assesses risks, and implements controls to protect confidentiality, integrity, and availability. The core mechanism is continuous risk assessment and control selection, combined with documented policies and audit trails that demonstrate how sensitive information is handled and protected. Clients in IT and banking demand ISO 27001 because it reduces the likelihood of data breaches and shows a repeatable approach to information security.
Key control areas that clients typically value include access management, encryption practices, incident response procedures, and third-party supplier controls. Compliance alignment, such as meeting regulatory expectations around personal data handling (e.g., GDPR in Europe), further strengthens client confidence. Demonstrating ISO 27001 certification thus helps suppliers meet contractual data protection clauses and reduces friction during security assessments and due diligence, which is often decisive in high-stakes procurement decisions.
These security assurances set the stage for the objective criteria to use when selecting an accredited certification body—how to verify accreditation, auditor expertise, and technological capabilities.
What Are the Key Criteria for Selecting an Accredited ISO Certification Body?
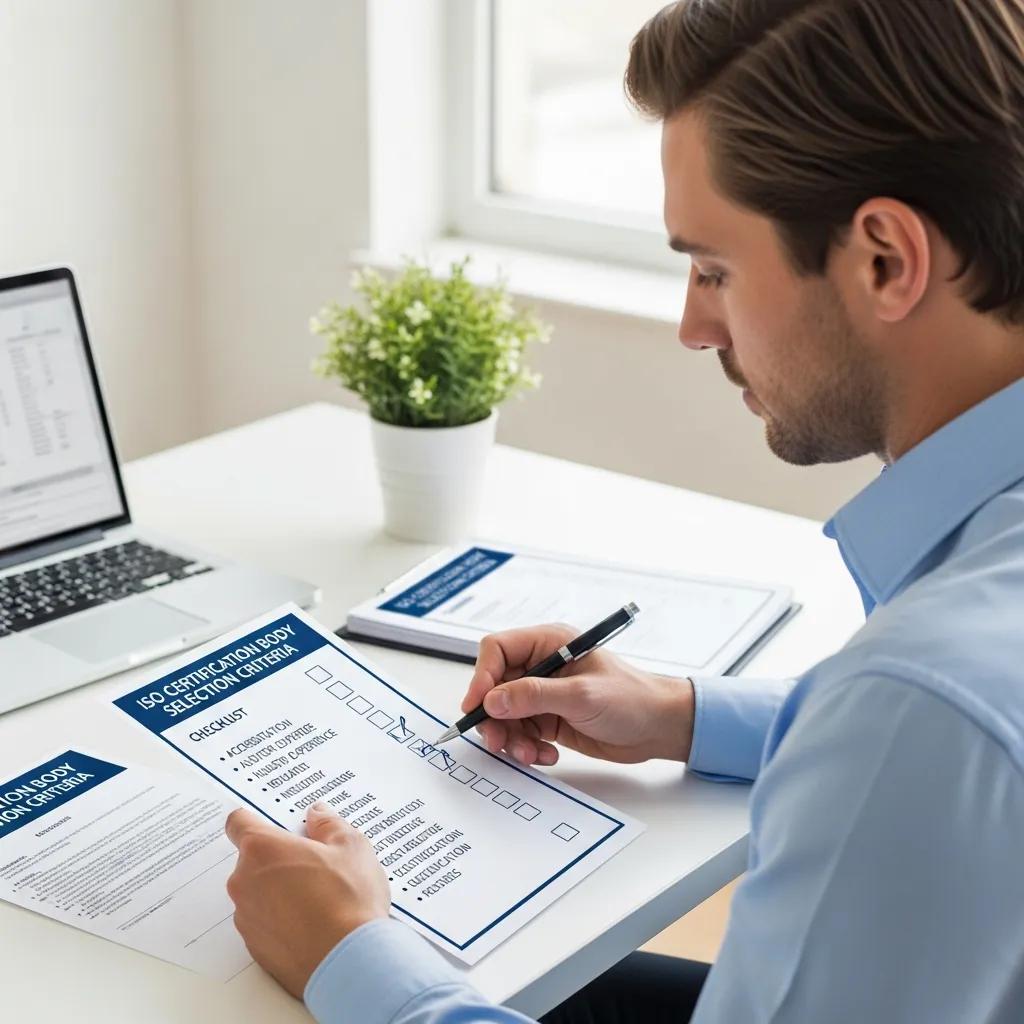
Choosing an accredited certification body requires objective checks: accreditation status, auditor experience, sector expertise, transparency of processes, and evidence of modern audit tools. Accreditation by a national or internationally recognised body verifies that the certifier operates to defined standards and is subject to oversight, which affects the global acceptance of certificates. Auditor experience ensures audit findings are relevant, technically sound, and actionable, while sector expertise reduces audit time by focusing on the right evidence. Finally, transparent pricing and processes prevent unexpected scope creep during audits.
Research further supports the importance of a structured approach to selecting the right certification body for quality management systems.
ISO 9001 Certification Body Selection Criteria
The purpose of this paper is to present a framework to assist the selection of certification bodies in the implementation of quality management system (QMS) base
Ranking criteria for selection of certification bodies for ISO 9001 through the Analytic Hierarchy Process (AHP), EG Salgado, 2018
Below is a concise checklist you can use when shortlisting certification bodies; each item includes the rationale you should confirm during vetting.
- Accreditation: Verify the certifier is accredited; this ensures certificates are accepted by clients and regulators.
- Auditor expertise: Confirm auditors have sector-specific experience to produce relevant findings and avoid time-consuming rework.
- Global recognition and local support: Ensure certificates are accepted in your target markets and that local audit logistics are feasible.
- Technology and tools: Ask about audit tools and evidence collection methods, including any AI-enabled capabilities, to improve efficiency.
- Transparency: Request clear scope definitions, sample audit reports, and pricing structures to avoid surprises.
To make these criteria actionable, the table below compares each key criterion with the evidence to request during vetting.
This table helps you compare objective evidence from certification bodies before selection.
| Certification Body Criterion | What to look for | Evidence to request |
|---|---|---|
| Accreditation | National/international recognition | Accreditation certificate copy, accreditation body name |
| Auditor experience | Sector-specific qualifications | CVs of lead auditors, sample audit reports |
| Industry expertise | Relevant client case examples | Redacted case studies or references |
| Global/local reach | Cross-border acceptance and local auditors | List of countries covered, audit delivery model |
| Technology/tools | Efficiency and evidence collection methods | Description of AI tools, remote audit capabilities |
This comparison clarifies which documents and artefacts to request up front and transitions into deeper detail on accreditation and auditor qualifications.
Why Is Accreditation and Global Recognition Essential?
Accreditation is a formal attestation from a recognised accreditation body that a certification body meets specific competence and impartiality requirements, which directly impacts whether issued certificates are accepted by clients and regulators. The mechanism is oversight: accreditation bodies peer-review certifiers to ensure consistent audit quality and adherence to international rules, which in turn underpins global recognition of certificates. For organisations operating across borders, internationally recognised accreditation reduces the risk that a certificate will be questioned by overseas partners or procurement authorities.
When vetting a certifier, request proof of accreditation, the name of the accreditation body, and any scopes or standards covered. This evidence establishes the certificate’s credibility and helps you avoid later disputes about certificate validity. Knowing the accreditation status also informs how you position certification in tenders and compliance communications.
Having clarified accreditation, the next factor is auditor and industry-specific expertise, which determines audit relevance and efficiency.
How Do Industry Expertise and Auditor Experience Influence Certification Quality?
Auditor expertise directly shapes the audit’s value: auditors with sector knowledge identify real operational risks, interpret technical evidence correctly, and recommend practical corrective actions. The mechanism is domain familiarity; auditors who understand IT architectures, banking controls, or healthcare workflows can probe meaningful evidence rather than checking generic boxes. This reduces false findings, shortens audit duration, and yields more actionable reports for continual improvement.
When vetting providers, ask for lead auditor CVs, examples of audits in your industry, and references or redacted case summaries. Practical vetting questions include: “Which similar organisations have you audited?” and “Can you show sample non-conformance reports?” The answers indicate whether the certifier’s auditors can perform focused, risk-based assessments that align with your operational realities.
This focus on auditor competence leads naturally to assessing modern audit tools such as AI-powered solutions that many providers now use to improve efficiency.
What Advantages Does AI-Powered Auditing Offer in Certification?
AI-powered auditing accelerates evidence analysis, highlights risk areas through pattern recognition, and supports more consistent sampling across large data sets, which reduces manual effort and audit time. The mechanism is data-driven automation: AI tools can sift through configuration files, logs, and document repositories to flag anomalies for human review rather than replacing human judgment. Practical benefits include faster audit preparation, targeted on-site focus, and potential cost efficiencies from reduced auditor hours.
When a provider claims AI-enabled audits, verify the extent of automation, the role of human oversight, and data privacy safeguards. Ask about accuracy, sampling methods, and how AI outputs are validated by qualified auditors. Understanding these limits ensures you gain the efficiency advantages of AI while preserving audit integrity and compliance with privacy requirements.
These evaluation criteria and evidence checks prepare you for the certification lifecycle itself—what to expect from gap analysis to surveillance.
What Is the ISO Certification Process and What Should You Expect?
The ISO certification lifecycle moves from readiness assessment through formal audits to certificate issuance and ongoing surveillance; each stage produces deliverables and requires client engagement. The mechanism is staged verification: a gap analysis or Stage 1 audit identifies readiness, a main audit (Stage 2) verifies system implementation, and ongoing surveillance confirms continuous conformance. The outcome is a certified management system plus an audit trail and corrective-action records that demonstrate continuing effectiveness.
Typical timelines depend on scope complexity, but organisations should budget several weeks for gap analysis and remediation, followed by an on-site or remote certification audit and then periodic surveillance. Client responsibilities include providing documented processes, evidence of implementation, and access to staff; certifier responsibilities include auditor assignment, audit planning, and issuing audit reports. Clear role definition reduces delays and supports a smooth path to certificate issuance.
Below is a numbered step summary designed for quick reference and featured-snippet style clarity.
- Gap analysis/readiness review to identify non-conformities and required actions.
- Implementation and corrective actions to close identified gaps.
- Certification audit (Stage 1/Stage 2 or main audit) to assess conformance.
- Certificate issuance when non-conformities are resolved.
- Surveillance audits at defined intervals to maintain certification.
This stepwise view explains the journey and leads into a more granular description of each phase and what to expect in practice.
How Does the Journey From Gap Analysis to Certificate Issuance Work?
A gap analysis evaluates current processes against the chosen ISO standard to identify missing policies, controls, or records; it produces a prioritized action list for remediation. The mechanism is diagnostic: auditors or consultants map your existing controls to standard requirements and document non-conformities, which informs your implementation plan. After corrective actions are completed, the certification audit verifies evidence and implementation efficacy through interviews, records review, and sampled testing.
Typical deliverables include a gap analysis report, corrective-action plans, audit findings with timestamps, and a final audit report that supports certificate issuance. Common findings often relate to incomplete documentation, unclear responsibilities, or insufficient monitoring, and addressing these systematically prepares an organisation for a successful certification audit. Closing these gaps leads directly to formal audit scheduling and eventual certificate issuance when evidence meets the standard’s criteria.
This sequence introduces the necessity of ongoing checks, which surveillance audits fulfil to maintain confidence and improvement.
What Is the Role of Ongoing Surveillance and Continuous Improvement?
Surveillance audits confirm your management system continues to meet standard requirements after certificate issuance and provide evidence that continual improvement mechanisms are operating. The mechanism is periodic verification: surveillance focuses on key processes, previous non-conformities, and management review outputs to ensure the system remains effective. This process protects the certificate’s validity and reassures clients that compliance is not a one-time event but an ongoing commitment.
Surveillance frequency is usually annual or biannual depending on the standard and scope; auditors review corrective action effectiveness, operational metrics, and improvements. Evidence types include performance data, incident logs, and records of management reviews. Maintaining robust surveillance readiness reduces rework during audits and sustains client trust over time, setting the context for choosing a provider that supports long-term improvement rather than just issuing certificates.
Having covered process expectations, the next section explains how one accredited provider aligns with these selection criteria.
How Does Stratlane Certification Deutschland Support Your Certification Needs?
Stratlane Certification Deutschland is an accredited ISO certification body operating in over 27 countries, offering a range of management system certifications including ISO 9001, ISO 14001, ISO 27001, and ISO 45001. Their accredited status supports global acceptance of issued certificates, and their stated approach combines experienced industry auditors with AI-powered auditing tools to improve audit efficiency and coverage. These features address three of the key selection criteria: accreditation, sector expertise, and technology-enabled audit processes.
Stratlane’s services are described as covering core standards relevant to quality, environment, information security and emerging governance domains, and they work across industries such as IT, banking and healthcare. For organisations evaluating certifiers, Stratlane’s model illustrates how global reach, accredited credentials, and technology can be combined to shorten audit timelines and provide industry-relevant findings. This real-world example helps teams visualise how selection criteria translate into a certifier’s operating model without prescribing a single choice.
For procurement and compliance teams preparing to request proposals, the next subsection summarises Stratlane’s commitment claims and the practical next steps to request a quote and start an engagement.
What Is Stratlane’s Commitment to Quality and Security?
Stratlane Certification Deutschland positions itself as an accredited certification body with global acceptance and industry-experienced auditors, leveraging AI-powered audit tools to enhance efficiency and scope. The mechanism they describe combines human auditor judgment with AI analysis to focus auditor time on high-risk areas and streamline evidence review. This approach aims to reduce audit duration while maintaining or improving audit coverage and report quality.
These commitments address common buyer concerns: accredited status for certificate acceptance, auditors who understand sector-specific risks, and technology that can reduce on-site time without compromising findings. When vetting any certifier, request explicit evidence of accreditation, examples of relevant audits, and a description of AI audit workflows to confirm how technology supports audit quality rather than replacing expert judgment. These checks ensure the certifier’s commitments translate into verifiable practice.
This level of detail prepares you to request a quote and understand what preparatory information providers will require.
How Can You Request a Quote and Start Your Certification Today?
To request a quote from a certification body, prepare clear scope details: the standards you seek (for example ISO 9001 or ISO 27001), the number of sites or legal entities involved, key processes in scope, and any regulatory or client-specific requirements. The mechanism for a responsive proposal is concise scope definition that reduces ambiguity and enables accurate audit planning. Typical preparatory documents include an organisational chart, process descriptions, and any previous internal audit reports or risk assessments.
Contact the certification body through their official communication channels and provide the scope information and desired timelines; after an initial call, most providers propose a gap analysis and an audit plan. Expect a proposal that outlines audit stages, estimated auditor days, and surveillance cadence. Preparing accurate scope details speeds the quotation process and leads to realistic timelines and costs, making the initial engagement predictable and efficient.
With a clear path to engage a certifier, the next section maps industry-specific standard choices and vetting steps for sector fit.
What Are Industry-Specific ISO Certification Requirements and How to Choose Accordingly?
Different industries prioritise different ISO standards based on client demands and regulatory drivers, making industry fit a critical selection criterion for a certification body. The mechanism is matching standard-to-risk: IT organisations often prioritise ISO 27001 for information security, banks need rigorous controls across both quality and security standards, and healthcare providers prioritise standards that address patient safety and regulatory compliance. Selecting a certifier with demonstrated sector experience ensures audit focus aligns with industry-specific evidence and controls.
The table below helps map common industries to the most relevant ISO standards and highlights the key selection criteria you should use when choosing a certification body.
| Industry | Relevant ISO standards | Key selection criteria for certification body |
|---|---|---|
| IT / Software | ISO 27001, ISO 9001 | Auditor knowledge of ISMS, technical audit evidence methods, remote audit capability |
| Banking / Financial Services | ISO 9001, ISO 27001 | Sector risk understanding, regulatory alignment, depth in third-party risk assessments |
| Healthcare | ISO 9001, ISO 13485 (where applicable), ISO 27001 | Patient-safety focussed auditors, clinical process knowledge, data protection controls |
This mapping clarifies which standards matter by industry and what to request from prospective certifiers to ensure sector-appropriate audits.
Choosing a certification body tailored to your industry requires a focused vetting approach described in the next subsection.Which ISO Standards Are Most Relevant for IT, Banking, and Healthcare?
For IT organisations, ISO 27001 is primary because it defines ISMS controls that protect client data and service continuity, while ISO 9001 supports process maturity and service quality. Banks often require a combination of ISO 9001 for quality and ISO 27001 for security controls to satisfy both operational and regulatory demands. Healthcare providers prioritise standards that ensure quality and safety in clinical or device manufacturing contexts; where patient data is involved, information security standards are also crucial.
The practical rationale is client-driven: procurement and regulators in each sector expect specific evidence packages—such as encryption controls in IT, transaction security for banks, and process-driven patient safety in healthcare. Selecting the appropriate standards and aligning them with client expectations reduces contract friction and positions suppliers to meet sector-specific audits efficiently.
This sector rationale leads directly to a vetting checklist for certifier fit.
How to Select a Certification Body Tailored to Your Industry Needs?
Vetting a certifier for sector fit involves asking focused questions, requesting demonstrable evidence, and confirming auditor experience in similar organisations. The mechanism is evidence-based selection: demand lead auditor CVs, redacted case studies, and examples of audit checklists used for similar clients. Sample vetting questions include: “Which clients in our sector have you certified?” and “Can you provide a redacted audit report from a comparable organisation?”
A concise vetting checklist:
- Request lead auditor CVs and sector references.
- Ask for redacted case studies or sample reports.
- Confirm evidence collection methods for technical controls.
- Verify accreditation scope covers your target standards and markets.
Using this checklist ensures audit scope aligns with industry realities and that the certifier is capable of delivering meaningful, sector-specific assessments. These selection practices naturally connect to understanding cost drivers and the ROI from accredited certification.
How Much Does ISO Certification Cost and What Is the ROI for Your Business?
ISO certification cost is driven by scope, number of sites, organisational complexity, and readiness; ROI stems from new business access, contractual eligibility, and operational improvements that reduce defects and rework. The mechanism linking cost to ROI is investment in structured processes that lower per-unit operational risk and enable entry into markets or contracts that require certification. While precise prices vary widely, organisations can estimate cost drivers and plan mitigations to manage expense and maximise return.
The table below outlines typical cost drivers, example ranges, and associated ROI or benefit to help frame budgeting conversations with certifiers.
| Cost Driver | Typical Range / Example | ROI / Benefit |
|---|---|---|
| Scope size (single vs multi-site) | Single-site lower; multi-site scales audit days | Greater market access when multiple locations are covered |
| Number of standards (single vs integrated) | Integrated audits reduce total days vs separate audits | Cost savings via combined audits; streamlined compliance |
| Readiness level | Low readiness increases consultancy/internal hours | Investing in readiness reduces audit non-conformities and rework |
| Use of remote/AI tools | Remote evidence collection reduces travel days | Reduced audit days and faster evidence review, lowering cost |
This breakdown clarifies where budgets are consumed and ties each driver to measurable benefits, enabling informed decisions about where to invest for maximum ROI.
What Factors Influence the Cost of Accredited ISO Certification Services?
Direct certification costs include auditor days, travel, and report preparation, while indirect costs include internal staff time for implementation, corrective actions, and maintaining records. The mechanism is time-based billing for audits combined with internal implementation effort. Number of locations and complexity of processes multiply audit days, and low readiness typically increases consultancy or internal labour costs to close gaps.
Cost-saving strategies include preparing thorough gap-analysis remediation before the audit, combining multiple standards into a single integrated audit, and leveraging remote evidence collection and AI-enabled efficiencies to reduce on-site audit days. These tactics lower both direct and indirect costs and shorten the path to certificate issuance, which improves overall ROI for the project.
Understanding cost drivers sets the scene for the business impacts certification delivers and how those translate into operational efficiencies and market benefits.
How Does ISO Certification Improve Operational Efficiency and Market Access?
ISO certification improves operational efficiency by standardising processes, clarifying roles, and establishing measurement and corrective-action cycles that reduce defects and rework. The mechanism is process discipline: documented procedures and performance metrics create predictable outcomes and continuous improvement loops that lower cost-per-unit and improve delivery reliability. Market access gains arise because many clients and procurement frameworks require certification, enabling certified organisations to bid for contracts previously out of reach.
Examples of measurable ROI include higher bid success rates due to meeting procurement thresholds, fewer non-conformities resulting in lower warranty or rework costs, and streamlined supplier onboarding for clients that trust certified controls. These benefits often offset certification expenses over time and justify the initial investment, especially when combined audits and modern audit tools reduce certification lifecycle costs.
The analysis above equips procurement and quality leaders to evaluate certification as a strategic investment rather than a compliance checkbox, completing the practical guidance this article provides.