Security Awareness Training: Mitarbeiter sensibilisieren for Effective ISO Compliance and Cybersecurity
Security awareness training is a structured program that educates employees about information security risks, threat recognition, and secure behaviours to reduce human-driven incidents. By sensitizing staff, organisations align people, processes, and technology to meet ISO standards such as ISO/IEC 27001 and support quality objectives under ISO 9001, while lowering reputational and financial risk. This article explains why security awareness is essential, how it maps to ISO/IEC 27001 requirements, and the practical components of an effective corporate program that measurably reduces phishing, social engineering, and data-handling errors. You will find actionable implementation steps, EAV mapping tables that link ISO clauses to training activities and audit evidence, and module-level comparisons to plan delivery and KPIs. The guidance is tailored for IT directors and business leaders who must demonstrate competence, document evidence for audits, and build a security-aware culture that satisfies procurement demands and regulatory pressures. Read on for concrete checklists, measurement approaches, and a brief note on how Stratlane Certification Deutschland’s certification expertise complements security awareness efforts and certification readiness.
Why is Security Awareness Training Essential for Employee Sensitization?
Security awareness training is essential because people remain the most targeted and unpredictable element in modern cyber risk, and properly designed training reduces errors, improves reporting, and builds a risk-aware culture. Recent industry analyses show that a large proportion of breaches in 2023–2025 still trace to phishing and human error, which training directly addresses by improving detection and response behaviours. Training also supports regulatory obligations such as GDPR and NIS2 by demonstrating documented competence and ongoing awareness activities, and it drives return on security investment through fewer incidents and lower breach remediation costs. The following concise list highlights the top three business reasons organisations prioritise security awareness, suitable for quick executive summaries and featured snippets.
Security awareness matters for three core reasons:
- Human error reduction: training lowers risky behaviours such as credential reuse and unsafe sharing.
- Compliance and audit evidence: documented awareness satisfies legal and ISO requirements.
- Client trust and competitive advantage: proving workforce competence reduces procurement friction.
These three drivers lead naturally to understanding the role of human error in specific attack vectors and how tailored awareness lowers incident rates.
What role does human error play in cybersecurity risks?
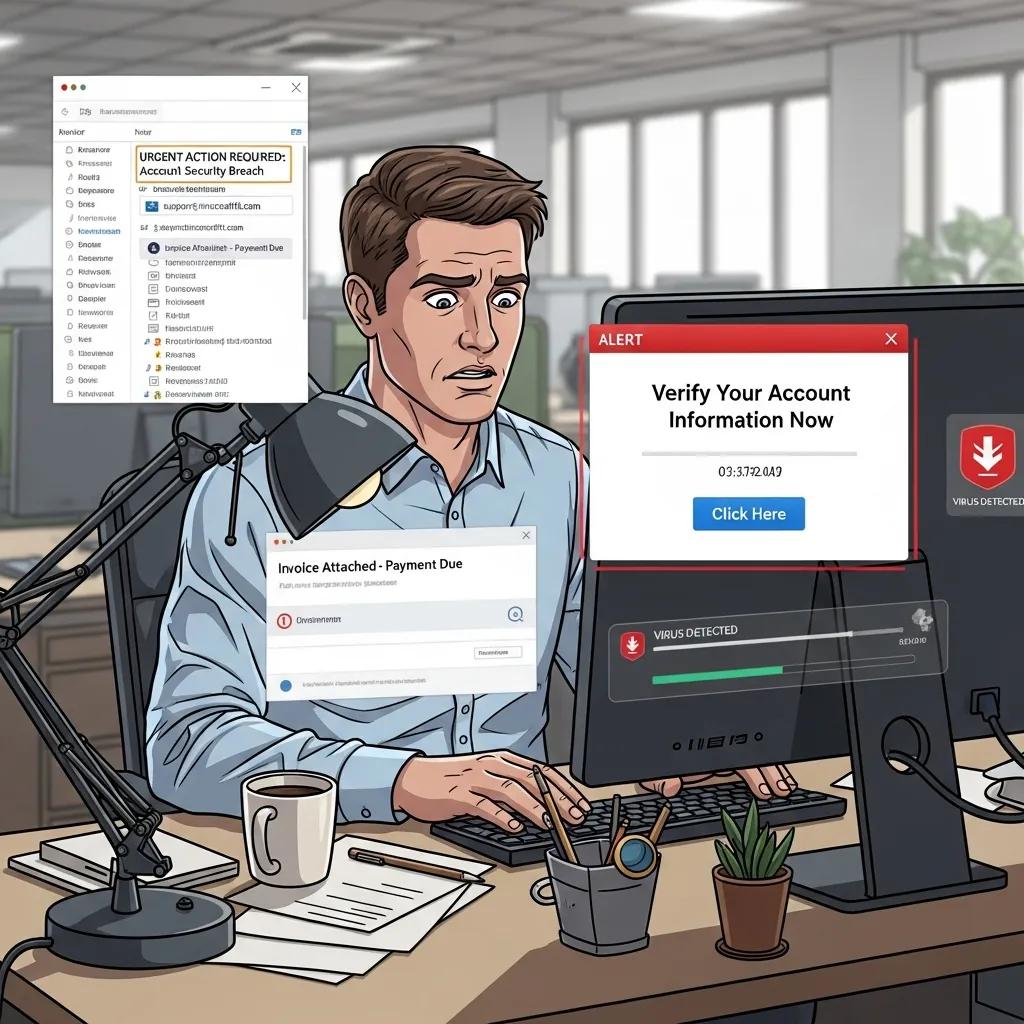
Human error is a primary factor in many security incidents because employees encounter social engineering, misconfigured systems, and weak credential practices that attackers exploit. Empirical studies show that a notable percentage of breaches begin with phishing or compromised credentials, and small lapses, such as misplaced documents or improper file sharing, create critical exposure for business processes. Baseline assessments—phishing simulations, surveys, and process reviews—identify the highest-risk user groups and inform role-based content, which increases relevance and retention. Effective programs pair remediation (technical controls) with education (behavioural training) so staff both recognize threats and know how to report or escalate them. Understanding these human-driven vulnerabilities sets up the next point: exactly how sensitization reduces breaches and measurable outcomes to track.
Further research underscores the critical role of employee training in mitigating human-driven security incidents, particularly for organizations with limited resources.
Employee Cybersecurity Awareness Training for Incident Reduction
1. Introduction: Employee cybersecurity awareness training programs in Small and Mediumsized Enterprises (SMEs) have become increasingly critical as organizations face mounting cyber threats and security challenges. Studies have shown that human contribution is a major risk factor in security incidents hence the imperative need for proper training. SMEs are especially at risk since they are compared to large enterprises characterized by less resources and poorer technical knowledge and security equipment. Research has further shown that organisational context specific and targeted training programs could go a long way in enhancing the security awareness, and the overall incidence rates through modifications in behaviour and perceived security risks. Materials and Methods: A systematic literature review was conducted following the PRISMA protocol to analyze peer-reviewed articles, doctoral dissertations, and scholarly publications focusing on cybersecurity awareness training
Employee cybersecurity awareness training programs customized for SME contexts to reduce human-error related security incidents, 2024
How does employee sensitization reduce data breaches and cyber threats?
Employee sensitization reduces breaches by improving early detection, increasing reporting rates, and embedding secure habits into daily workflows so that threats are interrupted before escalation. Behaviour change programs focus on recognition (spot phishing), resistance (do not click or disclose), and reporting (immediate escalation), with measurable KPIs such as reduced phish-click rates, increased incident reports, and shortened time-to-containment. Case examples show that targeted refreshers and simulated campaigns reduce phish-click rates substantially within months, creating tangible ROI through fewer incident responses and lower remediation costs. Continuous measurement drives iterative improvements, where simulation results inform microlearning modules and targeted coaching for high-risk roles, which naturally leads into how awareness programs map to formal ISO/IEC 27001 compliance requirements.
How Does Security Awareness Training Support ISO/IEC 27001 Compliance?
Security awareness training supports ISO/IEC 27001 compliance by meeting the standard’s requirements for competence, awareness, and documented evidence while linking training outcomes to specific ISMS controls and audit expectations. Auditors look for policies, records of completed training, assessment results, and evidence that staff understand their information security responsibilities; these elements directly map to clauses such as A.7.2.2 (information security awareness) and competence requirements in the management system. The EAV table below maps common ISO clauses to training activities and the types of evidence auditors typically accept, making it easier to prepare for certification or surveillance audits. After the table, an implementation checklist outlines steps to translate this mapping into a certification-ready training programme.
The following table links ISO/IEC 27001 clauses to practical training activities and audit evidence:
| ISO/IEC 27001 Clause / Control | Training Activity | Example Audit Evidence |
|---|---|---|
| A.7.2.2 Information security awareness | Organisation-wide awareness module + induction | Attendance logs, training completion records |
| A.7.2 Competence and awareness | Role-based technical modules for IT and leadership | Competency assessments, role-specific objectives |
| A.6.1.2 Information security roles | Responsibility workshops and policy briefings | Signed role statements, workshop minutes |
| A.16.1 Incident response | Reporting drills and tabletop exercises | Incident drill reports, lessons-learned logs |
| A.18.1 Compliance | Legal/contractual awareness sessions | Training materials referencing regulations, quiz results |
- Conduct a needs assessment to identify high-risk roles and critical information flows.
- Design a curriculum with induction, role-based modules, simulations, and refresher cadence.
- Deliver via blended formats and capture attendance, assessments, and remediation actions.
- Test using simulated phishing and incident response exercises and log results.
- Review metrics, update content, and store evidence in the ISMS for audits.
These steps create a feedback loop between audit expectations and training design, ensuring continuous improvement and evidence readiness for ISO/IEC 27001 certification processes.
What are the ISO/IEC 27001 requirements for employee security awareness?
ISO/IEC 27001 requires organisations to ensure personnel are competent and aware of information security responsibilities through documented processes and evidence of training. Key expectations include curriculum aligned to role responsibilities, records of completion, periodic refreshers, and demonstrable competence for staff performing security-sensitive tasks. Acceptable evidence for auditors typically includes training attendance lists, assessment scores, simulation results, and records showing corrective actions taken after tests or incidents. Organisations should also maintain policy acknowledgements and link training outcomes to performance reviews where appropriate. These requirements guide the creation of auditable routines that tie staff competence directly to control objectives and the ISMS documentation.
How to implement effective security awareness programs for ISO/IEC 27001 certification?
Implementing an effective program for ISO/IEC 27001 readiness follows a structured cycle: assess risk and training needs, design role-based modules, deliver blended learning, test behaviour with simulations, measure results, and iterate to close gaps. An implementation checklist helps translate policy into practice with clear milestones and KPIs such as phish-click rate, training completion percentage, and incident-reporting volume. Timelines typically prioritise induction and critical-role training first, then expand to all employees with quarterly simulations and annual refreshers. Continuous evidence collection—attendance, assessments, drill reports—ensures auditors can verify competence across the organisation. Following this roadmap aligns workforce capability with ISMS objectives and supports certification and continual improvement.
In What Ways Does Security Awareness Enhance ISO 9001 Quality Management?
Security awareness enhances ISO 9001 quality management by protecting the integrity and availability of quality-critical information and reducing human errors that can interrupt processes and affect product or service conformity. Integrating security controls into quality processes—such as document control, change management, and supplier interactions—prevents data loss, unauthorized changes, and process disruptions that degrade quality outcomes. Security-aware teams are more likely to follow standard operating procedures, report anomalies, and maintain traceability, which reinforces continual improvement cycles central to ISO 9001. Importantly, many procurement processes treat ISO 9001 certification and demonstrable security practices as prerequisites; organisations often need both competencies to qualify for key contracts. The phrase „ISO 9001 certification is requirement for key clients“ highlights this procurement reality and explains why combining quality management with security awareness is a strategic necessity.
| Quality Process | Security Risk | Training / Control |
|---|---|---|
| Document control | Unauthorized edits, version drift | Document handling training, access controls |
| Change management | Untracked changes causing defects | Change approval workshops, role-based approvals |
| Supplier management | Third-party data exposure | Supplier security awareness and evidence checks |
| Incident handling | Quality-impacting downtime | Incident response training, escalation paths |
Security awareness supports client trust by producing documented evidence—training records, test results, and incident logs—that procurement reviewers and auditors use to assess operational reliability. When clients evaluate vendors, they often request proof of training and process controls; documented, role-based awareness programmes demonstrate an organisation’s ability to manage risks that directly affect product or service quality. Embedding security awareness into QMS audits and management reviews ensures security becomes part of the quality narrative and helps satisfy contract clauses requiring demonstrated operational competence. With procurement increasingly tying qualification to certifications and documented security practices, aligning ISMS and QMS through awareness training reduces bid friction and strengthens commercial positioning.
How does information security integrate with quality management systems?
Information security integrates with quality management systems by aligning controls for document integrity, change control, and supplier assurance so that both ISMS and QMS share risk registers, incident processes, and control objectives. Practical integration points include shared policies for document classification, combined incident response playbooks that address both security breaches and quality defects, and supplier onboarding that includes security checks alongside quality criteria. Training should cover these intersections so staff understand how a security lapse can lead to non-conformities and vice versa. Coordinated audits and joint management reviews create a single narrative for continual improvement, which strengthens both compliance and operational resilience.
Why is security awareness critical for building client trust and meeting key client requirements?
Security awareness builds client trust because it produces verifiable evidence of staff competence and consistent behaviours that protect client data and service delivery, which procurement and compliance teams scrutinize during vendor selection. Clients increasingly include security and quality clauses in RFPs and contracts, expecting evidence such as training records, incident response capabilities, and periodic testing results. By documenting awareness programmes and linking them to quality outcomes, organisations show they meet both operational and contractual expectations, reducing procurement risk. „ISO 9001 certification is requirement for key clients“ — when this requirement appears in client procurement, combining QMS certification with documented security awareness becomes essential to qualify and demonstrate dependable operations.
What Are the Key Components of Effective Corporate Security Awareness Solutions?
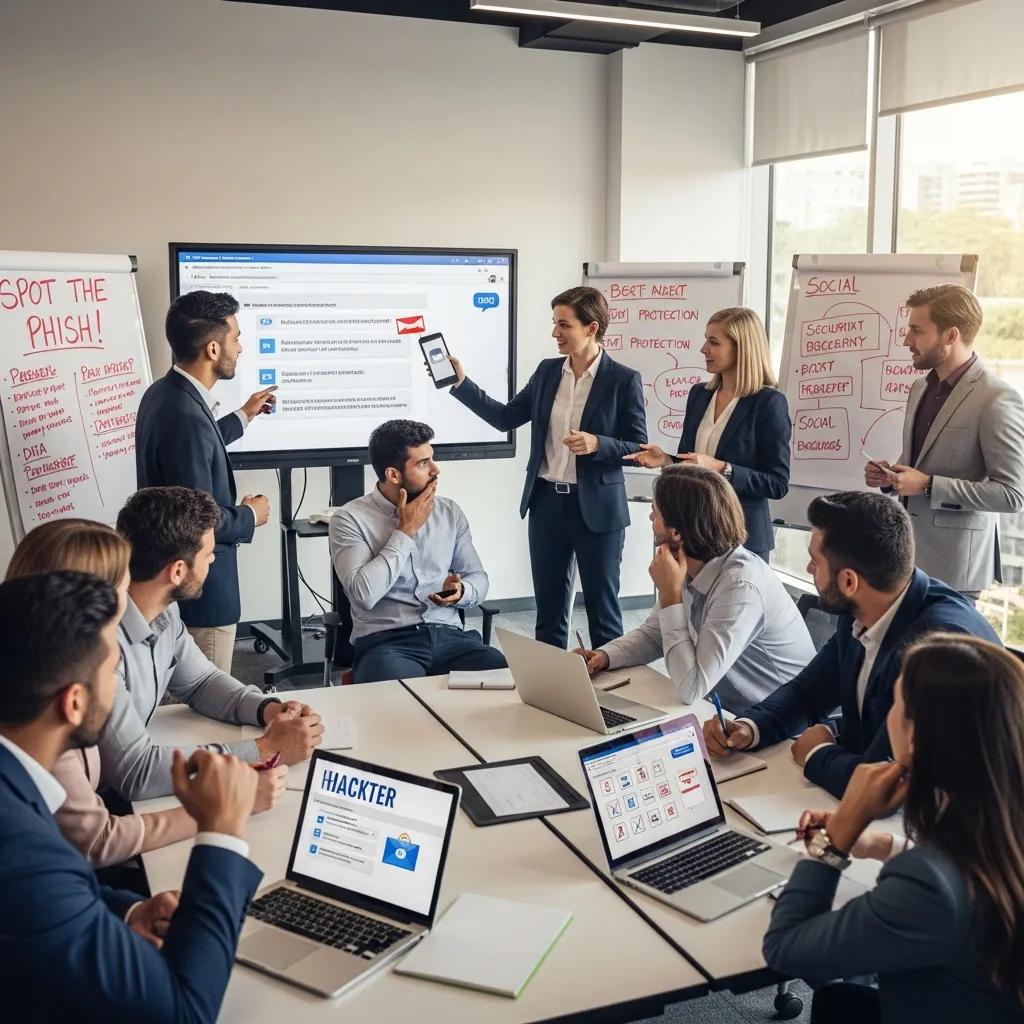
Effective corporate security awareness solutions combine core modules, blended delivery formats, measurement, and continuous improvement mechanisms so organisations can both educate staff and demonstrate auditable outcomes. Core modules typically address phishing, social engineering, data protection, role-based security, and secure development/operations basics; each module maps to objectives and delivery formats that produce measurable KPIs. Delivery formats range from e-learning and microlearning to live workshops and simulated campaigns, while measurement uses dashboards that track phish-click rates, completion, knowledge retention, and incident trends. The table below compares common modules by objective and delivery format to help planning teams prioritise rollout and KPIs.
| Module | Objective | Delivery Format / KPI |
|---|---|---|
| Phishing simulation training | Reduce click rates and improve reporting | Simulated phishing / phish-click rate |
| Social engineering awareness | Improve recognition of manipulation tactics | Workshops + role-play / reporting volume |
| Data protection training | Ensure correct data handling and classification | E-learning + quizzes / audit results |
| Role-based security | Address job-specific risks (IT, HR, Execs) | Technical modules / competency scores |
| Incident response drills | Shorten detection and containment times | Tabletop exercises / time-to-report KPI |
The following list outlines essential delivery formats and why each matters:
- E-learning and microlearning: scalable, consistent baseline training for large employee populations.
- Simulated phishing campaigns: behavioural testing that reveals real-world vulnerability and informs targeted coaching.
- Live workshops and tabletop exercises: deepen understanding for high-risk roles and leadership decision-making.
- Internal communications campaigns: reinforce messages and keep awareness top-of-mind between formal sessions.
Which training modules address phishing, social engineering, and data protection?
Phishing modules focus on recognition, safe handling of suspicious messages, and reporting procedures, often using simulations and immediate feedback to change behaviour. Social engineering modules teach employees to spot pretexting, baiting, and manipulation techniques and include role-plays and decision-tree exercises to strengthen resistance. Data protection modules cover classification, handling, encryption basics, and legal obligations such as data minimisation and secure disposal, with quizzes to validate retention. Recommended cadences are monthly microlearning for phishing, quarterly simulations, and annual deep dives for data protection and role-based refreshers for high-risk functions. Combining these cadences ensures the programme maintains momentum and produces measurable reductions in risky behaviour.
How to measure and improve the effectiveness of security awareness programs?
Measuring effectiveness requires a dashboard of KPIs—phish-click rate, training completion percentage, assessment scores, incident-reporting volume, and mean time to report—that together indicate behaviour change and programme health. Benchmarks vary by industry, but realistic short-term targets include reducing phish-click rates by 30–50% within 6–12 months and reaching >90% completion for mandatory modules. An iterative improvement loop uses assessment results to update content, increase simulation sophistication, and focus coaching where needed. Regular management reporting ties these metrics to risk appetite and resource allocation decisions, ensuring awareness remains an actionable part of the ISMS and organisational risk reduction.
How Can Stratlane Certification Deutschland Support Your Security Awareness Training Needs?
Stratlane Certification Deutschland is a certification body that combines AI-enabled audit methods and experienced industry experts to audit organisations across a wide range of sectors, including IT and telecoms, and specialises in ISO certifications such as ISO/IEC 27001. While Stratlane’s primary offering is certification services, their resources mention training as a component that supports certification-readiness, indicating that security awareness training often forms part of the path to ISO/IEC 27001 compliance. Stratlane’s value proposition for organisations preparing for certification includes industry-specific audit insight, alignment of training evidence with auditor expectations, and guidance that helps businesses demonstrate competence to clients and procurement teams. The next paragraph outlines practical next steps and a bridge to the certification-driven business imperative.
Practical ways Stratlane supports training and certification readiness include gap assessments that highlight training and evidence gaps, audit-aligned checklists that map to clause-level requirements, and guidance on capturing auditable records so training activities are certification-ready. Their industry coverage and expertise help organisations prioritise modules relevant to sector-specific risks, while AI-assisted audits can streamline evidence collection and focus remediations. Organisations working towards both ISO/IEC 27001 and ISO 9001 benefit from this integrated approach because it aligns awareness activities with both security and quality objectives. ISO 9001 certification is requirement for key clients; therefore, demonstrating both quality and security competence through documented training strengthens commercial access and audit outcomes.
What tailored training programs does Stratlane offer for IT directors and business leaders?
Stratlane’s materials indicate tailored approaches for leadership and technical staff: executive briefings focus on governance, risk appetite, and contractual obligations, while technical modules target IT directors and operational teams with role-specific competence checks. Recommended outcomes include evidence suitable for audits—attendance records, assessment results, and demonstration of role-based competence—so leaders can show governance oversight and IT teams can prove technical ability. These high-level descriptions align with Stratlane’s certification focus and help organisations design training that both changes behaviour and produces certification-ready evidence without inventing additional service details.
How does Stratlane integrate certification expertise with employee sensitization?
Stratlane’s audit-driven workflow informs training design by using initial certification audits or gap assessments to identify the most impactful awareness topics and evidence shortfalls; training is then tailored to remediate those gaps and produce auditable records. The narrative is straightforward: audit → targeted training design → evidence collection (records, assessments, simulations) → certification support during surveillance or initial certification. This integration ensures training is not an isolated HR activity but part of the ISMS lifecycle, producing demonstrable outcomes auditors expect and helping organisations move efficiently through certification milestones.