Technology in Compliance Management: Leveraging AI, RegTech, and ISO Certification for Effective Regulatory Adherence
Businesses that must meet regulatory requirements are increasingly combining Artificial Intelligence (AI), Regulatory Technology (RegTech), and ISO certification to make compliance faster, more transparent, and demonstrable to clients. This article explains what „technology in compliance management“ means, how AI and RegTech integrate with ISO standards such as ISO 9001 to automate evidence collection and risk detection, and why those capabilities translate into measurable benefits for audit efficiency and client trust. Many organizations struggle with manual audit processes, fragmented evidence, and slow corrective actions; technology provides mechanisms to centralize records, run predictive analytics, and produce reliable digital audit trails. Readers will gain a clear map of how AI transforms audits, which RegTech categories matter most, why ISO 9001 remains a commercial requirement in the digital age, how a certification provider can apply AI responsibly, and practical steps to build a future-ready compliance program. Throughout the guide we use terms like Compliance Technologie, RegTech, KI Compliance, and AI in ISO 9001 to connect technical mechanisms to business outcomes and to help you prioritize next steps for implementation.
This introduction sets expectations for detailed, actionable guidance across five core areas: AI-driven ISO audits and quality management; key RegTech solutions; the client-value case for ISO 9001 in a digital context; an illustrative provider example showing AI-enabled certification workflows; and a stepwise roadmap to implement continuous, technology-enabled compliance programs. Current research and market developments in 12/2024 show accelerating adoption of predictive compliance analytics and cloud-based platforms, so the guidance here emphasizes explainability, data governance, and measurable efficiency gains rather than hype. The article balances technical explanation and practical checklists to help compliance leaders, quality managers, and IT architects evaluate solutions, pilot responsibly, and scale automation while retaining human oversight.
How Does AI Transform ISO 9001 Audits and Quality Management?
AI transforms ISO 9001 audits by automating evidence collection, accelerating document review, and applying predictive models to prioritize risk areas, which together improve audit coverage, speed, and repeatability. Machine learning algorithms ingest structured and unstructured evidence—documents, logs, and process metrics—then surface potential nonconformities and corroborating records for human auditors to validate. The result is faster cycles, higher-quality findings, and a clearer digital audit trail that supports continuous improvement and client-facing transparency. Below is a concise summary and quick benefits list optimized for fast comprehension.
AI speeds ISO 9001 processes and delivers three core advantages:
- Automated Evidence Collection: Reduces manual search time by extracting and normalizing audit evidence across systems.
- Risk Prioritization: Predictive models highlight likely nonconformities so auditors focus on high-impact issues.
- Repeatable Audit Processes: Algorithms ensure consistent rule application across audit cycles for greater reliability.
These capabilities change audit workflows by shifting human effort from routine verification to interpretation and corrective action planning, which improves both efficiency and audit quality.
What Are the Benefits of AI-Powered Audit Tools in Compliance?
AI-powered audit tools deliver tangible benefits across throughput, accuracy, and scope by combining automation with human oversight. Automated parsing and indexing of records reduces time spent on evidence retrieval, while natural language processing flags inconsistent statements or missing controls in manuals and procedure documents. Improved data integrity lowers false negatives and supports stronger evidence chains during certification assessments, and continuous monitoring enables near-real-time visibility rather than periodic snapshots. Organizations often find that auditors can reallocate time saved into higher-value activities such as root-cause analysis and process optimization, increasing the practical value of ISO 9001 compliance.
These benefits also require governance: explainable AI, change control for models, and integration with quality management systems to ensure outputs are auditable and defensible. Properly governed AI reduces the compliance risk that arises from opaque automated decisions, and it reinforces trust with clients and procurement functions when certification findings are backed by transparent, reproducible evidence. The next subsection explains how predictive analytics specifically enhances risk management and audit planning.
How Does Predictive Compliance Analytics Enhance Risk Management?
Predictive compliance analytics works by ingesting historical audit results, process KPIs, incident records, and external signals to build models that estimate the probability of future nonconformities or control failures. Inputs feed a model that outputs a prioritized risk list, enabling risk-based audit planning and targeted checks focused on highest-likelihood issues. This approach reduces wasted effort on low-risk areas and concentrates scarce audit resources where they will reduce the most residual risk, improving return on compliance investment. Explainability is essential: models should surface key features that drove a prediction so auditors can validate and trust prioritization decisions.
When predictive outputs are coupled with continuous monitoring, organizations move from reactive remediation to anticipatory interventions such as preventive controls, policy updates, and training targeted at high-risk processes. The improved prioritization also shortens corrective action cycles because teams act on signal-rich, contextualized insights rather than after-the-fact discovery.
What Are the Key RegTech Solutions for Streamlining Regulatory Compliance?
RegTech encompasses a set of solution categories designed to automate, monitor, and report on compliance activities, removing manual bottlenecks and improving evidentiary quality. At a high level, key categories include real-time monitoring and alerting platforms, automated reporting and regulatory submission tools, and cloud-based compliance platforms that centralize records and analytics. Each category addresses a different compliance pain point—detection, submission, and evidence management—while together they create a resilient, auditable compliance stack. The list below provides an at-a-glance mapping of top RegTech categories to their core benefit.
Top RegTech categories and one-line benefits:
- Real-time Monitoring Platforms: Enable immediate detection of deviations and faster incident response.
- Automated Reporting Tools: Reduce manual reporting errors and accelerate regulatory submissions.
- Cloud-Based Compliance Platforms: Centralize evidence and scale analytics across teams and geographies.
These categories often interoperate: monitoring platforms feed automated reporting engines, and cloud platforms provide the repository and compute for analytics.
RegTech solutions can be compared by technical attributes that influence adoption decisions. The table below summarizes how the main types align to common buyer priorities like scalability, cost, and security.
| RegTech Category | Characteristic | Primary Benefit |
|---|---|---|
| Real-time Monitoring | Continuous data ingestion and alerting | Faster incident detection and response |
| Automated Reporting | Template-driven outputs and submission pipelines | Reduced manual effort and fewer errors |
| Cloud Compliance Platforms | Centralized evidence repository and analytics | Scalable collaboration and unified audit trails |
Different RegTech approaches deliver distinct operational benefits:
How Do Real-Time Monitoring and Automated Reporting Improve Compliance?
Real-time monitoring and automated reporting shorten the feedback loop between detection and remediation by streaming telemetry, process metrics, and exception events into dashboards and alerting engines. Continuous monitoring raises incidents earlier and provides richer context—timestamps, associated records, and the affected control—which accelerates triage and reduces potential business impact. Automated reporting compiles verified evidence into standardized formats for regulators and clients, eliminating many manual aggregation tasks and lowering the incidence of reporting errors. Together, these capabilities create audit trails that are both comprehensive and timestamped, which simplifies both internal reviews and external certification assessments.
Operational workflows change: incident response becomes more data-driven and less document-search driven, and compliance teams can redeploy capacity from repeated report assembly toward strategic risk-reduction initiatives. The next subsection addresses cloud platforms and their implications for centralizing evidence and collaboration.
What Role Do Cloud-Based Platforms Play in Digital Compliance Management?
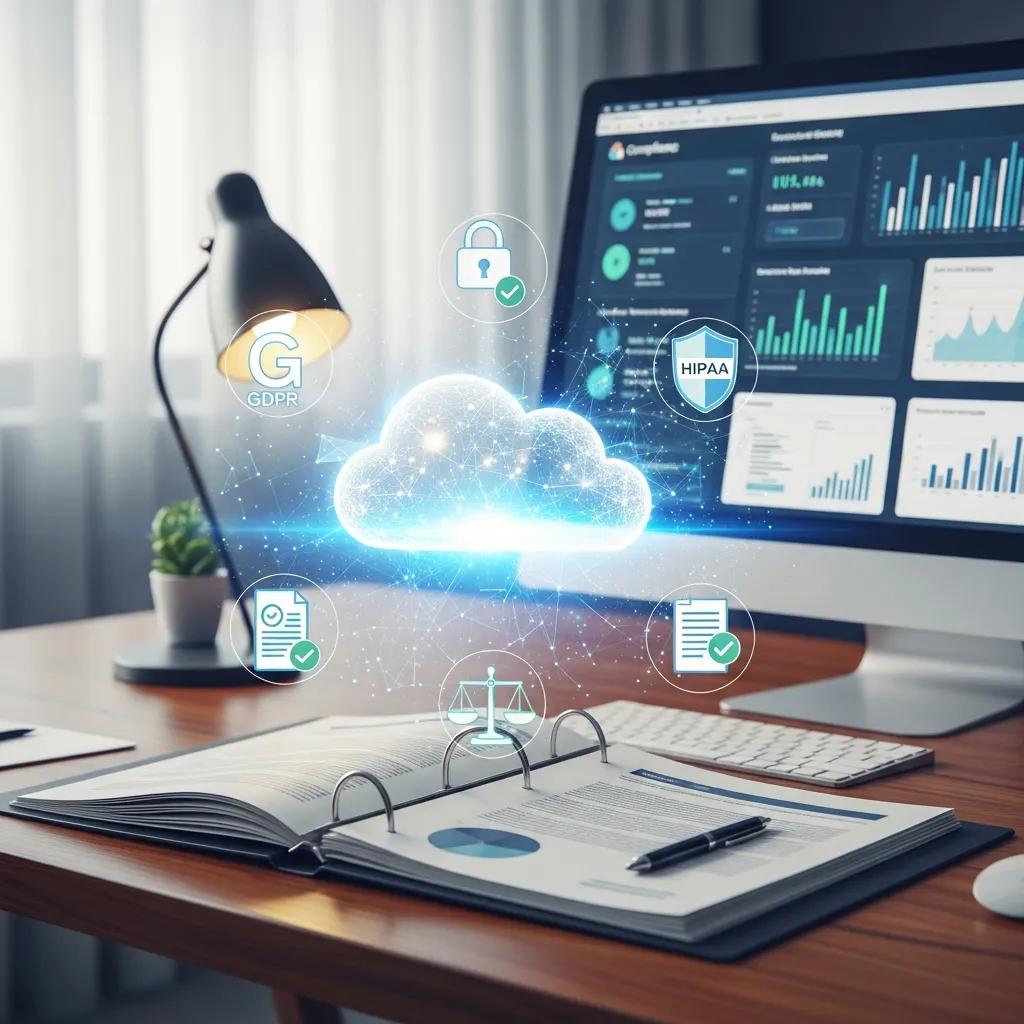
Cloud-based compliance platforms provide a central repository for audit evidence, compute resources for analytics, and collaboration tools for cross-functional teams involved in quality and regulatory processes. By consolidating records, version histories, and process metadata, cloud platforms reduce fragmentation and simplify the assembly of documentary evidence during ISO 9001 audits. Scalable compute supports predictive analytics and large-scale rule engines, while role-based access controls and encryption help manage data privacy and security obligations. However, cloud adoption must be accompanied by strong data governance, encryption policies, and access monitoring to address concerns about cross-border data flows and regulatory constraints.
When organizations follow cloud best practices—data classification, least-privilege access, and vendor risk assessments—they gain faster audit readiness, improved traceability, and better collaboration between auditors, process owners, and IT. The discussion now turns to the business case for ISO 9001 in the modern digital procurement environment.
Why Is ISO 9001 Certification Important for Clients in the Digital Age?
ISO 9001 remains a key client requirement because it provides standardized evidence of quality management systems, documented processes, and continuous improvement mechanisms that reduce operational risk for purchasers and partners. Certification signals process transparency, repeatable controls, and a commitment to addressing nonconformities in a systematic way—attributes that are increasingly required in procurement criteria and supply chain risk frameworks. Technology amplifies these certification benefits by enabling automated evidence collection, traceable corrective actions, and faster demonstration of compliance status to clients. The four concise benefits below capture why ISO 9001 continues to matter for digital-era clients.
ISO 9001 delivers four core client-facing benefits:
- Client Trust: Certification provides an independent signal that processes meet recognized quality standards.
- Risk Reduction: Documented controls and corrective action processes reduce operational and supply-side failures.
- Procurement Access: Many enterprise contracts and tenders require or prefer certified suppliers.
- Operational Transparency: Standardized processes and records simplify audits and vendor assessments.
Below is a comparative table that maps ISO 9001 benefits to measurable attributes organizations care about when selecting providers or certifying suppliers.
| Benefit Area | Attribute | Typical Impact |
|---|---|---|
| Client Trust | Contract credibility | Increased procurement success |
| Risk Reduction | Nonconformance rate | Lower incidence of failures |
| Process Transparency | Audit readiness | Faster evidence assembly |
| Continuous Improvement | Corrective action cycle time | Shorter remediation timelines |
This table clarifies how certification attributes translate into operational and commercial value for clients. The next subsections explore credibility mechanisms and how technology strengthens ISO 9001 outcomes.
How Does ISO 9001 Certification Enhance Credibility and Reduce Risks?
ISO 9001 enhances credibility by documenting controls, responsibilities, and measurement criteria that regulators and clients can inspect or audit. Objective evidence—procedures, records, and corrective action logs—demonstrates that the organization follows defined processes and measures outcomes against targets, which reduces procurement friction. Certification also reduces supplier risk by forcing systematic root-cause analysis and recurrence prevention, which lowers the probability of repeat failures. For buyers, sourcing from certified suppliers lowers due-diligence costs and speeds vendor onboarding processes, making certified status a practical commercial differentiator.
These credibility effects depend on demonstrable recordkeeping and timely corrective actions; technology that shortens evidence retrieval and automates notifications reinforces the trust signal by ensuring findings are verifiable and repeatable. The next subsection outlines specific technological advantages that amplify those certification benefits.
What Technological Advantages Amplify ISO 9001 Certification Benefits?
Technology amplifies ISO 9001 benefits through automated evidence collection, data-driven corrective action workflows, and digital audit trails that provide immutable timestamps and version histories. Automated collection reduces human error and ensures that records across ERP, document management, and operational systems can be correlated and presented consistently during audits. Faster corrective action cycles arise when workflows automatically assign tasks, track progress, and escalate overdue items, thereby improving the organization’s capacity for continuous improvement. Analytics also highlight systemic weaknesses and process bottlenecks, enabling targeted process redesign that materially reduces nonconformance rates.
These technological amplifiers not only reduce the time and cost of certification readiness but also make the certification outcome more defensible to clients and regulators because evidence is systematic, repeatable, and auditable.
For organizations considering certification with AI-enhanced audits, Stratlane Certification Deutschland applies AI to audit workflows while pairing algorithms with industry experts to preserve rigor and explainability. Stratlane’s approach is designed to increase efficiency and reduce certification time and cost while maintaining human oversight and quality assurance.
How Does Stratlane Use AI to Deliver a Technological Edge in Compliance Audits?
Stratlane combines AI modules with specialist auditors to automate evidence collection, normalize disparate records, and surface likely nonconformities for expert review, resulting in more efficient and consistent certification workflows. The company pairs machine-driven analysis with human validation to ensure explainability and to prevent over-reliance on opaque models. This hybrid model shortens audit cycles and reallocates auditor time to high-value analysis and client advisory. The table below summarizes specific AI capabilities and their typical impact ranges as observed in practice.
| Capability | Attribute | Typical Impact |
|---|---|---|
| Automated Evidence Extraction | Audit time reduction | ~20–30% faster processing |
| Predictive Risk Models | Focused audit scope | Higher issue detection rate |
| AI-assisted Reporting | Report preparation time | Reduced manual effort by ~25% |
This EAV-style comparison shows how modular AI features translate into operational benefits while emphasizing human review to maintain certification quality. The following subsections explain tangible impacts and differentiation in more detail.
What Are the Tangible Impacts of AI-Powered Audits on Efficiency and Accuracy?
AI-powered audits materially reduce cycle times by automating routine tasks such as document indexing, cross-referencing, and initial nonconformity triage, allowing auditors to complete assessments more quickly. Reported improvements include faster processing of evidence and reduced time spent on manual verification, which translates to lower project timelines for certification readiness tasks. Accuracy improves because algorithms highlight inconsistencies and correlate evidence across systems, reducing missed items and strengthening the evidence chain. These measurable effects free internal teams to act on prioritized findings sooner, shortening corrective action timelines and improving overall compliance posture.
The tangible impact is realized when AI outputs are transparent and the organization maintains strong governance over model changes, ensuring that efficiency gains do not come at the expense of audit defensibility.
How Does AI Integration Differentiate Stratlane’s Certification Services?
Stratlane differentiates by using a hybrid model where AI accelerates data processing and identifies risk areas while industry experts validate findings and provide remediation guidance, producing both speed and depth in certification assessments. Compared with traditional workflows that rely heavily on manual review, this approach increases consistency across audit engagements and reduces variability in what auditors examine. Clients benefit from shorter certification timelines and richer, more actionable audit reports that combine machine-speed evidence synthesis with expert interpretation. That differentiation supports faster client readiness for procurement requirements while preserving the trustworthiness of certification outcomes.
The hybrid model supports scalability without diluting quality, enabling Stratlane to deliver ISO certifications—including ISO 9001, ISO 14001, ISO 27001, and ISO 45001—using AI-assisted processes alongside expert oversight.
How Can Organizations Implement a Future-Ready Compliance Strategy with Technology?
A future-ready compliance strategy begins with assessing current maturity, piloting RegTech in high-risk areas, and scaling automation with governance and explainability baked in. Organizations should adopt a risk-based approach that prioritizes continuous monitoring and automated reporting, while ensuring data governance and model explainability for AI components. Roadmaps should include pilot programs, cross-functional governance committees, and measurable KPIs tied to audit cycle time, nonconformance rates, and evidence completeness. The numbered roadmap below provides an actionable implementation sequence for teams to follow.
A practical 6-step roadmap to enable continuous compliance:
- Assess Readiness: Conduct a compliance and technology maturity assessment to identify gaps and priorities.
- Define KPIs: Establish measurable targets such as audit cycle time and corrective action turnaround.
- Pilot Solutions: Run pilots in high-risk processes with limited scope to validate performance and explainability.
- Govern Models: Create governance for AI models, data lineage, and change management.
- Scale Automation: Expand successful pilots into broader monitoring and reporting workflows.
- Monitor & Improve: Continuously measure outcomes and refine models and controls.
This roadmap balances pragmatic pilots with robust governance so automation improves compliance without introducing new risks.
What Steps Enable Continuous Compliance and Risk Management Automation?
Continuous compliance is enabled by sequencing assessment, piloting, scaling, and monitoring with clear governance checkpoints at each phase. Start with a maturity assessment that maps current processes, data sources, and control owners; follow with narrowly scoped pilots that test real-time monitoring, automated reporting, and predictive analytics. Establish a governance board to own model approvals, data quality standards, and explainability requirements, and set KPIs that measure audit readiness, evidence availability, and remediation speed. Finally, operationalize continuous monitoring feeds into a centralized compliance platform that alerts owners, initiates workflows, and creates verifiable audit trails.
These steps create a repeatable cycle that turns episodic compliance work into an ongoing, risk-based program capable of adapting to regulatory and operational change.
Which Emerging Trends in AI and RegTech Will Shape Compliance in 2025 and Beyond?
Several trends will shape the compliance landscape: the rise of generative and large-model AI requiring explainability, growth in ESG and sustainability-focused RegTech, more cloud-first compliance architectures, and regulatory alignment efforts such as regional AI rules that affect model governance. Each trend affects readiness and tooling decisions: explainable AI requirements necessitate models that provide decision rationales, ESG RegTech requires new data pipelines and reporting templates, and cloud-first strategies prioritize vendor controls and cross-border governance. Organizations should evaluate these trends against their risk profile and adapt governance, tooling, and staffing accordingly.
Key readiness actions include investing in explainability tooling, mapping ESG reporting requirements, and building vendor risk management for cloud and AI suppliers.
For organizations seeking a partner to assess readiness and prepare for certification with AI-enabled audits, Stratlane Certification Deutschland offers certification services that combine AI-assisted auditing and expert review to reduce time and cost while maintaining rigorous quality assurance. If you want a readiness assessment or to discuss piloting AI-enabled audit workflows, consider a certification readiness engagement to map gaps and estimate potential efficiency gains.