ISO 27001 Implementierung: Eine umfassende Anleitung zur erfolgreichen Informationssicherheitszertifizierung
ISO 27001 Implementierung describes a structured approach to establishing, operating, monitoring and improving an Information Security Management System (ISMS) so organisations can protect information assets and demonstrate compliance. This guide explains what ISO 27001:2022 requires, why the 2025 migration window matters, and how a pragmatic, risk-based ISMS implementation delivers measurable reductions in cyber risk and stronger client assurance. Readers will learn a step-by-step roadmap for implementation, the documentation and evidence auditors expect, integration tactics with ISO 9001, sector-specific control priorities, and how AI-powered audit tools can shorten certification timelines. Practical templates, EAV comparison tables and actionable checklists are included to support project planning and internal alignment. The aim is to equip security, compliance and operational leaders with a repeatable implementation plan that supports certification while improving operational security outcomes.
Was ist ISO 27001 und warum ist die Implementierung 2025 entscheidend?
ISO 27001 is an international standard that specifies requirements for establishing, implementing, maintaining and continually improving an ISMS, using a risk-based approach to protect confidentiality, integrity and availability of information. The 2022 revision reorganised and consolidated Annex A controls, emphasised alignment with cybersecurity and privacy expectations, and promoted outcomes-focused controls that reflect modern IT and cloud usage. Implementing ISO 27001 in 2025 is critical because organisations face both a migration window and heightened client and regulator expectations that make timely certification a competitive and compliance requirement. Early adoption reduces transition risk, ensures alignment with current threat models, and positions organisations to meet procurement demands and regulatory overlays. Understanding these drivers sets up the implementation roadmap and documentation requirements described next.
Welche Vorteile bietet die ISO 27001:2022 Version für Unternehmen?
ISO 27001:2022 streamlines control sets and improves alignment with cybersecurity practices, reducing complexity while strengthening practical coverage of modern threats. The revision reduced the number of legacy control categories and reorganised Annex A to emphasise outcome-based controls, which helps organisations focus on measurable security outcomes rather than checkbox compliance. This enables clearer mapping between risk treatment plans and controls, which supports better resource allocation and clearer value demonstration to customers. Organisations implementing the 2022 version typically see improved audit clarity, faster evidence collection, and stronger alignment with data protection laws and cloud security expectations, which in turn enhances client trust and supplier competitiveness.
ISO 27001:2022 delivers several practical business benefits:
- Reduced control complexity that lowers maintenance overhead and streamlines audits.
- Improved alignment with cybersecurity and privacy standards, aiding regulatory compliance.
- Clearer measurables for security outcomes that support client assurance and tender eligibility.
These benefits explain why many organisations prioritise migration and implementation now; the next section maps how cybersecurity and data protection drivers shape ISMS requirements.
Wie beeinflussen Cybersecurity und Datenschutz die ISO 27001 Anforderungen?
Cybersecurity trends and data protection obligations directly shape ISO 27001 risk assessments and control selection, because modern threats alter the likelihood and impact of information risks. Practical examples include cloud workloads that require cloud-native controls and identity management, remote work that elevates endpoint and access controls, and regulatory overlays such as data protection laws that demand processing-specific safeguards. Mapping these operational realities to Annex A controls and risk treatment plans ensures that selected controls address both technical vulnerabilities and legal obligations. Incident response capabilities, logging and monitoring, and encryption often become high-priority controls as part of the ISMS, and these operational priorities feed back into monitoring KPIs and management review cycles.
This interplay between cybersecurity, privacy and ISO 27001 means that a good risk assessment informs both control selection and documentation practices, which leads naturally into the step-by-step implementation roadmap described below.
Wie gestaltet sich der Schritt-für-Schritt Prozess der ISO 27001 Implementierung?
ISO 27001 implementation follows a PDCA (Plan–Do–Check–Act) style lifecycle, beginning with scoping and risk assessment, then control implementation, monitoring and continual improvement toward certification readiness. The process typically includes planning the ISMS scope and policy, performing a risk assessment to populate a risk register, preparing a Statement of Applicability (SoA), implementing controls and procedures, conducting internal audits and management reviews, and arranging an external certification audit. Resource planning, timeline estimates and stakeholder engagement are essential throughout to keep the project on track and produce audit evidence. The following numbered roadmap provides an actionable sequence you can adapt for typical organisational size and complexity.
A concise implementation roadmap:
- Define Scope and Governance: Agree ISMS boundaries, stakeholders, and an information security policy.
- Asset Inventory and Classification: Identify information assets and assign value and ownership.
- Risk Assessment: Apply a defined methodology to identify threats, vulnerabilities and impacts.
- Risk Treatment Plan: Select controls, produce the SoA and prioritise treatment activities.
- Control Implementation: Deploy technical, organisational and procedural controls mapped to Annex A.
- Training & Awareness: Run role-based training and document competence evidence.
- Internal Audit & Management Review: Verify operation and drive corrective actions.
- Certification Audit: Engage an accredited body for stage-1 and stage-2 audits, then transition to surveillance.
This numbered sequence clarifies project milestones and supports stakeholder reporting; the next subsections unpack planning, risk analysis and control implementation specifics.
Welche Phasen umfasst die Planung und Risikoanalyse im ISMS?
Planning and risk analysis begin with clear scope definition, selection of an appropriate risk assessment methodology, and creation of an asset inventory that captures owners, value, and applicable processing activities. The methodology defines impact and likelihood criteria, assessment cadence, and decision thresholds for risk treatment; these choices must be documented and consistently applied. Outputs include a risk register that records identified risks, rated scores, proposed treatments and owners, plus a risk treatment plan that maps selected controls to residual risk. A short risk-register template typically contains fields for asset, threat, vulnerability, impact, likelihood, risk score, treatment, owner and review date, enabling traceable decision-making and audit evidence.
To operationalise the risk register into controls, teams next map findings to Annex A controls and draft the SoA that justifies applicability, which leads into the implementation and monitoring phase described next.
Wie erfolgt die Umsetzung und Überwachung der Sicherheitskontrollen?
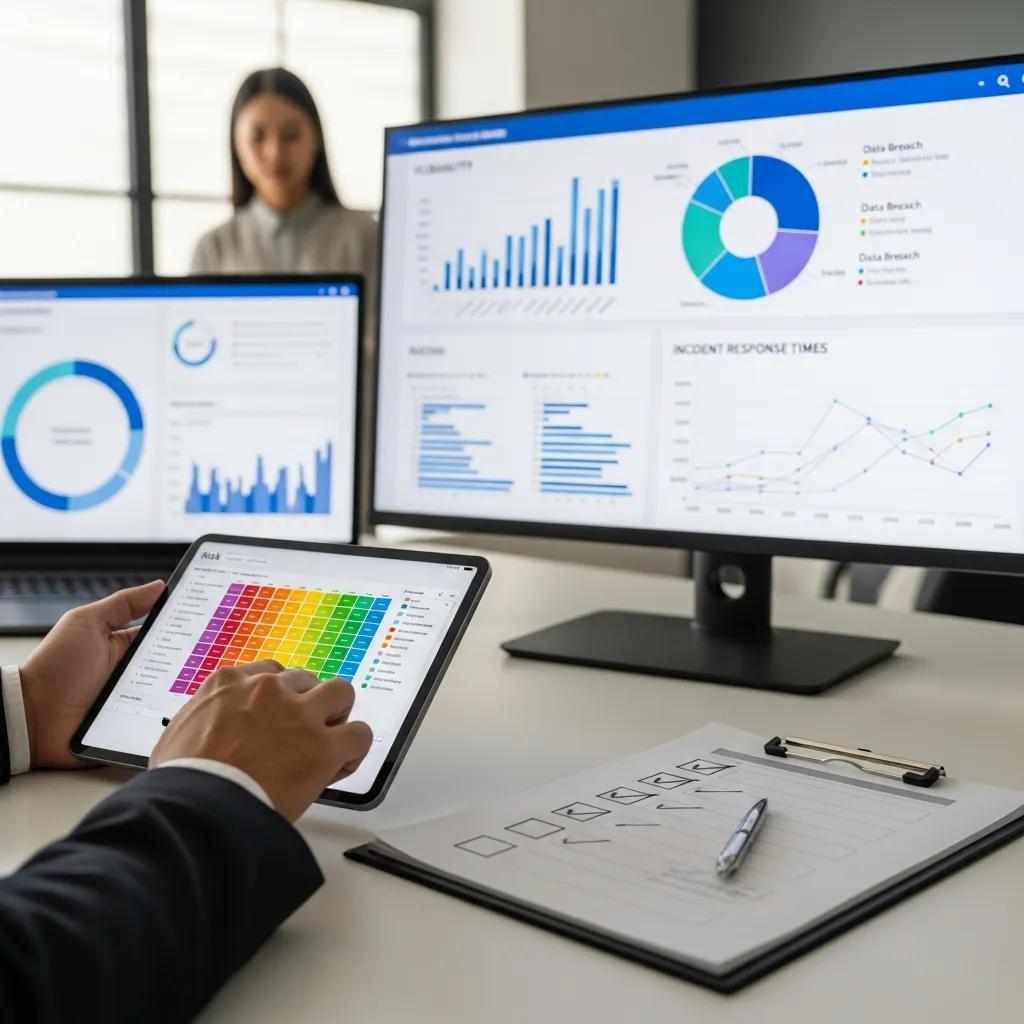
Control implementation requires translating SoA selections into concrete processes, technical configurations and documented procedures with assigned owners and KPIs to measure effectiveness. Typical steps include control design, change tickets for technical fixes, procedural writes for operational controls, and evidence capture templates for auditors (logs, configuration snapshots, training records). Monitoring is achieved through defined metrics such as incident frequency, mean time to detect/contain, audit nonconformities and control performance indicators; these feed internal audit schedules and management review agendas. Internal audits validate control operation, while management reviews evaluate ISMS performance and resource needs, closing the loop on continual improvement obligations.
Structured monitoring and evidence management prepare organisations for certification assessment; the next section details required documentation and evidence expectations.
| Implementation Phase | Key Activities | Deliverables |
|---|---|---|
| Planning | Define scope, policy, governance | ISMS scope statement, policy, project plan |
| Risk Assessment | Asset inventory, threat analysis | Risk register, methodology document |
| Implementation | Deploy controls, train staff | SoA, procedures, configuration evidence |
Welche Anforderungen und Dokumentationen sind für die ISO 27001 Zertifizierung notwendig?
Certification requires a core set of mandatory documents plus organisation-specific evidence demonstrating implemented controls and continual improvement. Mandatory items include the ISMS scope statement, information security policy, risk assessment and risk treatment plan, Statement of Applicability (SoA), procedures for key processes, internal audit reports, management review minutes and corrective action records. Auditors also expect objective evidence such as logs, configuration files, access control records, training attendance and contractual clauses for suppliers. Preparing those documents early reduces last-minute work and builds a sustainable audit trail for surveillance cycles.
Mandatory and recommended documentation list:
- ISMS Scope Statement: Defines boundaries and applicability of the ISMS.
- Information Security Policy: High-level direction and management commitment.
- Risk Assessment & Treatment Plan: Records of risk decisions and treatments.
- Statement of Applicability (SoA): Control selection, applicability and justification.
- Procedures & Evidence: Internal audit records, incident logs, access records.
Having these documents structured and traceable simplifies internal audits and demonstrates readiness for external certification; the SoA creation method below explains practical steps to complete applicability mapping.
Wie erstellt man eine vollständige Statement of Applicability?
A complete SoA lists Annex A controls, indicates whether each control is applicable, provides justification for inclusion or exclusion, and references the evidence or risk treatment measure that satisfies the control objective. The creation process begins by mapping each significant risk from the risk register to candidate controls, documenting why controls are selected or omitted, and linking each applicable control to owner, implementation status and evidence locations. A clear checklist for SoA preparation includes control identifier, applicability (yes/no), justification, implementation notes and evidence references. This linkage between risk, control justification and evidence streamlines auditor queries and demonstrates systematic risk-driven decision-making.
Producing a robust SoA reduces audit friction and helps teams prioritise remaining implementation tasks before the certification audit, which connects to the available templates discussed next.
Welche Checklisten und Vorlagen unterstützen die Dokumentation?
Practical templates accelerate documentation while ensuring consistency across owners and audits. High-value templates include a risk register template, SoA template with justification fields, internal audit checklist aligned to Annex A, incident response runbook template, access control procedure and management review agenda template. Each template should identify a typical document owner, expected review cadence and where evidence is stored. Using consistent templates reduces variances between departments, simplifies internal audits, and produces repeatable evidence for external auditors.
Key templates and recommended owners:
| Document Type | Typical Owner | Review Cadence |
|---|---|---|
| ISMS Policy | Executive sponsor or CISO | Annual |
| Risk Register | Risk manager | Quarterly |
| Statement of Applicability | ISMS owner | After major changes or annually |
| Internal Audit Plan | Internal audit lead | Annual |
Wie integriert man ISO 27001 effektiv mit ISO 9001 für ganzheitliche Managementsysteme?
Integrating ISO 27001 and ISO 9001 combines the process approach and PDCA cycles of a Quality Management System (QMS) with the risk-based information security focus of an ISMS, creating synergies that reduce duplication and streamline audits. Both standards share common elements such as leadership commitment, documented processes, internal audits and management review, so an integrated management system can reuse processes like document control, change management and supplier assessment while applying discipline-specific controls where needed. Planning integration requires mapping overlapping clauses, harmonising terminology, aligning review cycles and consolidating audit schedules to capture efficiencies. Practical integration reduces administrative burden and demonstrates a mature systemic approach to both quality and security.
The following EAV comparison highlights shared and distinct elements to guide integration planning.
| Process Area | ISO 9001 Evidence | ISO 27001 Evidence |
|---|---|---|
| Management Responsibility | Policy, objectives, reviews | ISMS policy, objectives, management review |
| Document Control | Controlled documents registry | Access control for sensitive documents |
| Supplier Management | Supplier evaluations, contracts | Supplier security requirements, due diligence |
| Internal Audit | Audit schedule, reports | Risk-focused audit findings, corrective actions |
Warum ist ISO 9001 Zertifizierung für viele Kunden eine Voraussetzung?
Procurement teams and many key clients often require ISO 9001 certification as evidence of consistent quality management, contractual fulfilment and organisational maturity, which reduces supplier selection risk and supports predictable service delivery. ISO 9001 is frequently a requirement for key clients. Quality certification signals process discipline that clients rely upon when assessing vendors, and many supplier frameworks explicitly list ISO 9001 as a precondition for tender participation. By combining ISO 9001 with ISO 27001, organisations can meet common procurement requirements while also addressing information security expectations, creating a stronger commercial position and simplified compliance narrative for customers.
Explaining how ISO 9001 supports client assurance naturally leads to planning a unified management system that preserves both quality and security outcomes, which the next subsection outlines.
Wie profitieren Unternehmen von einem integrierten Managementsystem?
An integrated management system reduces duplicated documentation, consolidates internal audit activities and aligns management review outputs across quality and security domains, producing time and cost savings. Shared processes such as document control, supplier evaluation and continual improvement can be managed once with controls mapped to both standards, leading to fewer audits and clearer responsibilities. Case examples typically show reduced audit days, streamlined corrective action processes and faster board-level reporting when systems are integrated. Planning should include a gap analysis between standards, a harmonised process map, and a consolidated audit plan to capture these efficiencies and ensure both certification bodies’ requirements are met.
These integration efficiencies make combined certification compelling for organisations that must satisfy both quality-driven clients and stringent information security expectations, and they help prepare for efficient AI-assisted audits described next.
Wie nutzt Stratlane KI-gestützte Audits zur Optimierung der ISO 27001 Implementierung?
Stratlane Certification Deutschland brings an AI-assisted approach to certification audits that combines automated evidence triage with experienced auditors to accelerate assessments and focus human attention on high-risk areas. As an innovative, accredited certification body with reach across Europe and the UK, Stratlane specialises in auditing and certifying management systems including ISO 27001:2022 and integrates AI-powered audit tools with expert judgement to improve audit efficiency and evidence quality. AI tools can pre-screen documentation, flag inconsistencies and prioritise high-risk items, while auditors validate context and perform assurance activities that require professional judgement. This blended model shortens assessment timelines, reduces routine auditor time and improves consistency of audit findings, which supports a faster path to certification.
A short bridge sentence: Organisations preparing for certification can leverage AI-driven pre-assessments and tailored support to speed readiness and reduce cost, then engage an accredited auditor for formal assessment and certification.
Welche Vorteile bieten AI-gestützte Prüfungen für Effizienz und Kosten?
AI-augmented audits improve efficiency by automating repetitive evidence checks, highlighting anomalies and prioritising auditor focus on areas of highest risk and uncertainty. Typical efficiency gains include faster evidence collection and validation, reduced auditor time spent on routine checks, and earlier detection of documentation gaps that would otherwise appear during stage-2 assessment. By triaging documentation and performing initial consistency checks, AI tools allow auditors to concentrate on interviews, control effectiveness and judgement-based sampling. The result is a reduction in overall audit days, clearer pre-audit feedback for implementers, and improved audit quality through systematic anomaly detection.
Further research highlights the transformative potential of AI and machine learning in enhancing cybersecurity audits and compliance processes.
AI & ML for Enhanced Cybersecurity Audits & Compliance
This study explores how artificial intelligence (AI) and machine learning (ML) transform cybersecurity auditing by enhancing compliance automation, threat detection, auditor trust, continuous monitoring, and sector-specific assurance in finance and healthcare.
ADVANCING THREAT DETECTION THROUGH ARTIFICIAL INTELLIGENCE AND MACHINE LEARNING ENHANCED CYBERSECURITY AUDITS, D Goswami, 2025
These operational improvements make AI-assisted audits valuable for organisations seeking to reduce certification cycle time while maintaining robust assurance, and they lead naturally into how Stratlane supports clients during preparation.
Wie unterstützt Stratlane Unternehmen bei der Vorbereitung auf die Zertifizierung?
Stratlane supports organisations with gap assessments, pre-audits, customised training, documentation templates and full certification audits, guiding clients from initial scoping to surveillance cycles after certification. A typical engagement begins with a gap analysis to identify missing controls and documentation, followed by targeted remediation support such as SoA workshops, internal audit execution and training for key roles. Pre-assessments using AI tools can rapidly highlight evidence gaps so teams can address them before the formal audit, reducing the risk of major nonconformities. Stratlane then conducts the formal certification audit and provides continuing surveillance support to ensure sustained compliance and improvement.
- Pre-assessment & Gap Analysis: Identify priorities and remediation roadmap.
- Documentation Support: Templates and SoA workshops to close evidence gaps.
- Certification Audit & Surveillance: Formal assessment and ongoing assurance.
This service model helps teams move from readiness to certification more predictably while maintaining focus on business risk reduction.
Welche branchenspezifischen Besonderheiten sind bei der ISO 27001 Implementierung zu beachten?
Sector-specific risk profiles and regulatory overlays influence control prioritisation and evidence requirements, so implementations should be tailored to the organisation’s industry context rather than relying solely on generic control baselines. For example, IT firms often prioritise cloud security and access management, financial organisations emphasise transaction integrity and segregation of duties, and healthcare providers must focus on patient data confidentiality and regulatory reporting. Understanding these sectoral emphases early in the risk assessment ensures that control selection and monitoring KPIs reflect real operational threats and compliance obligations. Tailored risk treatment plans and evidence sets reduce audit friction and ensure that certification demonstrates genuine operational security rather than superficial compliance.
The next subsection summarises key control emphases per sector to guide prioritisation during implementation.
Wie unterscheiden sich Anforderungen in IT, Finanz- und Gesundheitssektor?
Different sectors emphasise distinct controls driven by their core information risks: IT organisations focus on cloud governance, identity and access management and incident response capabilities, finance sector actors prioritise encryption, secure transaction logging and segregation of duties, while healthcare entities concentrate on patient data confidentiality, consent management and secure integration of medical devices. Each sector also faces specific regulatory overlays that must be considered in the SoA and evidence collection strategy, such as data protection obligations and industry-specific reporting standards. Mapping these sector priorities into the risk register and control design ensures the ISMS addresses the most consequential exposures for the organisation.
Recognising these differences helps teams design targeted controls and collect sector-relevant evidence ahead of audits, which leads to the recommended resources and support options below.
Wo finde ich weiterführende Informationen zu branchenspezifischen Lösungen?
For deeper guidance, organisations should consult official standards, national guidance and sector-specific best practice while also seeking tailored advice from experienced certification bodies and consultants who understand both the standard and the industry context. Authoritative resources include standards bodies’ guidance documents and national cybersecurity agencies’ sectoral advisories, which provide implementation examples and control expectations. Many certification bodies and specialised consultancies also publish industry-focused whitepapers and templates that translate Annex A controls into sector-applicable measures. Engaging with experienced auditors or assessment partners early secures clarity on evidence expectations and reduces surprises during the certification audit.
Below is a brief list of recommended resource types and a prompt to seek tailored industry support:
- Official standard guidance and sector advisories from recognised authorities.
- Industry-specific whitepapers and implementation checklists from experienced providers.
- Professional consultancy or certification body support for tailored ISMS design.
This targeted approach helps organisations align their ISMS with sector demands and prepare robustly for certification.
| Document | Purpose | Typical Owner |
|---|---|---|
| Risk Register | Record and prioritise risks | Risk Manager / ISMS Owner |
| Statement of Applicability | Map controls to risks and justify exclusions | ISMS Owner |
| Internal Audit Reports | Evidence of monitoring and improvement | Internal Audit Lead |
These tables and lists combined provide a practical blueprint to structure implementation activities, assign responsibility and gather audit evidence in a way that supports timely certification and ongoing security improvement.