Kontinuierliche Verbesserung: Der PDCA-Zyklus für ISO 9001 und ISO 27001 Zertifizierung
Continuous improvement is the purposeful process of iterating systems, controls and behaviours so organizations deliver more reliable quality and stronger information security over time. The PDCA Zyklus — also called the PDCA cycle or Plan–Do–Check–Act (Deming Cycle) — is a lightweight, repeatable framework that translates strategy into measurable improvement at process level, producing faster corrective action and clearer evidence for audits. Readers will learn the four PDCA phases, how each phase maps to ISO 9001 and ISO 27001 requirements, practical KPIs to track improvement, and how AI-assisted auditing accelerates the Check and Act phases. Many teams struggle to make continuous improvement operational because they treat audits as endpoints rather than feedback loops; PDCA reframes audits as inputs for iterative change and performance validation. This guide walks through PDCA mechanics, provides clause- and control-level crosswalks for QMS and ISMS implementers, presents EAV-style tables for immediate use during implementation or audit preparation, and highlights how certification bodies with AI-powered audit tooling and experienced auditors can speed qualification outcomes.
Was ist der PDCA-Zyklus und wie unterstützt er kontinuierliche Verbesserung?
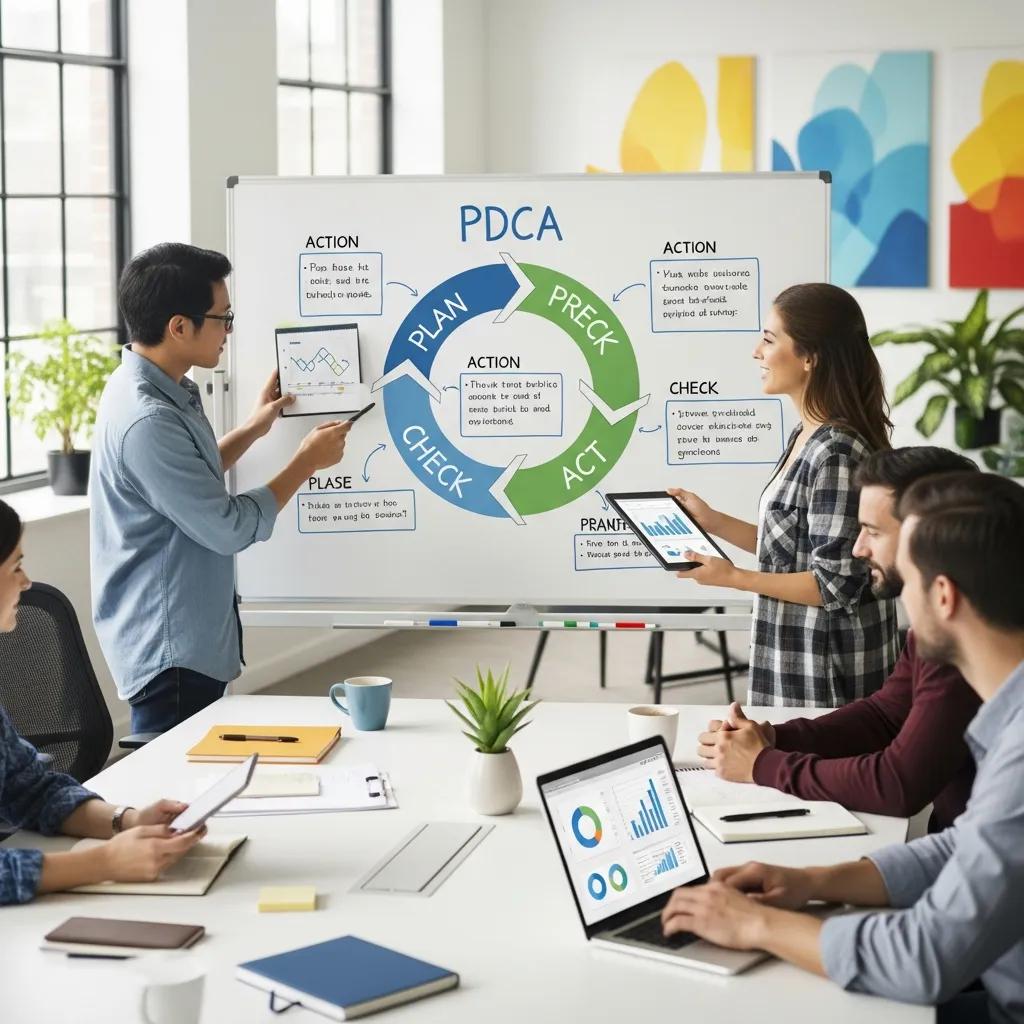
The PDCA Zyklus is a four-step iterative method for managing and improving processes by planning changes, implementing them, checking results and acting on findings to institutionalize improvements. At its core PDCA translates strategic objectives into concrete experiments and measurable outcomes, so organizations reduce variation and raise process capability over successive cycles. The cycle supports continuous improvement because each iteration produces data—metrics, nonconformities, audit findings—that feed the next planning phase, creating a closed feedback loop that sharpens both controls and decision-making. Understanding PDCA as an operational rhythm helps teams embed risk-based thinking into routine process governance and prepares evidence for ISO auditors.
The following numbered list outlines the four phases with one-line roles for ISO contexts and prepares the reader for deeper, clause-level mapping in later sections.
- Plan: Define objectives, risks, KPIs and the change hypothesis; prepare documented plans and resources for ISO-aligned controls.
- Do: Execute the planned activities, implement controls and collect implementation evidence such as logs, SOP updates and training records.
- Check: Measure performance, run internal audits and analyze metrics to test the hypothesis and control effectiveness against ISO requirements.
- Act: Close the loop with corrective actions, management review and updates to policies and objectives to institutionalize improvements.
H3: Welche vier Phasen umfasst der PDCA-Zyklus?
Each PDCA phase has a clear objective and predictable tasks that produce audit evidence and support continual improvement. In Plan teams establish context, set measurable objectives and identify risks and opportunities—typical outputs are process maps, KPI definitions and risk registers. In Do the organization carries out the plan via documented procedures, training and control implementations while capturing records that demonstrate operation. In Check the focus is measurement: monitoring KPIs, internal audits, control testing and data analysis to determine whether the Do step achieved the Plan’s goals. In Act leaders authorize corrective actions, revise objectives and update documented information based on Check findings, ensuring the next Plan is informed by real performance data.
H3: Wie trägt der Deming Cycle zur Qualitäts- und Informationssicherheit bei?
The Deming Cycle’s emphasis on iterative learning and statistical thinking underpins modern quality management and informs risk-based ISMS practices by making data central to decisions. Deming popularized the idea that management should view processes as systems of causes and outputs, which aligns with ISO 9001’s requirements for context, performance evaluation and continual improvement. For information security, Deming’s learning mindset supports continuous validation of controls and the use of metrics to reduce incident frequency and severity. Practitioner reports and industry guidance indicate that applying PDCA to both QMS and ISMS shifts organizations from reactive fixes to proactive resilience, with management review and measurable KPIs closing the loop between technical controls and business risk.
Understanding this conceptual lineage helps implementers apply PDCA as a shared improvement language across quality and security teams, which is discussed next for ISO 9001 contexts.
Wie wird der PDCA-Zyklus in ISO 9001 Qualitätsmanagementsystemen angewendet?
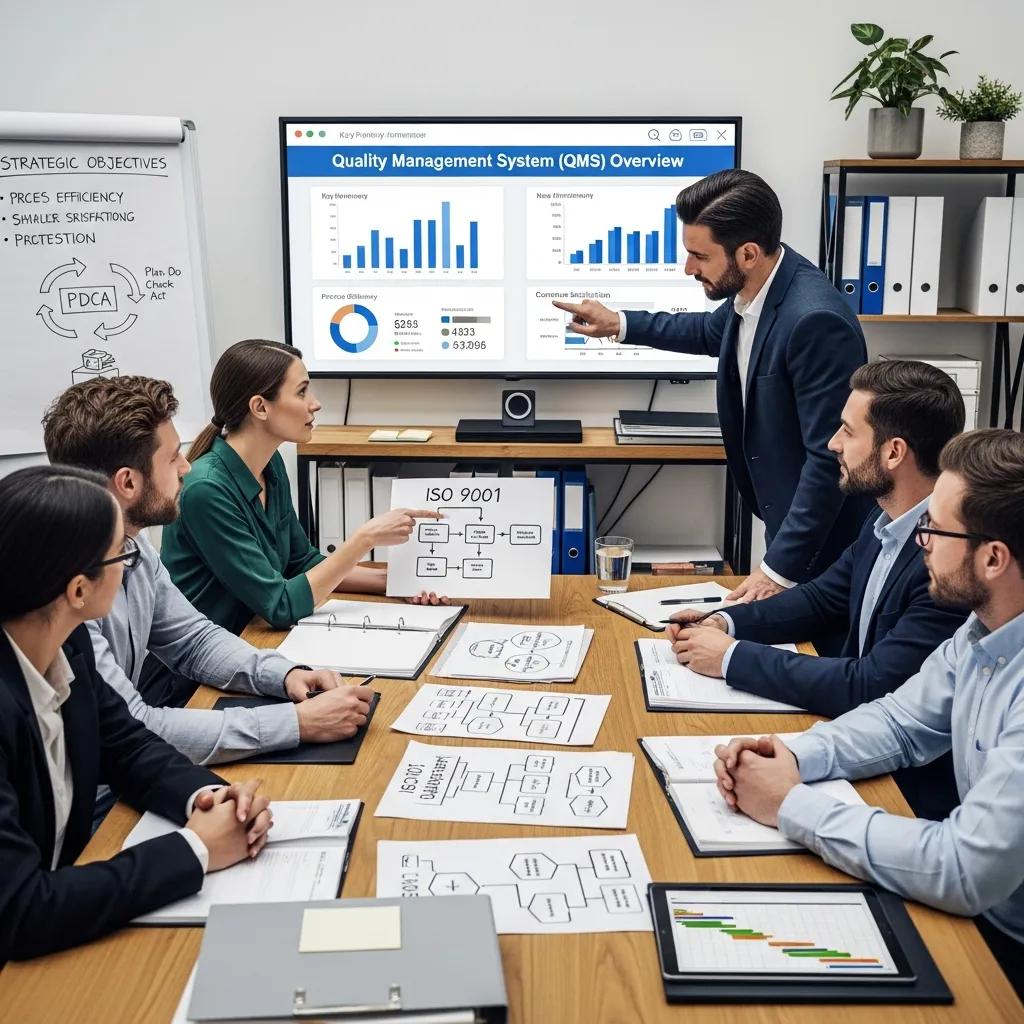
PDCA in ISO 9001 maps planning to context and objectives, doing to process operations, checking to monitoring and internal audit, and acting to management review and corrective actions. When applied correctly, the PDCA cycle gives QMS owners a repeatable method for translating clause requirements into concrete artifacts and performance evidence auditors expect. Practically this means the Plan phase documents context (clause 4), sets quality objectives and risk-based plans (clause 6), Do executes operational controls and records outputs (clauses 7 & 8), Check uses monitoring, measurement and internal audits (clause 9), and Act formalizes improvements through management review and corrective action (clause 10). This clause-aligned approach reduces compliance ambiguity and makes continual improvement demonstrable.
Implementers can use the following EAV-style table to map PDCA phases to ISO 9001 activities and deliverables for auditor-ready evidence.
| PDCA Phase | ISO 9001 clause relevance / typical activities | Typical deliverables or documents |
|---|---|---|
| Plan | Clause 4 (Context), Clause 6 (Planning, objectives) | Context analysis, quality objectives, risk register |
| Do | Clause 7 & 8 (Support, Operation) | Procedures, work instructions, training records, process logs |
| Check | Clause 9 (Performance evaluation) | KPI reports, internal audit reports, monitoring records |
| Act | Clause 10 (Improvement) | Corrective action reports, management review minutes, updated documentation |
This crosswalk shows how each PDCA phase produces specific evidence auditors expect, smoothing certification journeys and enabling measurable improvement.
After mapping phases to clauses, practitioners should apply PDCA at process level to handle common QMS challenges such as nonconformity reduction and supplier performance management.
H3: Welche Rolle spielt PDCA bei der Verbesserung von QMS-Prozessen?
At process level PDCA converts problems into experiments that yield measurable outcomes and reproducible improvements. For example, a customer complaint process can be planned with target response times and root-cause analysis steps, executed with standardized triage (Do), monitored via complaint metrics and audit checks (Check), and improved with corrective actions and revised SLAs (Act). Typical KPIs include complaint cycle time, repeat complaint rate and first-time resolution—data that demonstrates improvement across cycles. Embedding PDCA into process governance helps teams move from ad-hoc fixes to systematic capability-building, enabling sustained reductions in defects and improved customer satisfaction.
This operational approach leads directly into a clause-to-phase mapping that implementers and auditors can use as a checklist.
H3: Wie korrespondieren PDCA-Phasen mit den Anforderungen der ISO 9001:2015?
Direct clause-to-phase mappings clarify expected evidence and simplify audit preparations by tying PDCA outputs to specific ISO requirements. For Plan, link clause 4 context and clause 6 planning documents; for Do, show process records and competence evidence under clauses 7 and 8; for Check, present performance evaluation outputs per clause 9; and for Act, provide corrective actions and continual improvement evidence under clause 10. Sample evidence artifacts include risk assessments, documented objectives, process maps, training logs, audit reports and management review minutes, which together form a traceable improvement narrative. Using this mapping as a checklist helps organizations prepare succinct evidence packages for certification audits and internal reviews.
Having established the QMS crosswalk, we now examine how PDCA applies to information security systems with an ISMS-focused mapping.
Wie fördert der PDCA-Zyklus kontinuierliche Verbesserung in ISO 27001 Informationssicherheitsmanagementsystemen?
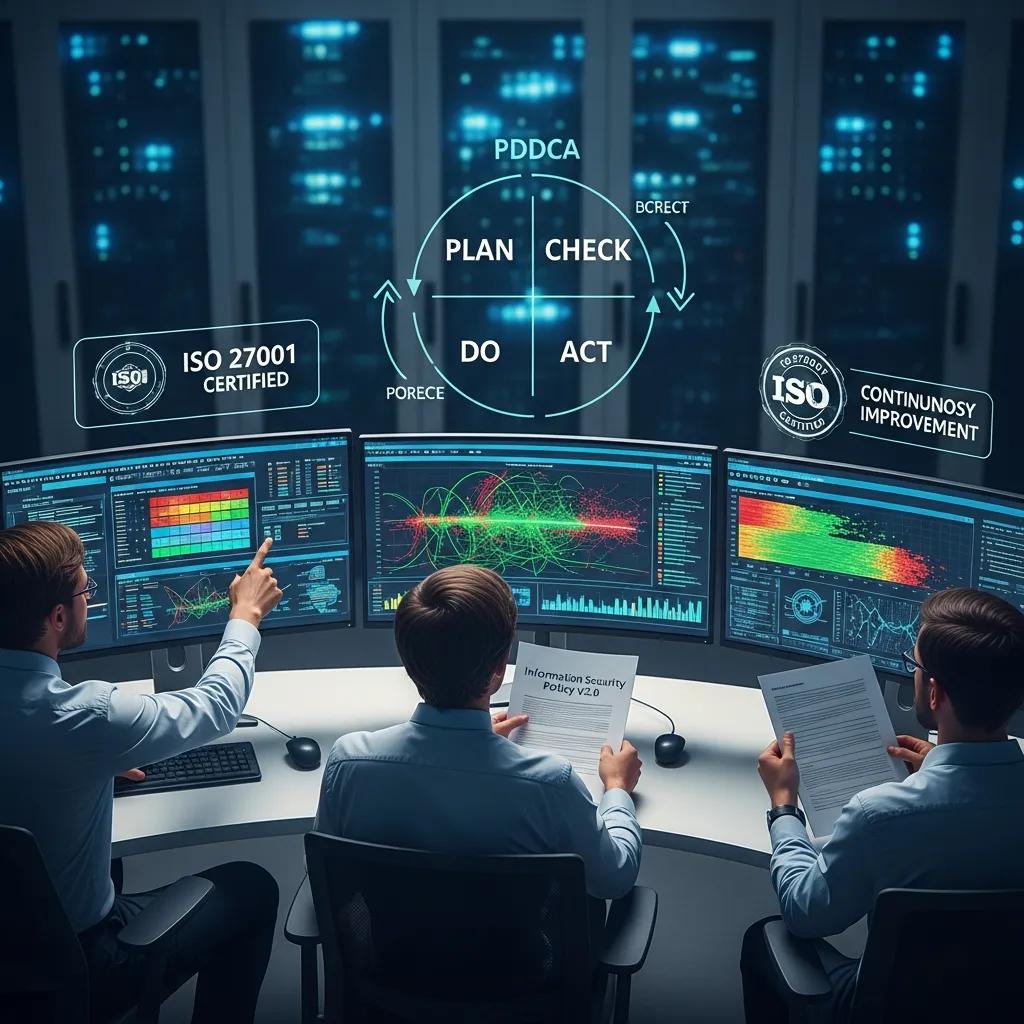
PDCA for ISO 27001 frames the risk lifecycle: Plan covers risk assessment and ISMS scope, Do implements policies and controls, Check measures control performance and conducts audits, and Act updates risk treatment and controls based on findings. Applying PDCA to ISMS workstreams ensures controls are tested and improved iteratively, which increases control effectiveness and reduces incident recurrence. ISMS teams should treat internal audits and security testing as inputs to Act, using evidence to refine control selection and treatment plans. The PDCA rhythm makes information security accountable to measurable objectives and ties technical controls back to business risk.
Key PDCA links to ISMS activities:
- Plan: Establish ISMS scope, conduct risk assessment, and document risk treatment plans.
- Do: Deploy security policies, technical controls and awareness training, creating operational evidence.
- Check: Monitor logs, run control effectiveness tests and conduct internal audits to evaluate performance.
- Act: Apply corrective actions, update risk treatments and perform management review to institutionalize improvements.
This overview prepares implementers for a concise PDCA→ISMS crosswalk and examples of metrics used to measure control effectiveness.
H3: Wie unterstützt PDCA das Risikomanagement und die Kontrolle von ISMS?
PDCA structures a predictable risk lifecycle where identification feeds treatment, treatment is implemented and monitored, and monitoring outcomes drive re-evaluation of residual risk. For example, Plan creates a risk register and acceptable risk criteria; Do deploys encryption, access controls and logging; Check compares incident trends and control test results against thresholds; Act remediates gaps and updates the registry. Useful ISMS metrics include mean time to detect (MTTD), mean time to remediate (MTTR), control pass rates from testing and percentage of overdue corrective actions. These measurable signals let security teams demonstrate continuous improvement in audits and to stakeholders.
This metric-driven approach leads into a compact clause mapping showing ISO 27001 clauses tied to PDCA activities and suggested evidence.
H3: Welche ISO 27001-Klauseln sind eng mit dem PDCA-Zyklus verbunden?
ISO 27001 clauses align naturally to PDCA: context and leadership inform Plan, support and operation correspond to Do, performance evaluation maps to Check, and improvement links to Act. Implementers should map clause numbers to expected artifacts—context/leadership (4–5): scope and leadership commitment; planning (6): risk assessment and objectives; support/operation (7–8): policies, procedures and control implementation; performance evaluation (9): monitoring, audits and reviews; improvement (10): corrective actions and updates. The following mini-table summarizes clause mappings and examples of audit evidence.
| PDCA Phase | ISMS activity | Example evidence for audit |
|---|---|---|
| Plan | Context, leadership, planning | Scope statement, risk assessment, objectives |
| Do | Support & Operation | Policies, control implementation logs, training records |
| Check | Performance evaluation | Monitoring reports, internal audit findings, KPI dashboards |
| Act | Improvement | Corrective action logs, updated risk treatment plans, management review minutes |
This clause-to-PDCA mapping helps ISMS owners prepare focused evidence packages that demonstrate continual improvement in line with ISO 27001 expectations.
Welche Vorteile bietet die Anwendung des PDCA-Zyklus für Führungskräfte und IT-Verantwortliche?
PDCA delivers measurable business outcomes that matter to leaders: reduced operational cost through fewer defects, stronger compliance posture with fewer audit findings, and increased customer and partner confidence through demonstrable process maturity. By converting vague improvement goals into iterative, testable cycles, PDCA reduces time-to-detection and shortens remediation timelines, translating into quantifiable risk reduction. For IT managers, the framework integrates technical control testing with management reporting, enabling data-driven decisions that improve uptime and reduce incident recurrence. For procurement and commercial teams, PDCA-driven certification signals reliable processes and lowers supplier risk.
The following list presents core executive-facing benefits and representative KPIs leaders can use to evaluate impact and ROI.
- Efficiency gains: Reduced cycle times and defect rates measured by percentage drop in process cycle time and rework rate.
- Compliance improvement: Fewer nonconformities and audit findings, tracked via audit closure rate and reduction in repeat findings.
- Customer and partner trust: Stronger tender eligibility and supplier assurance when processes are certified and continuously improved.
ISO 9001 certification is often required by key clients, and this procurement reality makes PDCA not only a quality tool but also a pathway to market access and commercial de-risking.
The next short EAV table helps decision-makers connect PDCA benefits to measurable KPIs and expected impact windows.
| Benefit | Metric / KPI | Expected impact / timeframe |
|---|---|---|
| Efficiency | Cycle time, defect rate | 10–30% improvement in 6–12 months |
| Compliance | Audit findings, closure rate | 50–80% reduction in repeat findings in 6 months |
| Trust & Access | Tender eligibility, supplier score | Faster qualification for bids; improved supplier ratings within one certification cycle |
These benefit-to-metric mappings help leaders prioritize PDCA initiatives that align with business goals and procurement requirements.
H3: Wie steigert PDCA Effizienz, Compliance und Kundenzufriedenheit?
PDCA improves efficiency by making small, measurable changes that accumulate into significant performance gains; organizations typically combine Plan experiments with Do pilots, Check results and scale via Act. Compliance improves when Check activities (internal audits, monitoring) reveal gaps early and Act ensures timely corrective action, reducing the incidence of major findings in external audits. Customer satisfaction rises because defect rates decline and response times improve, and because certified processes provide an auditable guarantee of consistent service delivery. Leaders should track representative KPIs—cycle time, defect frequency and Net Promoter-like feedback—to quantify improvements and to feed the next PDCA iteration.
H3: Warum ist ISO 9001 und ISO 27001 Zertifizierung für Geschäftspartner wichtig?
Certification signals that standardized processes and controls exist, are monitored and are continually improved, which reduces partner risk and streamlines supplier qualification. For many tenders and strategic partnerships, certification provides third-party assurance that risk-based controls operate effectively and that management oversight is active. PDCA is the mechanism that sustains certification — it produces the records, metrics and management reviews auditors examine to verify ongoing conformity. Organizations that treat certification as continuous improvement rather than a one-off audit earn long-term trust and easier access to new business opportunities.
This commercial context leads naturally to how certification bodies and AI-assisted audits can accelerate PDCA outcomes for clients.
Wie unterstützt Stratlane Certification Deutschland mit KI-gestütztem Audit den PDCA-Zyklus?
Stratlane Certification Deutschland is a certification services provider based in Düsseldorf with operations across Europe and the UK that audits and certifies management systems against international ISO standards including ISO 9001, ISO 14001, ISO 27001 and ISO 45001. Their approach combines AI-powered audit tools with experienced industry auditors to enhance audit efficiency and evidence synthesis while maintaining expert judgment. AI-assisted tooling accelerates evidence collection and anomaly detection during the Check phase, while experienced auditors interpret findings and prioritize Act recommendations that align with business risk. This blended model aims to deliver high-quality, efficient and cost-effective certification processes for organizations pursuing continual improvement and market-ready assurance.
The following list explains how AI plus auditor expertise improves specific PDCA outcomes and prepares organizations for faster, more reliable certification.
- Faster evidence aggregation: AI analyzes records, logs and documentation to present probable findings for auditor review.
- Improved anomaly detection: Automated trend analysis flags control regressions earlier in Check cycles.
- Actionable recommendations: Experienced auditors convert AI findings into prioritized corrective actions for management review.
This combined capability supports organizations that must demonstrate continual PDCA-driven improvement as part of their procurement and compliance strategies.
H3: Wie verbessert KI die Check- und Act-Phasen des PDCA-Zyklus?
AI tools enhance the Check phase by automating routine data analysis, correlating events across logs and surfacing trends that human reviewers might miss, which reduces time-to-insight and increases the accuracy of control effectiveness assessments. For Act, AI-generated trend reports and anomaly summaries shorten the management review preparation time and provide evidence-based inputs for prioritizing corrective actions. In practice, AI can produce dashboards that highlight recurring nonconformities, quantify residual risk and estimate remediation timelines, while auditors validate and contextualize those outputs for final recommendations. Together, these capabilities compress PDCA cycles and increase the velocity of continuous improvement.
These AI benefits combine with auditor expertise and global recognition to create stronger market access and trust.
H3: Welche Vorteile bieten erfahrene Auditoren und globale Anerkennung?
Experienced, accredited auditors provide interpretative judgment that complements AI outputs by assessing systemic issues, measuring risk appetite alignment and advising on practical remediation priorities. Global acceptance of certificates ensures that a company’s documented PDCA practices are recognized across borders, facilitating international trade and partner qualification. Auditor sector knowledge accelerates audit focus on high-risk areas while minimizing disruption to business operations, producing certificates that stakeholders trust. The synergy of AI tools and auditor experience therefore enhances both the credibility and the efficiency of certification outcomes.
With practical auditing support clarified, implementers will find value in real-world examples showing measurable PDCA results across sectors.
Welche Praxisbeispiele zeigen erfolgreiche PDCA-Implementierung für ISO-Zertifizierungen?
PDCA produces consistent, measurable improvements in diverse industries when applied with discipline: IT operations reduce incident repeats, manufacturing lowers defect rates, and service providers shorten complaint resolution times. Case examples commonly share a pattern: Plan precise objectives and KPIs, run controlled Do pilots, Check outcomes with audits and monitoring, and Act to scale successful changes and close gaps. These cross-industry lessons demonstrate transferable practices such as using small-scope pilots for rapid learning, integrating internal audits into monthly Check routines and making management review outcomes actionable. The following anonymized industry examples illustrate these principles and provide practical takeaways for implementers.
H3: Wie haben verschiedene Branchen PDCA für Qualitäts- und Informationssicherheitsverbesserung genutzt?
In IT operations, PDCA reduced mean time to remediate by implementing targeted Playbooks (Plan), executing incident drills (Do), analyzing response metrics (Check) and updating runbooks (Act), which delivered measurable MTTR reduction. In manufacturing, a line that used PDCA to reduce defects planned root-cause experiments (Plan), trialed tooling adjustments (Do), measured defect trends (Check) and standardized the successful change (Act), achieving sustained defect-rate decline. In professional services, firms applied PDCA to improve delivery consistency by planning standardized templates, piloting them with select teams, auditing usage and embedding successful templates across the organization. Each industry example shows how PDCA turns localized changes into organizational improvements.
These examples lead to a final set of measurable outcomes that organizations can expect when PDCA is applied consistently.
H3: Welche messbaren Ergebnisse erzielten Unternehmen durch kontinuierliche Verbesserung?
Organizations regularly report measurable outcomes such as percentage reductions in defect rates, faster audit closure times and lower incident recurrence when PDCA is applied and sustained. Representative KPI improvements include defect reductions of 10–40%, audit finding reductions of 50–80% for repeat issues, and time-to-certification improvements when evidence packages are organized around PDCA artifacts. Tracking these metrics requires disciplined monitoring and a simple dashboard that ties PDCA cycles to business outcomes and audit evidence. By reporting progress in management review and feeding results into the next Plan phase, organizations convert isolated wins into enterprise-level reliability gains.
ISO 9001 certification is often required by key clients, and organizations that pair rigorous PDCA practice with credible certification support are better positioned to meet procurement criteria. For teams ready to translate PDCA into certified outcomes, contacting an accredited certification services provider can clarify qualification requirements and audit readiness. Stratlane Certification Deutschland offers certification services and AI-powered audit support that help organizations align PDCA-driven improvement with the evidence auditors expect—contact Stratlane Certification Deutschland to discuss qualification and audit services and how a PDCA-centered approach can accelerate your path to certification.