Das ISO 27001 Audit: So bereiten Sie sich vor – Ihr umfassender Leitfaden zur erfolgreichen Zertifizierung
The ISO 27001 audit verifies that an organisation’s Information Security Management System (ISMS) effectively protects confidentiality, integrity and availability of information assets while meeting international standard requirements. This guide shows IT directors, security leads and business managers how the ISO 27001 audit process works, what to prepare, and which controls and documents auditors expect to see to reduce procurement friction and strengthen client trust. You will learn the standard’s core objectives, the practical steps to define scope and run risk assessment, how Stage 1 and Stage 2 audits differ, and how to handle nonconformities and surveillance audits. Along the way the article explains how ISO 9001 often factors into customer procurement, why integrating quality and information security systems pays off, and how AI-assisted audit tools streamline evidence mapping. For organisations considering certification, Stratlane Certification Deutschland offers ISO 27001:2017 certification audit services and can certify ISO 9001 where clients require both quality and information security alignment; this mention is brief so you can focus on practical readiness first.
The ISO 27000 series of standards provides the foundational framework against which an Information Security Management System (ISMS) can be officially certified.
ISO 27000 Series: Standard for ISMS Certification
The ISO 27000 series of standards provide a standard against which an information security management system (ISMS) can be certificated.
Improving the quality of information security management systems with ISO27000, 2011
Was ist ISO 27001 und warum ist die Zertifizierung wichtig?
ISO 27001 is an international management standard that specifies requirements for establishing, implementing, maintaining and continually improving an ISMS to protect information assets. The standard works by requiring a documented risk management framework, selection and implementation of Annex A controls, and leadership-driven governance to ensure risks are identified and treated. The primary business value of ISO 27001 certification is demonstrable assurance to customers and stakeholders that information risk is systematically managed, which reduces contractual friction and supports regulatory alignment. Understanding the ISMS components and strategic benefits prepares organisations for practical steps like scoping, risk assessment and internal audits, which we cover next.
ISO/IEC 27001 specifically outlines the comprehensive requirements and implementation process for an ISMS, emphasizing a business risk approach for continuous improvement.
ISO 27001 ISMS: Requirements & Implementation for Certification
ISO/IEC 27001 specifies the requirements and implementation process for the Information Security Management System (ISMS), which is a part of the general management system, based on a business risk approach, to establish, implement, operate, monitor, review, maintain and improve information security.
Statement of applicability as a key element of the GIS certification process in the light of cybersecurity standards, M Kiedrowicz, 2022
This section clarifies what an ISMS contains and why the certification yields measurable competitive advantages.
Wie definiert sich das Information Security Management System?
An ISMS is the organised set of policies, procedures, controls and roles that together protect information across people, processes and technology. It typically includes documented security policies, an asset inventory, risk assessment and treatment plans, a Statement of Applicability (SoA), incident management procedures and records of internal audits and management reviews. Governance is critical: top management must own the ISMS and assign a security owner to maintain accountability and continuous improvement. Clear role definitions and documented processes ensure that evidence exists for auditors, enabling efficient verification during a certification audit.
This definition leads directly into the strategic benefits organisations realise by certifying.
Welche strategischen Vorteile bietet die ISO 27001 Zertifizierung?
ISO 27001 certification delivers several strategic benefits that improve market position and operational resilience:
- Market Access and Trust: Certification signals dependable information governance to customers and partners.
- Regulatory Alignment: The ISMS supports compliance with data protection and sector-specific rules.
- Risk Reduction and Resilience: Systematic risk management lowers breach likelihood and limits impact.
These advantages translate into faster procurement decisions, reduced contractual negotiation on security clauses, and a quantified basis for investment in controls, which then connect into how ISO 9001 often appears in procurement requirements.
Warum ist ISO 9001 für viele Schlüsselkunden eine Voraussetzung?
ISO 9001 is a quality management standard that many key customers use as a baseline for supplier selection because it demonstrates consistent process control and supplier management capability. Procurement teams often treat ISO 9001 as a proxy for organisational maturity and predictable delivery, which reduces perceived supplier risk and simplifies vendor onboarding. For companies pursuing ISO 27001, holding ISO 9001 alongside an ISMS can streamline vendor evaluations and satisfy customers who require both quality and information security assurances. Stratlane Certification Deutschland can certify both ISO 27001 and ISO 9001, and their accredited operations across multiple countries, combined with AI-powered audit tools, help demonstrate alignment to procurement criteria efficiently.
Explaining the complementarity of ISO 9001 and ISO 27001 shows why integrated management systems often produce the best commercial outcomes.
Wie ergänzt ISO 9001 die ISO 27001 für umfassende Unternehmenssicherheit?
ISO 9001 complements ISO 27001 by formalising process controls, change management and supplier oversight that underpin effective information security controls. Where ISO 27001 focuses on information risk and Annex A controls, ISO 9001 ensures that processes are repeatable, responsibilities are defined and supplier performance is monitored — all of which reduce operational causes of security incidents. Integrating a QMS and ISMS reduces duplicated audits, aligns management review cycles and consolidates documentation such as procedures and records. Practical integration examples include linking supplier evaluation criteria in ISO 9001 with supplier access controls required by the ISMS.
This comparison clarifies why many customers list ISO 9001 as a procurement prerequisite and how it supports security objectives.
Welche Rolle spielt ISO 9001 beim Aufbau von Kundenvertrauen?
ISO 9001 builds customer trust by proving that an organisation manages quality risks, meets contractual requirements consistently, and has structured continuous improvement processes. In procurement scenarios, buyers use ISO 9001 certification as a quick filter to shortlist suppliers who demonstrate process discipline and reduced delivery risk. Certification can reduce the need for lengthy due diligence, lower insurance or oversight costs, and increase the likelihood of winning long-term contracts. Organisations that combine ISO 9001 and ISO 27001 show both procedural reliability and information protection, which together strengthen bids for sensitive or regulated work.
This role of ISO 9001 naturally leads into the concrete preparation steps for an ISO 27001 audit, which are the next focus.
Welche Schritte sind für die Vorbereitung auf das ISO 27001 Audit erforderlich?
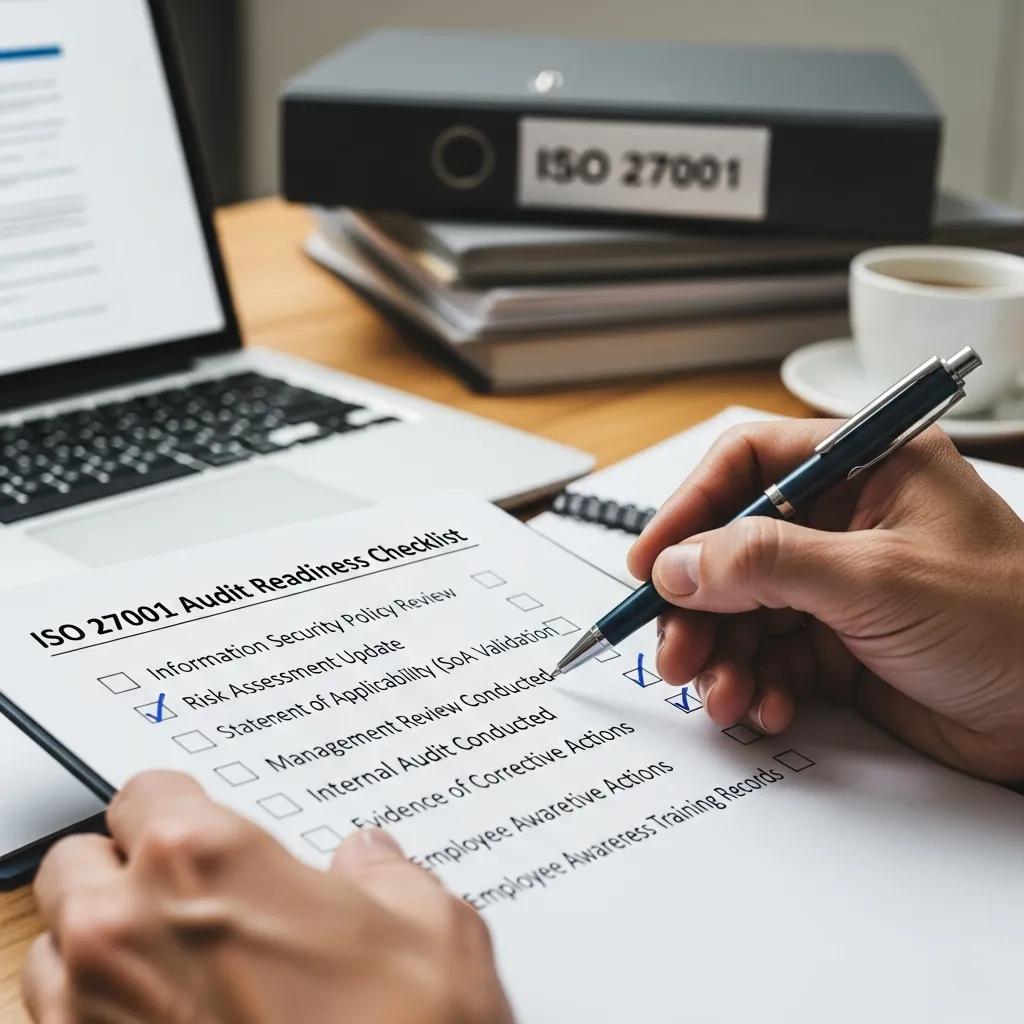
Preparing for an ISO 27001 audit follows a structured roadmap: define scope, conduct risk assessment and treatment, implement necessary controls, prepare documentation including a Statement of Applicability, run internal audits and perform a management review to demonstrate continual improvement. The information security audit process demands evidence for risk-based decisions and control effectiveness, so preparing records and assigning owners early reduces last-minute pressure. Organisations often use an evidence checklist, internal mock audits and gap analysis to validate readiness before inviting a certification body. Below is a concise numbered preparation checklist that targets featured-snippet style clarity.
Follow these steps as a practical checklist to become audit-ready.
- Define ISMS scope clearly, including locations, assets and interfaces.
- Conduct a risk assessment and create a risk treatment plan linked to Annex A controls.
- Compile mandatory documentation: policies, SoA, procedures, records of controls and internal audit reports.
- Perform internal audits and a management review to demonstrate monitoring and continual improvement.
- Address gaps with corrective actions and evidence before scheduling Stage 1.
A brief summary: following this sequence creates a defensible audit trail and ensures the ISMS is auditable and aligned to business context.
Intro to the checklist table: the table below helps compare required documents, their purpose and typical owners to support audit preparation.
| Document | Purpose | Typical Owner / Example Content |
|---|---|---|
| ISMS Scope Statement | Defines boundaries and applicability of controls | CISO or ISMS Lead — scope description, included sites, exclusions |
| Risk Assessment & Treatment Plan | Identifies, analyses and documents risk responses | Risk owner — risk register, likelihood/impact, treatment actions |
| Statement of Applicability (SoA) | Maps Annex A controls to implemented controls and justification | ISMS Lead — control selection, implementation status, justification |
| Policies & Procedures | Provide rules and process steps for control operation | Process owners — access control policy, incident response procedures |
| Internal Audit Reports | Evidence of monitoring, nonconformities and corrective actions | Internal audit team — findings, corrective action records |
This documents comparison highlights who owns evidence and why each item matters; keeping owners and contents explicit accelerates auditor verification. The next step explains effective scoping in detail.
Wie definiert man den Geltungsbereich des ISMS effektiv?
Defining the ISMS scope requires identifying the information assets, business processes, locations and supporting technology to include, then documenting exclusions with justifications linked to business risk. Scoping criteria should consider interfaces with third parties, cloud services and regulatory obligations to avoid later surprises during audit sampling. Practical tips include starting with critical business processes, mapping asset owners, and ensuring the scope is neither too broad (which dilutes focus) nor too narrow (which leaves unmanaged interfaces). A clear scope statement, signed by top management, also demonstrates leadership commitment and makes audits more predictable for both the organisation and the certification body.
Effective scoping naturally leads to focused risk assessment and treatment, which we address next.
Wie führt man eine umfassende Risikoanalyse und -behandlung durch?
Risk assessment follows four core steps: identify risks to assets, analyse likelihood and impact using a risk matrix, evaluate risk against criteria and select treatment options, then document decisions and owners in the risk treatment plan. Use a simple likelihood-impact matrix to prioritise risks and tie each selected treatment to measurable controls and acceptance criteria in the SoA. Assigning risk owners and deadlines for treatments creates accountability and provides auditors with clear evidence of decision-making. Recent best practice includes documenting residual risk and demonstrating management acceptance during the management review to show governance over risk treatment.
Linking risk assessment outputs to implemented controls and the SoA ensures smoother audit verification and prepares the organisation for Stage 1 examination.
Wie gestaltet sich der Ablauf des ISO 27001 Zertifizierungsaudits?
A certification audit typically happens in two stages: Stage 1 is a documentation review to assess readiness and Stage 2 is an on-site evaluation of implemented controls and evidence of effectiveness. The information security audit process evaluates whether the ISMS is implemented as described, whether controls are operating, and whether the organisation meets ISO 27001:2017 requirements. Auditors sample records, interview staff and test controls to determine conformity; preparing traceable evidence, control logs and interview rosters speeds up verification. The comparison table below clarifies what to expect in each stage for planning and scheduling decisions.
| Audit Stage | Focus | Typical Duration / Deliverable |
|---|---|---|
| Stage 1 (Documentation Review) | Verify ISMS documentation, SoA and readiness | 1–2 days — Stage 1 report with findings and readiness assessment |
| Stage 2 (On-site Assessment) | Verify implementation and effectiveness of controls | 2–5 days depending on scope — Report with conformity findings |
| Surveillance Audits | Ongoing verification of ISMS maintenance | Annual or periodic — Surveillance report and actions |
| Recertification | Full reassessment for renewal | Every 3 years — Recertification decision and report |
This comparison shows auditors’ expectations and helps teams schedule staff availability and evidence collection; next we outline common Stage 1 tasks.
Was passiert im Stage 1 Audit: Dokumentenprüfung?
Stage 1 focuses on whether required documentation exists and whether the ISMS appears ready for on-site verification; auditors look for an up-to-date SoA, risk assessment records, policies, scope statement and internal audit outcomes. Typical findings include missing or inconsistent documentation, unclear ownership, or incomplete risk treatment evidence; these are documented as observations or minor nonconformities that should be addressed before Stage 2. Auditor tips include making key documents easy to find, preparing a document index, and ensuring responsible owners can explain decisions. Demonstrating that internal audits and management review have occurred is particularly persuasive during Stage 1 and often dictates the timing of Stage 2.
Preparing these documents reduces the likelihood of Stage 1 findings leading to delays in the certification timeline.
Wie läuft das Stage 2 Audit: Vor-Ort-Bewertung ab?
Stage 2 is an evidence-driven on-site assessment where auditors test controls, interview staff at different levels, and sample logged events to confirm control effectiveness. Auditors will walk through processes, observe technical and physical controls, review implementation records and verify corrective actions from internal audits; control sampling is risk-based and may include live demonstrations or access reviews. Typical day structure includes opening meeting, interviews with control owners, control testing sessions and a closing meeting summarising findings. Preparing staff with mock interview questions and ensuring easy access to logs, change records and incident history shortens audit time and improves outcomes.
These on-site activities lead into how nonconformities are classified and managed, which is the next major topic.
Wie werden Nichtkonformitäten erkannt und behoben?
Nonconformities are identified when the ISMS or its controls fail to meet ISO 27001 requirements or when evidence shows controls are ineffective; auditors classify findings as major or minor depending on severity and impact on the ISMS. Efficient corrective action requires structured root-cause analysis, documented action plans with owners and deadlines, and verification of effectiveness through evidence such as re-tests or trend data. Common pitfalls that cause nonconformities include insufficient internal audit coverage, missing evidence of control operation, and poorly defined scope or SoA. The table below categorises typical nonconformity types with suggested corrective actions and timelines to guide response prioritisation.
Ultimately, the true effectiveness of ISO 27001 is measured by its ability to prevent or minimize information security incidents and address any identified gaps, even after certification.
ISO 27001 Effectiveness: Measuring ISMS Success & Addressing Gaps
Effectiveness of ISO 27001 as an information security system is a measure of the expectation satisfaction level based on the organizational expectations prior to implementation of ISO 27001 and the actual results obtained after certification. Thus, effectiveness focuses on how well objectives have been achieved rather than how well processes have been followed. The effectiveness of ISO 27001 is in preventing or minimizing the exposure to information security incidents in the real world. In a scenario where there has been so much investment in adopting the framework and subsequent certification resulting in high levels of stakeholder assurance, the focus is to identifying the areas where it is effective. But more importantly, it also focus on the areas where there are gaps, leading to information security risks and/or an incident even in a situation where the framework is adhered to and certification against it exists. Companies that have ISO 27001 certification and audit
Effectiveness of ISO 27001, as an information security management system: an analytical study of financial aspects, NK Sharma, 2012
This table clarifies expectations for remediation and timelines so organisations can plan corrective action closures before certification decisions; the following section explains frequent audit pitfalls to avoid.
Welche häufigen Audit-Pitfalls sollten vermieden werden?
Organisations commonly trip on a handful of avoidable issues during certification: incomplete or poorly indexed documentation, internal audits that do not cover critical processes, ambiguous process ownership, and scope statements that omit key interfaces. To prevent these pitfalls, maintain a central evidence index, ensure internal auditors are competent and independent, and confirm that each control has an assigned owner who can demonstrate operation. Practical do/don’t guidance includes rehearsing interviews with staff, validating logs and demonstrating metrics that show control performance over time. Avoiding these mistakes reduces the risk of major nonconformities and helps ensure a smoother certification process.
Avoiding such pitfalls feeds directly into implementing robust corrective measures when issues do arise, which we describe next.
Wie implementiert man wirksame Korrekturmaßnahmen?
An effective corrective action process follows a concise template: identify the nonconformity, perform root-cause analysis (e.g., 5 Whys), define corrective actions with owners and deadlines, implement changes, and verify effectiveness with evidence and monitoring metrics. Use measurable success criteria such as reduced incident rates, completed re-tests or audit rechecks to demonstrate closure to auditors. Document all steps in a corrective action record and link outcomes to management review to show governance and continual improvement. Typical timelines vary by severity, but major findings should have documented remediation plans and interim risk mitigations while full corrective action is implemented.
This structured approach ensures corrective actions produce lasting change and provide auditors with verifiable closure evidence.
Wie sichert man die Aufrechterhaltung der Zertifizierung und kontinuierliche Verbesserung?
Maintaining certification requires scheduled surveillance audits, an active internal audit programme, ongoing risk assessment updates and a culture of continual improvement using methods such as PDCA (Plan-Do-Check-Act). Surveillance audits typically verify that the ISMS continues to operate and that corrective actions have remained effective, while recertification provides a periodic full reassessment. Modern approaches include automating evidence collection and control monitoring to reduce administrative load and improve responsiveness. Combining governance, monitoring and periodic re-evaluation creates the conditions for sustained compliance and measurable security improvements.
Sustained maintenance leads into specifics about surveillance timing and readiness preparation, followed by how AI tools aid efficiency.
Welche Bedeutung haben Überwachungsaudits und Rezertifizierungen?
Surveillance audits, typically conducted annually, focus on continued operation of the ISMS and closure of previous findings, while a full recertification audit occurs around the third year to renew certification status. Organisations should maintain audit-ready evidence between cycles: updated risk registers, records of control operation, internal audit results and management review minutes. A surveillance readiness checklist includes current SoA, recent incident records and evidence of implemented corrective actions, which simplifies auditor sampling. Keeping these artefacts current reduces the intensity of each surveillance visit and demonstrates ongoing commitment to information security.
Regular surveillance and recertification cycles maintain trust with customers and reduce the operational surprise of audits, creating a predictable compliance rhythm.
Wie unterstützt der Einsatz von KI-gestützten Audit-Tools die Effizienz?
AI-powered audit tools accelerate evidence mapping, automatically correlate documents with Annex A controls and surface documentation gaps that auditors typically query, shortening preparation time and focusing human audit effort where it matters. These tools do not replace auditor judgment but augment it by identifying patterns, automating repetitive checks and creating searchable evidence indices that auditors and ISMS owners can use during Stage 1 and Stage 2. Stratlane Certification Deutschland utilises AI-assisted audit tools as part of its certification service to increase efficiency and consistency across multi-country audits, supporting faster verification without compromising auditor oversight. Integrating AI into continuous monitoring and internal audits also produces trend data that strengthens management reviews and corrective action validation.
These capabilities make maintaining certification less labor-intensive while keeping auditors focused on high-value verification tasks.
For organisations ready to pursue certification, consider scheduling a readiness assessment with an accredited body and aligning internal audit cycles with surveillance schedules to keep the ISMS inspection-ready. Stratlane Certification Deutschland offers ISO 27001:2017 certification audit services across Europe and the UK, with accredited coverage in many countries and professional auditors supported by AI-powered tools to increase efficiency; their dual offering of ISO 9001 and ISO 27001 certification can be beneficial where procurement requires both quality and information security alignment.
- Plan audit readiness: Map evidence and owners for every Annex A control.
- Use automation where appropriate: Let AI tools surface gaps while auditors verify conclusions.
- Keep governance visible: Document management review decisions and link them to risk treatment.
These actions help organisations sustain certification and continuously improve their ISMS.