The Strategic Importance of Compliance for Companies: Unlocking Business Growth and ISO 9001 Certification Value
Compliance has become a strategic business function rather than a mere regulatory checkbox, and companies that treat it as such convert legal obligations into measurable commercial outcomes. This article explains how modern compliance frameworks intersect with operational excellence, risk management, and market access, and it shows why ISO 9001 certification is a practical mechanism that turns quality management into competitive value. Readers will learn what compliance means in a corporate context, core benefits and common risks, how ISO 9001 supports a risk-based QMS, actionable mitigation strategies, and the near-term trends (AI and data privacy) shaping compliance through 2025 and beyond. The following sections map the essentials: why compliance matters, ISO 9001’s role and real-world impacts, tactical risk-mitigation steps, regulatory alignment approaches, how compliance drives client trust, and emerging trends that require strategic planning. Throughout, the article integrates practical examples, semantic relations between standards and processes, and targeted frameworks you can apply to align compliance with business growth objectives.
Why is Compliance Essential for Modern Businesses?
Compliance is the set of laws, regulations, standards, and internal policies that govern how an organisation operates, and it ensures legal conformity while protecting business continuity. By embedding compliance into operations, companies reduce legal exposure, enable consistent service delivery, and secure access to regulated markets, which in turn supports revenue stability. Recent studies indicate the financial impact of non-compliance can include fines, litigation costs, and lost contracts, making proactive compliance an economic imperative rather than just a reputational one. The next section unpacks the primary benefits that make compliance a business enabler rather than a cost centre, showing how documented processes and controls convert requirements into performance advantages.
What Are the Core Benefits of Corporate Compliance?
Core compliance benefits span reputation, operational quality, and legal protection, each reinforcing the others in business practice. Enhanced reputation arises because third-party audits and documented controls build stakeholder trust, which improves supplier relationships and investor confidence. Operational efficiency results from standardised processes and documented procedures that reduce defects and rework, supporting better margins and consistent delivery. Legal protection is achieved through timely identification of regulatory obligations and documented evidence that mitigates penalties and supports defence in audits. These benefits together create an environment where compliance supports growth rather than constrains it, paving the way for standards-based initiatives like ISO 9001 to deliver measurable outcomes.
- Reputational Protection: Public evidence of controls increases stakeholder trust and reduces scrutiny.
- Operational Efficiency: Standardised processes reduce defects and the cost of quality.
- Legal and Financial Safeguards: Documented compliance lowers the risk of fines and contractual disputes.
These core benefits naturally lead into a discussion of how specific controls mitigate the principal business risks organisations face.
How Does Compliance Mitigate Business Risks?
Compliance mitigates a spectrum of business risks by identifying obligations, defining controls, and establishing monitoring mechanisms that reduce uncertainty and exposure. Legal and regulatory risks are addressed through registers and compliance checks that ensure timely adherence to laws; operational risks are mitigated by process controls, training, and formal corrective actions; data privacy and cybersecurity risks are managed through policy, technical safeguards and alignment with related standards. Continuous improvement cycles—internal audits, management reviews, and CAPA—ensure that risk controls evolve as the business context changes. Understanding these mechanisms prepares organisations to implement targeted controls that reduce incident frequency and severity while improving resilience and supplier stability.
- Risk identification: Map regulations and obligations to processes for prioritized controls.
- Control implementation: Apply documented procedures and technical safeguards to reduce exposures.
- Monitoring and improvement: Use audits and reviews to close gaps and improve risk posture.
This mapping of risks to controls sets the stage for exploring how ISO 9001 specifically enhances compliance and business outcomes.
How Does ISO 9001 Certification Enhance Compliance and Business Success?
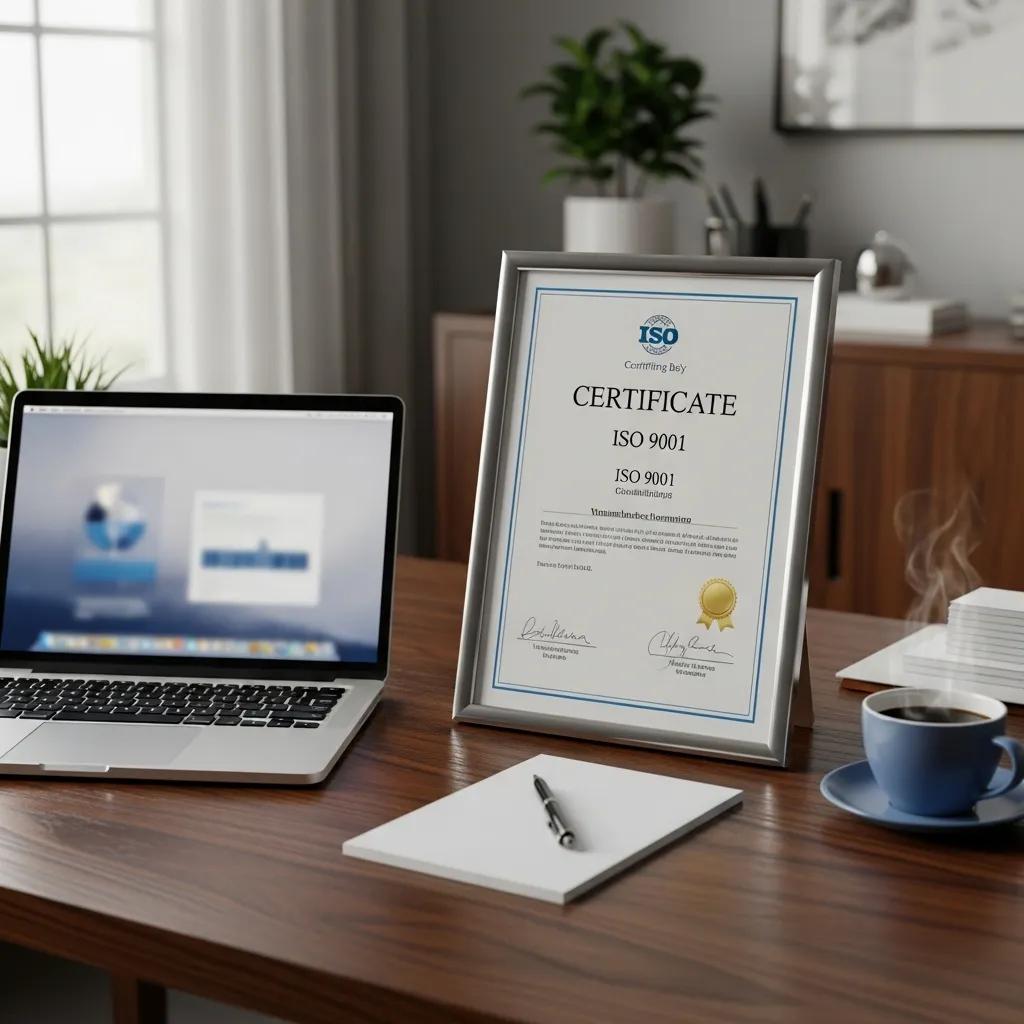
ISO 9001 is a structured Quality Management System (QMS) standard that operationalises compliance through a process approach, Plan-Do-Check-Act cycles, and risk-based thinking, thereby converting requirements into auditable practices. The standard’s clauses require documented processes, performance measurement, internal audits, and management review—mechanisms that provide tangible evidence of control to regulators and purchasers. Practically, ISO 9001 reduces variation, lowers defect rates, and improves supplier control, which supports higher customer satisfaction and tender eligibility. The table below maps ISO 9001 features to business attributes and outcomes to make that relationship explicit and actionable.
| QMS Feature | Operational Attribute | Business Outcome |
|---|---|---|
| Process Approach | Standardised workflows and responsibilities | Reduced process variation and defects |
| Documented Procedures | Traceable records and evidence | Faster audits and regulatory confidence |
| Internal Audits | Systematic verification | Early issue detection and corrective action |
| Management Review | Executive oversight and priorities | Strategic alignment and continual improvement |
This table highlights how ISO 9001 establishes the documented controls and measurement systems that satisfy both compliance demands and commercial expectations. The following subsections explain specific QMS improvements and why many clients view ISO 9001 as a procurement requirement.
What Value Does ISO 9001 Bring to Quality Management Systems?
ISO 9001 drives practical QMS improvements by enforcing standardized processes, consistent measurement, and continual improvement mechanisms that directly reduce defects and variability. By requiring documented procedures and KPIs, the standard ensures that teams can measure performance, identify root causes, and implement corrective actions that improve product and service quality. Internal audits and supplier controls increase transparency across the value chain, enabling better supplier qualification and reduced supply disruption. These improvements translate into quantifiable benefits like fewer customer complaints, shorter lead times, and better alignment between production and market demand, which together support higher customer satisfaction and commercial resilience.
- Standardisation: Clear process ownership reduces errors.
- Measurement: KPIs enable improvement and transparency.
- Supplier control: Audits and requirements improve upstream quality.
These practical QMS gains help explain why ISO 9001 often appears in procurement criteria for larger clients and regulated tenders.
Why Is ISO 9001 Certification a Requirement for Key Clients?
Yes — ISO 9001 certification is often a de facto requirement for key clients because it provides independent, evidence-based assurance that a supplier operates a controlled QMS. Procurement teams use certification as a quick filter to reduce due diligence time, ensure baseline quality controls, and lower supply chain risk. Certification supports eligibility for public tenders and large enterprise contracts where regulatory compliance and consistent delivery are prerequisites. For buyers, ISO 9001 simplifies supplier assessment by offering demonstrated audit trails, documented procedures, and management oversight that reduce onboarding friction and contractual risk.
- Procurement efficiency: Certification reduces the need for exhaustive supplier reviews.
- Supplier assurance: Third-party audits provide independent verification of controls.
- Risk reduction: Certified suppliers present lower operational and delivery risk.
Understanding ISO 9001’s role in procurement naturally leads to practical strategies companies can adopt to mitigate compliance risks effectively.
What Strategies Can Companies Use to Mitigate Compliance Risks Effectively?
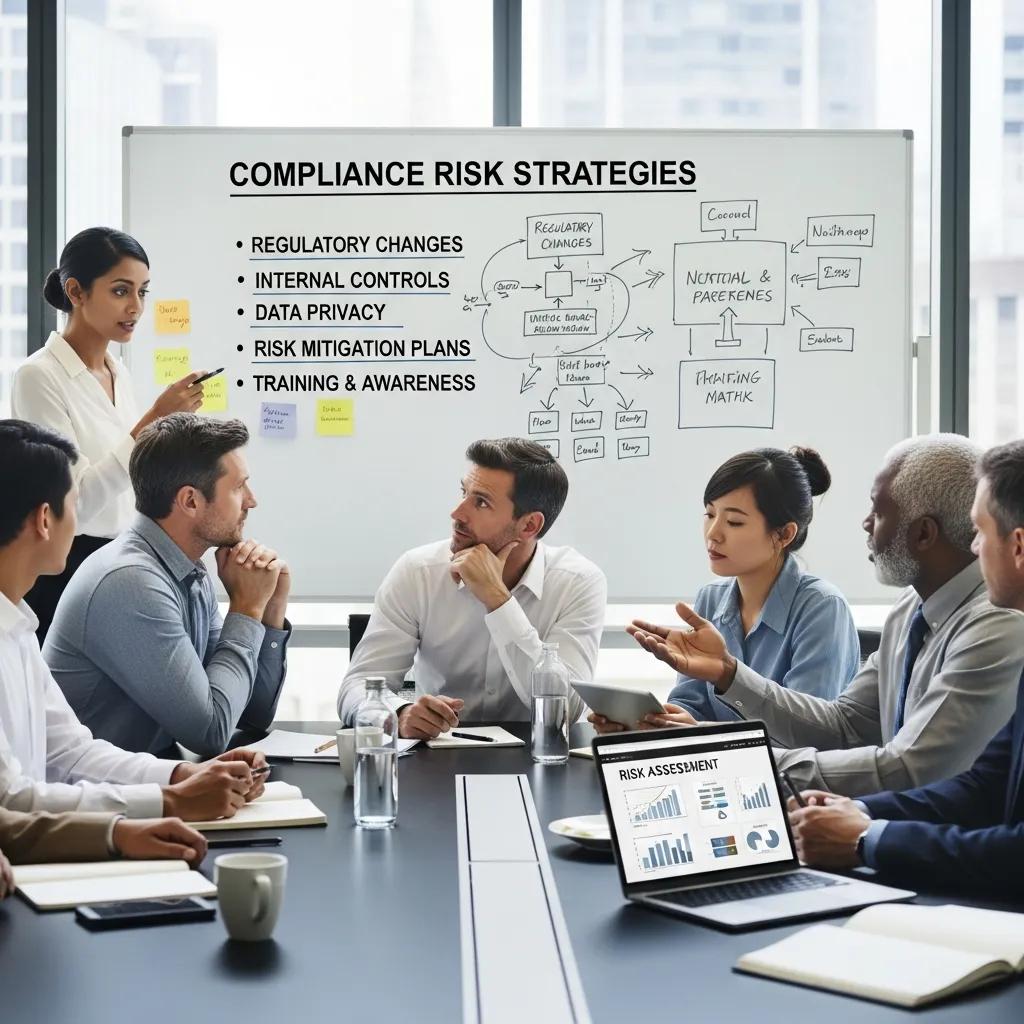
An effective compliance strategy combines governance, process controls, people, technology, and external validation to create layered defenses against regulatory and operational risk. Start with governance structures that assign ownership, maintain a regulatory register, and prioritise obligations by impact. Implement process controls, documented procedures, and internal audits tied to KPIs to operationalise compliance. Leverage technology for monitoring and evidence collection, and consider third-party certification such as ISO 9001 to validate controls externally. Below is a practical EAV-style comparison mapping mitigation entities to attributes and expected values to help you prioritise interventions.
| Mitigation Entity | Characteristic | Expected Value |
|---|---|---|
| Internal Audit | Frequency, scope | Increased issue detection rate |
| Document Control | Versioning, accessibility | Traceable audit trails |
| Supplier Assessment | Criteria, sampling | Reduced supplier failure incidents |
| Training Program | Coverage, refresh rate | Improved compliance adherence |
These strategic elements work together: governance defines priorities, process controls implement them, technology scales monitoring, and certification provides objective evidence. When applying these strategies, consider providers that combine domain expertise with automation to accelerate audit cycles and evidence aggregation. For example, Stratlane Certification Deutschland offers ISO 9001 certification services and combines experienced auditors with AI-enabled auditing capabilities to streamline assessments and deliver auditable results; their approach exemplifies how third-party certification can integrate with in-house governance to close compliance gaps efficiently.
How Does ISO 9001 Support a Risk-Based Approach to Compliance?
ISO 9001 operationalises risk-based thinking by requiring organisations to identify, assess, treat, and monitor risks within their processes, linking risk assessment directly to controls and performance measurement. The standard encourages process mapping and failure-mode thinking so that risk identification becomes part of everyday management rather than an annual exercise. A typical risk workflow under ISO 9001 begins with risk identification during process design, proceeds to risk assessment with likelihood and impact scoring, defines treatments such as controls or contingency plans, and concludes with monitoring through KPIs and audits. Embedding this workflow ensures mitigations are proportionate and measurable, and that management reviews feed corrective actions back into process design.
Academic research further underscores the importance of ISO 9001’s risk-based approach, particularly for smaller enterprises.
ISO 9001:2015 Risk-Based Thinking for SMEs
The purpose of this paper is to theorize and prioritize the main categories of risk sources for the European manufacturing small- and medium-sized enterprises (SMEs) in accordance with the International Organization for Standardization (ISO) 9001:2015 requirement
Risk-based thinking according to ISO 9001: 2015 standard and the risk sources
European manufacturing SMEs intend to manage, A Chiarini, 2015
- Identify: Map process risks during design and change control.
- Assess: Use scoring to prioritise remediation.
- Treat and Monitor: Apply controls, measure effectiveness, and update management review.
This risk-based integration is effective for both regulatory alignment and continuous quality improvement.
What Are Common Compliance Risks and How to Address Them?
Common compliance risks include regulatory non-conformance, data privacy breaches, supplier failures, and operational process breakdowns; each requires targeted mitigation strategies. Data privacy risks should be addressed with technical controls, privacy impact assessments, and alignment with related standards like ISO/IEC 27001 where appropriate. Supplier risks call for qualification criteria, periodic audits, and contractual clauses that require evidence of controls. Operational failures are best handled by root cause analysis, corrective actions, and process redesign to remove recurring failure modes. The short mitigations below pair typical risks with practical responses.
- Regulatory non-conformance: Maintain a regulatory register and perform gap analyses.
- Data privacy breaches: Implement encryption, access controls, and DPIAs.
- Supplier failure: Enforce supplier audits and performance KPIs.
- Process breakdowns: Use CAPA and FMEA to identify and remediate root causes.
Mapping risks to specific controls and monitoring their effectiveness through KPIs ensures organisations can proactively manage exposures rather than reacting to incidents, which leads into how enterprises can navigate regulatory compliance in practice.
How Can Regulatory Compliance Be Navigated Successfully by Enterprises?
Successful regulatory navigation requires a proactive, structured approach: maintain a regulatory watch, map regulations to business processes, conduct gap analyses, prioritise remediation by risk and customer impact, and embed change management and training. Create an internal alignment plan that assigns responsibilities, timelines, and resource estimates for compliance initiatives, and integrate regulatory mapping into your QMS so that process changes reflect legal requirements. Use standards like ISO 9001 to provide documented evidence of controls that regulators and customers expect, and ensure management reviews include regulatory changes and adaptation plans. The next subsections show how ISO 9001 maps to regulatory requirements and provide a tactical alignment checklist.
What Role Does ISO 9001 Play in Meeting Regulatory Requirements?
ISO 9001 supplies structural evidence—documented procedures, records, and audit trails—that regulators and auditors seek when evaluating compliance. Specific clauses such as document control, control of nonconforming outputs, and management review directly correspond to typical regulatory expectations for traceability, corrective action, and executive oversight. By mapping ISO 9001 clauses to regulatory checkpoints, organisations can present consistent evidence during inspections and reduce the burden of ad hoc documentation requests. This structural alignment accelerates regulatory responses and demonstrates a committed approach to governance, which benefits both audits and client assurance.
- Document Control: Ensures current procedures and records are available for audits.
- Nonconformance Management: Demonstrates corrective action and prevention measures.
- Management Review: Shows executive accountability and continual improvement.
These alignments make ISO 9001 a pragmatic tool for regulatory resilience and compliance readiness.
How to Align Business Processes with Evolving Compliance Regulations?
Aligning processes to evolving regulations begins with a gap analysis that compares current controls to new or changing requirements, followed by prioritisation of remediations by risk and client impact. Implement process redesign where necessary, update documented procedures, roll out targeted training, and monitor effectiveness through KPIs and internal audits. A practical alignment checklist includes assigning an owner for each regulatory change, defining milestones, updating systems and contracts as needed, and validating changes through internal audit before formal release. Timelines vary by scope, but short iterations with focused pilots accelerate implementation and reduce business disruption.
- Gap analysis: Identify differences between current controls and new requirements.
- Prioritisation: Score changes by risk and client impact to allocate resources.
- Implementation: Update processes, train staff, and validate through audit.
This tactical approach supports continuous alignment and reduces the time between regulatory change and compliant operation, which in turn enhances competitive positioning and client trust.
How Does Compliance Drive Competitive Advantage and Client Trust?
Compliance translates into market value by signalling reliability and consistency, which prospects and procurement teams use to reduce perceived risk in vendor selection. Certification and documented controls serve as sales differentiators during tendering and can shorten contract negotiations by reducing buyer due diligence. Consistent delivery enabled by a robust QMS leads to higher customer satisfaction and retention, which amplifies lifetime customer value. The EAV table below summarises ROI-oriented comparisons that demonstrate how compliance investments map to access and trust outcomes.
| Investment | Attribute | Commercial Impact |
|---|---|---|
| ISO 9001 Certification | Market access | Eligibility for large tenders and RFPs |
| QMS Process Improvement | Defect reduction | Lower cost of quality and improved margins |
| Customer-facing SLAs | Transparency | Higher retention and repeat business |
This table shows how specific compliance investments convert into market advantages and client trust; the following subsections unpack credibility signals and customer satisfaction mechanisms.
In What Ways Does ISO 9001 Certification Boost Market Credibility?
ISO 9001 functions as a third-party credibility signal that procurement teams and clients recognise during vendor selection, because it demonstrates that an organisation maintains auditable processes and management oversight. Certification reduces the perceived risk associated with a supplier by providing independent verification of controls, which simplifies supplier vetting and improves the speed of contract award. Audit reports and certificate status are tangible credentials that sales teams can leverage in tenders and proposals to differentiate offerings. These credibility signals translate into fewer barriers when entering regulated markets and greater confidence from enterprise buyers.
- Third-party validation: Independent audits reduce buyer uncertainty.
- Procurement efficiency: Certified suppliers face fewer qualifiers in RFPs.
- Sales differentiation: Certification strengthens bid positioning.
These credibility benefits culminate in improved commercial outcomes, including higher win rates and smoother onboarding for new clients.
How Can Compliance Enhance Customer Satisfaction and Retention?
Compliance enhances customer satisfaction by ensuring consistent service delivery, transparent processes for complaints and corrective actions, and measurable SLAs that clients can rely on. A robust QMS reduces variability in product or service quality, which decreases complaint rates and shortens resolution times through documented CAPA processes. Structured feedback loops tied to management review demonstrate responsiveness and continuous improvement, strengthening long-term relationships and reducing churn. Measurement KPIs—such as on-time delivery, defect rate, and complaint resolution time—provide objective indicators of performance that correlate with higher retention and increased customer lifetime value.
- Consistent quality: Standardised processes reduce variability and improve satisfaction.
- Structured resolution: CAPA processes shorten complaint-to-resolution cycles.
- Transparency: Clear SLAs and reporting build client confidence.
Because ISO 9001 and related standards act as enablers for these practices, many buyers explicitly require certification as part of qualification—making compliance an integral part of commercial strategy. If you are evaluating certification, consider providers that combine accreditation with modern auditing methods: Stratlane Certification Deutschland operates with experienced auditors and AI-enabled auditing to streamline assessments and provide auditable evidence across multiple jurisdictions, supporting companies seeking certification to access new tenders and increase client trust.
What Is the Future of Compliance: AI, Data Privacy, and ISO Certification?
The future of compliance is defined by automation, continuous monitoring, and heightened data privacy expectations; AI will accelerate evidence collection and anomaly detection, while regulations will demand greater transparency and governance around automated decision-making. Continuous compliance models—where monitoring and evidence aggregation happen in near real-time—will reduce audit cycle time and provide earlier alerts for control failures. Data privacy trends such as AI transparency, data residency rules, and stricter consent regimes will require QMS processes to integrate privacy-by-design principles. Organisations should prepare by investing in data governance, model oversight, and audit-capable evidence systems to remain compliant and competitive.
How Is AI Transforming Compliance and Certification Processes?
AI transforms compliance by automating data sampling, anomaly detection, and evidence aggregation, enabling auditors to cover larger data sets more quickly and identify patterns that manual reviews might miss. Automated tools can extract records, correlate events with controls, and flag deviations for human review, accelerating audit cycles and improving coverage. However, AI requires governance: model validation, explainability, and human oversight are essential to ensure automated findings are defensible during certification or regulatory review. Properly governed, AI enhances the speed and depth of compliance assessments while maintaining the need for experienced auditors to interpret results and make contextual judgements.
Recent studies highlight how AI is revolutionizing compliance audits by leveraging advanced analytics to streamline the process.
AI-Driven Compliance Audits for Regulatory Adherence
AI-based compliance auditing leverages machine learning, natural language processing (NLP), and automation to identify regulatory breaches, pull out evidentiary matter, and deliver audit findings faster and more consistently. This paper suggests a hybrid compliance-audit model that integrates transformer-based NLP for contract and regulation interpreting, supervised anomaly detection with the transaction and reporting stream, and explainability layer mapping model outputs to regulation clauses and audit trails.
AI-Driven Compliance Audits: Enhancing Regulatory Adherence in Financial and|
Legal Sectors, ST Gandhi, 2023
Further research demonstrates the potential of AI-driven process mining to automate continuous compliance monitoring, identifying deviations and risks in real-time.
Automated Compliance Monitoring with AI Process Mining
This paper addresses the solutions to these challenges by proposing anAI-driven process mining solution that helps automate the process of compliance monitoring in business processes. Integration of process mining techniques with artificial intelligence (AI) enables organizations to continuously monitor, audit, and assure adherence to regulatory standards more accurately. Using AI, this solution analyzes event logs identifies deviations of compliance rules and potential risks in real-time, and helps businesses proactively tackle these before they explode.
AI-Driven Process Mining for Automated Compliance Monitoring, K Babu, 2025
- Automation: Faster evidence collection and anomaly detection.
- Scalability: Broader coverage across processes and suppliers.
- Governance need: Model validation and human oversight ensure reliability.
These capabilities point toward continuous certification models that blend automated monitoring with periodic human-led audits.
What Emerging Trends in Data Privacy Impact Compliance Strategies?
Emerging data privacy trends—such as increased scrutiny of AI processing, cross-border data transfer restrictions, and requirements for transparency—demand changes to contracts, DPIAs, and operational processes. Organisations will need to implement privacy-by-design in product development, maintain clear records for data processing activities, and ensure contracts with vendors include robust privacy clauses. Tactical recommendations include updating privacy policies, conducting DPIAs for AI projects, and specifying data residency or transfer mechanisms where required. These steps reduce regulatory risk and align QMS procedures with modern privacy expectations, ensuring that compliance efforts remain relevant as laws and expectations evolve.
- AI transparency: Document how models use personal data and decision logic.
- Data residency: Map data flows and apply appropriate transfer safeguards.
- Privacy-by-design: Embed privacy requirements into process changes and product roadmaps.
Preparing for these trends ensures your compliance framework can adapt quickly and continue to provide evidence for both regulators and clients.
For organisations ready to translate compliance into measurable business advantage, certification remains a powerful lever. If your procurement or customer base requires ISO 9001 as a qualifying condition—or you seek an external audit that combines expert review with modern, AI-enabled evidence aggregation—Stratlane Certification Deutschland provides ISO 9001 certification services and accredited audits across multiple countries. Located in Düsseldorf, Stratlane blends experienced industry auditors with AI-capabilities to streamline assessments and help organisations meet client requirements and tender eligibility.
- Request a consultation: Evaluate readiness for ISO 9001 certification and tender qualification.
- Assess scope: Map processes, regulatory obligations, and supplier dependencies.
- Plan certification: Define timelines and evidence collection tailored to client and regulatory needs.
By treating compliance as strategic infrastructure, companies can reduce risk, improve operational performance, and access new markets with greater confidence.