Kartellrecht-Compliance: How ISO 9001 Certification Enables Effective Antitrust Compliance Programs
Kartellrecht-Compliance (antitrust compliance) means designing systems, policies and controls that prevent cartels, price fixing, bid rigging and other competition-law breaches while creating auditable evidence for regulators and customers. This article explains why organisations in 2025 face heightened competition-law risk, how ISO 9001’s quality management principles map to antitrust controls, and how a formal Quality Management System (QMS) produces traceable documentation that reduces legal and procurement exposure. Readers will gain a practical, ISO-aligned blueprint for risk assessment, policy design, role-based training, monitoring and continuous improvement, plus concrete examples of how certification evidence supports procurement and client requirements. The piece also outlines how AI-powered audits accelerate evidence collection and how Stratlane Certification Deutschland’s certification services can be used strategically to demonstrate controls to key clients. Begin with a clear definition of Kartellrecht-Compliance and the enforcement trends shaping corporate priorities in 2025.
What is Kartellrecht-Compliance and Why is it Crucial for Businesses in 2025?
Kartellrecht-Compliance refers to organisational measures that ensure adherence to competition law and prevent anti-competitive conduct such as cartels, bid rigging, and unlawful information exchange. The mechanism that makes compliance effective is a structured management system combining risk identification, documented procedures, and monitoring to detect and prevent harmful conduct, which delivers value by reducing fines and procurement losses. Current enforcement trends in 2024–2025 include increased cross-border cooperation among competition authorities, growing scrutiny of algorithmic pricing and data-driven coordination, and greater attention to procurement-related exposures. These shifts mean senior leaders, procurement heads and IT directors must prioritise controls that are auditable and demonstrable to regulators and key customers.
What are the Key Elements of an Antitrust Compliance Program?
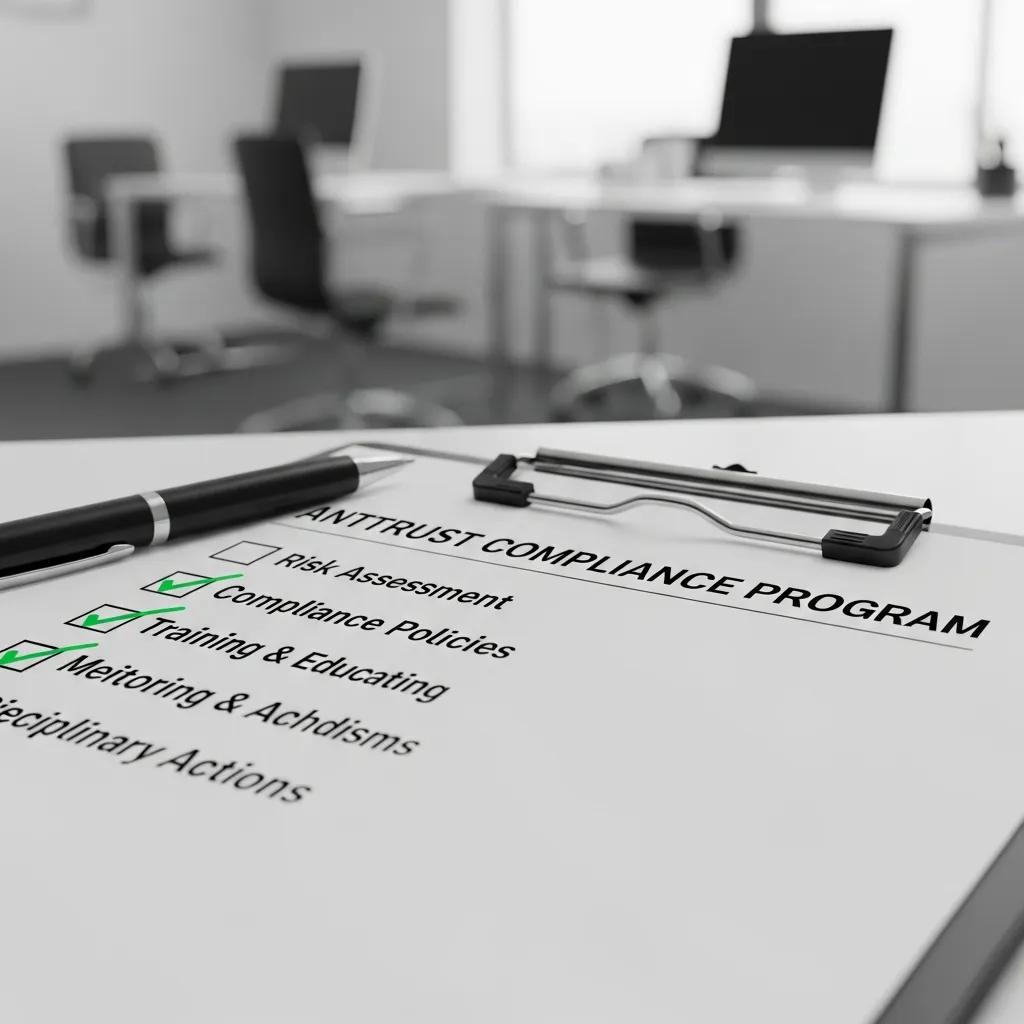
An effective antitrust compliance program combines governance, policies, risk assessment, training, monitoring and remediation in a structured framework that produces evidence for audits and investigations. Tone from the top provides leadership commitment and assigns responsibilities to a compliance officer, while written policies articulate prohibited behaviours and escalation routes. Risk assessments identify vulnerable processes—procurement, pricing algorithms and distribution agreements—and prioritise mitigations based on impact and likelihood. Training ensures that commercial, procurement and IT teams understand boundaries and reporting channels, and monitoring plus audits detect anomalies and feed corrective actions into management review, supporting continuous improvement.
Research further underscores the multifaceted nature of effective compliance, highlighting the interplay of deterrence, corporate ethics, and robust management systems.
Effective Competition Law Compliance Programs & Management Systems
The research has provided useful information on the development of competition law compliance culture. For instance, it confirmed the hypothesis that the experiences and perspectives of the particular company affects compliance. The research also provides some limited evidence to support the three key theoretical frameworks which are likely to underpin the establishment and maintenance of effective compliance: deterrence based on rational choice; moral corporate citizenship based on questions of legitimacy and sound corporate governance; and managerial competence based on operational effectiveness and adoption of sound management systems.
Competition law compliance programmes: A study of motivations and practice, 2005
The following checklist summarises the program elements organisations should implement:
- Governance and leadership accountability with defined roles and reporting lines.
- Written antitrust policies and procedures tailored to commercial practices.
- Risk assessment and mitigation tied to processes like procurement and pricing.
These elements create a defensible posture that regulators and customers can verify during procurement checks.
What are the Consequences of Non-Compliance with Competition Law?
Non-compliance with competition law can trigger significant fines, civil damages, criminal exposure for individuals in some jurisdictions, and severe reputational harm that affects sales and contracts. Financial penalties may reach substantial percentages of turnover, while civil claims and follow-on damages can amplify total liability and create long-term cash flow impacts. Procurement consequences include disqualification from tenders and the loss of key clients who require demonstrable controls as a condition of supply. Reputational damage reduces partner trust and can restrict market access, making prevention and documentation crucial to commercial continuity.
Typical impacts to anticipate:
- Large monetary fines and ongoing compliance costs.
- Contractual exclusions and procurement losses.
- Reputational erosion affecting partnerships and market opportunities.
Understanding these consequences underscores why organisations must adopt systematic, auditable controls rather than ad hoc compliance measures.
How Does ISO 9001 Support Kartellrecht-Compliance and Regulatory Adherence?
ISO 9001 provides an auditable Quality Management System framework—centered on risk-based thinking, documented information and PDCA cycles—that organisations can adapt to manage antitrust risks and produce reliable evidence for customers and regulators. The mechanism is straightforward: ISO 9001 requires clear process definitions, records of actions taken, monitoring and management review, which directly support detection, prevention and remediation of competition-law issues. Applying ISO principles to antitrust functions yields benefits such as consistent supplier interactions, traceable decision-making on pricing and procurement, and demonstrable training records that procurement teams value.
This table maps core ISO 9001 clauses and principles to specific antitrust compliance functions and shows how each produces auditable outcomes.
| ISO 9001 Clause / Principle | Antitrust Compliance Function | Auditable Outcome |
|---|---|---|
| Context of the organisation & interested parties | Identify market positions, customers and procurement dependencies | Documented scope and supplier lists that inform risk assessments |
| Leadership & commitment | Assign accountability and decision authority for compliance | Management responsibility records and review minutes |
| Risk-based thinking & actions | Systematic antitrust risk identification and control selection | Risk registers, mitigation plans and acceptance records |
| Documented information & control | Procedure manuals, training records and contract templates | Versioned policies, training logs and contract change records |
This mapping demonstrates how ISO 9001 clauses create traceable records that serve both internal governance and external verification needs. The next section explains which specific ISO principles most directly reduce antitrust exposure.
Which ISO 9001 Principles Enhance Antitrust Risk Management Strategies?
Key ISO 9001 principles—process approach, risk-based thinking, documented information and continual improvement—each reduce antitrust risk by stabilising decision paths and evidence trails. The process approach standardises supplier engagement, pricing approval workflows and contract negotiation steps to prevent informal practices that can lead to unlawful coordination. Risk-based thinking mandates that organisations evaluate algorithmic and procurement vulnerabilities and implement controls proportionate to identified risks. Documented information creates immutable records—contracts, approvals and training logs—that serve as primary evidence in audits or investigations and support leniency and mitigation arguments.
Examples of implementation:
- Formal procurement workflows with approval gates and logged communications.
- Algorithm change controls and versioned model documentation.
- Centralised training records and periodic competence assessments.
These ISO-aligned controls feed into management review and drive continuous improvement, which is explored next.
How Does ISO 9001 Certification Strengthen Corporate Governance and Compliance Culture?
ISO 9001 certification formalises governance by requiring leadership involvement, defined responsibilities and documented management reviews that collectively sustain a compliance culture. Certification mechanisms compel organisations to measure performance via KPIs, record non-conformities and implement corrective actions, which embed accountability across commercial and operational teams. Training programs, competency records and audit schedules become part of the QMS, demonstrating to procurement teams and regulators that the organisation maintains repeatable, monitored processes. The cultural effect is measurable: higher audit completion rates, shorter remediation timelines and visible management oversight signal a mature compliance posture.
Governance actions that reinforce culture:
- Regular management reviews linking antitrust KPIs to strategic objectives.
- Role-based training with tracked completion and assessment.
- Non-conformance logs that drive root-cause analysis and systemic fixes.
These governance practices create the organisational discipline necessary to deter and detect competition-law violations.
How to Design an Effective Antitrust Compliance Program Aligned with ISO 9001 Standards?
Designing an ISO-aligned antitrust program begins with a structured risk assessment, proceeds to policy and control design using the process approach, and embeds training, monitoring and PDCA cycles to ensure ongoing effectiveness. The mechanism is iterative: risk identification informs procedural controls, documented information captures actions, monitoring identifies non-conformance, and management review triggers corrective measures. The value delivered is a defensible, auditable compliance system that integrates with existing QMS elements and produces evidence that customers and regulators accept.
Below is a practical implementation table showing how ISO-style attributes (training, monitoring, reporting) translate into concrete compliance tasks and examples.
| Attribute | Practical Implementation | Example |
|---|---|---|
| Training | Role-based learning paths with assessments and records | Commercial staff complete annual antitrust modules; completion logs retained |
| Monitoring | Routine audits plus data analytics for anomalies | Procurement audit schedule and AI-assisted anomaly reports on bidding patterns |
| Reporting | Clear escalation routes and documented incident handling | Incident forms, investigation records and corrective action plans |
This table clarifies how ISO 9001 process elements become operational compliance controls. The following subsections spell out best practices and implementation mechanics.
What are the Best Practices for Antitrust Risk Assessment and Policy Development?
Best practice begins with cross-functional risk workshops that include legal, commercial, procurement and IT to map markets, suppliers and algorithmic touchpoints. Use structured scoring—impact × likelihood—to prioritise risks and tie each prioritized risk to a specific control and owner, ensuring traceability. Policies should be concise, auditable and process-oriented: include prohibited behaviours, approval thresholds, permitted communications and contract clauses, with version control and change logs. Keep evidence retention rules clear so that investigation teams and auditors can retrieve communications, approvals and transaction records efficiently.
Practical policy drafting tips:
- Draft process maps for pricing and procurement approvals.
- Define clear escalation points and disciplinary consequences.
- Require standard contract clauses that limit information exchange.
These practices ensure policies are both enforceable and verifiable during audits and client due diligence reviews.
How to Implement Training, Monitoring, and Continuous Improvement for Compliance?
Implement role-based training with frequent refreshers and assessments, and retain completion records as documented information under the QMS. Monitoring should combine scheduled audits, spot checks and technology-assisted anomaly detection to surface suspicious patterns in procurement or pricing algorithms. Use KPIs—such as audit completion rate, number of detected anomalies and remediation lead time—to feed management review and PDCA cycles. Non-conformities must trigger root-cause investigations, corrective action plans and verification of effectiveness to close loops and show continuous improvement.
Sample KPIs and cadence:
- Annual antitrust training completion rate for commercial staff.
- Quarterly procurement audit coverage and remediation timelines.
- Monthly anomaly alerts from monitoring systems and follow-up actions.
These measures embed compliance into routine operations and supply a continuous stream of evidence for stakeholders and customers.
What are the Business Benefits of Integrating Competition Law Compliance with ISO 9001?
Integrating antitrust compliance with ISO 9001 delivers measurable commercial benefits: reduced legal exposure, stronger positions in procurement processes, improved reputation with clients and streamlined operations through standardised processes. The mechanism is that ISO 9001 turns ad hoc practices into documented, repeatable processes and produces records—policies, training logs and audit results—that procurement teams rely on when evaluating suppliers. This alignment not only mitigates enforcement risk but also shortens due diligence cycles and increases trust in tender evaluations.
Commercial advantages to expect:
- Lower legal risk through documented prevention and remediation.
- Procurement advantages: faster onboarding and fewer compliance queries.
- Operational efficiency from process standardisation and reduced rework.
Following these benefits, note that ISO 9001 certification increasingly becomes a requirement for doing business in certain supply chains; demonstrating certification and audit evidence helps organisations meet client expectations and secure contracts.
Integration note: For organisations that must prove controls to customers, ISO 9001 certification provides the auditable controls and documentation many major clients now expect as part of supplier eligibility. Certification shows clients that your organisation maintains documented processes, monitored performance and traceable corrective actions—factors that often determine procurement decisions and long-term supply relationships.
How Does ISO 9001 Certification Reduce Legal Exposure and Enhance Reputation?
ISO 9001 certification reduces exposure by documenting preventive controls, investigation routines and remediation measures that demonstrate proactive compliance to regulators and clients. The mechanism is evidential: versioned policies, training logs and audit trails show that the organisation took reasonable steps to prevent breaches and responded appropriately when issues arose. This demonstrable posture can mitigate penalties and influence leniency considerations during investigations, while also signalling to clients a low-risk supplier profile that enhances bid competitiveness.
Key reputational effects:
- Certification signals organisational maturity and lowers perceived vendor risk.
- Documented procedures shorten client due diligence times.
- Audit trails support transparent investigations and remediation.
These outcomes help organisations maintain and win contracts where compliance is a decision factor.
What Competitive Advantages Do Businesses Gain from Robust Compliance Programs?
Robust compliance programs shorten supplier onboarding, reduce the frequency of client audits, and improve bid success where clients prioritise certified controls and traceable processes. The mechanism is that consistent processes reduce variability and provide predictable outcomes for customers, while certification acts as third-party validation of those processes. In sectors like IT and manufacturing, documented algorithm controls or procurement workflows can be decisive differentiators in tender evaluations and strategic partnerships.
Competitive outcomes to quantify:
- Faster contract awards due to reduced compliance friction.
- Distinctiveness in bids where certification is a selection criterion.
- Lower internal costs from standardised procedures and fewer remediation cycles.
These advantages translate into clearer commercial value from investing in ISO-aligned compliance systems.
How Does Stratlane Certification Deutschland Facilitate Kartellrecht-Compliance with AI-Powered Audits?
Stratlane Certification Deutschland offers certification services focused on ISO standards and leverages AI-powered audit tools to accelerate evidence collection, identify anomalies and produce reproducible audit outputs that align with antitrust compliance requirements. The mechanism is tool-assisted audit automation: AI collates documented information, highlights deviations from defined processes and produces structured reports that feed directly into the QMS evidence base. The value for clients is faster audit cycles, clearer evidence for procurement teams and tailored guidance to meet industry-specific antitrust risks while preparing for certification.
Stratlane’s approach combines experienced auditors with technology to scope certification around antitrust-relevant processes, producing outputs clients can present during procurement checks or regulatory inquiries. This integration showcases how certification is not merely a label but a practical source of verifiable controls and documentation that clients demand.
What are the Advantages of AI-Enhanced Auditing in Compliance Verification?
AI-enhanced auditing speeds evidence collation, detects patterns and anomalies across large datasets, and improves reproducibility of audit findings compared with manual-only reviews. The mechanism uses algorithms to surface irregularities in procurement timelines, pricing changes and contract edits that may signal antitrust exposure, enabling auditors to focus on high-risk items. This produces value through reduced time-to-certification, more frequent continuous monitoring options and richer audit trails that are easier to present to clients and regulators.
Primary benefits include:
- Automated evidence aggregation and anomaly detection.
- Scalability for reviewing large transaction and communication datasets.
- Consistent, reproducible audit outputs that strengthen evidentiary value.
These capabilities allow organisations to maintain a stronger, data-driven compliance posture between formal audits.
How Does Stratlane Tailor Certification Services for Industry-Specific Antitrust Risks?
Stratlane adapts audit scope, checklists and risk criteria to the unique antitrust exposures of sectors such as IT, manufacturing and complex supply chains, ensuring that certification addresses the most relevant controls. The mechanism is sector-specific scoping: auditors define key processes—algorithm governance for IT, bundling and procurement controls for manufacturing—and require evidence attuned to that exposure. Clients receive targeted audit reports and recommendations that reflect their operational realities and provide the specific documentation procurement teams expect.
Tailoring elements often include:
- Industry-specific checklists and risk matrices.
- Sector-relevant training modules and evidence requirements.
- Focused audit sampling on high-risk contracts and algorithm changes.
This targeted approach increases the practical relevance of certification for customers and reduces unnecessary audit burden.
Where Can Businesses Learn More and Get Support for ISO 9001-Based Antitrust Compliance?
Organisations seeking support should prepare to assess scope, document key processes and engage with certification bodies that understand both ISO 9001 and competition-law risk. The mechanism for initiating support includes an initial scoping assessment, gap analysis against ISO clauses and antitrust controls, followed by a tailored certification plan that outlines timelines, required documentation and audit stages. The value of a structured approach is a clear roadmap to certification and a set of auditable outputs that customers and regulators accept during procurement checks.
How to Request a Consultation or Certification Quote from Stratlane?
To request a consultation or a certification quote from Stratlane Certification Deutschland, prepare high-level information about your intended scope, relevant locations and any existing management systems or certifications. Typical preparatory items include a summary of business activities affecting competition risk, a list of key suppliers and information flows, and a rough estimate of entities or sites to be included in the certification scope. Expect an initial scoping conversation that yields a gap analysis and a proposed timeline for assessment and certification.
Steps to prepare for a consultation:
- Define the business scope and processes to be covered by certification.
- Compile existing policies, training records and key contract templates.
- Provide an overview of IT systems that influence pricing or procurement decisions.
These preparatory steps help ensure the consultation yields a realistic quote and an actionable certification plan that supports procurement and client requirements.
What Additional Resources and Training Are Available for Competition Law Compliance?
Organisations should combine official guidance from competition authorities with practical training formats—executive briefings, role-based e-learning and scenario workshops—to build and maintain antitrust competence. Recommended resources include regulatory guidance documents and industry-specific compliance manuals, while training should be frequent, role-specific and outcome-measured with retained records. Maintaining a regulatory watch and updating materials as enforcement focus evolves ensures the compliance program remains current and defensible.
Training and resource recommendations:
- Executive briefings for leadership on strategic antitrust risks.
- Role-based e-learning for commercial, procurement and IT teams.
- Scenario workshops and tabletop exercises to test incident response.
These resources, combined with ISO-aligned documentation practices, create a sustainable compliance capability that supports both internal governance and external procurement demands.