Lenkung von Dokumenten und Aufzeichnungen: Essential ISO 9001 Document Control Requirements for Quality Management Systems
Document and record control in ISO 9001 is the structured set of policies and processes that ensure documented information is created, approved, distributed, protected and retained to support consistent quality outcomes. This article explains what ISO 9001 expects for documented information, why document control matters for compliance and contracts, and how organisations can implement practical systems — including modern AI-assisted approaches — to reduce errors and speed audits. Readers will learn clause-mapped requirements, step-by-step implementation guidance, enterprise controls such as versioning and retention schedules, and industry-specific adaptations for sectors like automotive, healthcare and IT. The guide blends normative interpretation of clause 7.5 with actionable workflows, checklists and EAV tables to make translation into your QMS straightforward. If you manage Dokumentenmanagement, Aufzeichnungslenkung or are preparing for ISO 9001 certification, this resource lays out both the technical controls and the business rationale needed to achieve and defend compliance.
What is Document and Record Control in ISO 9001?
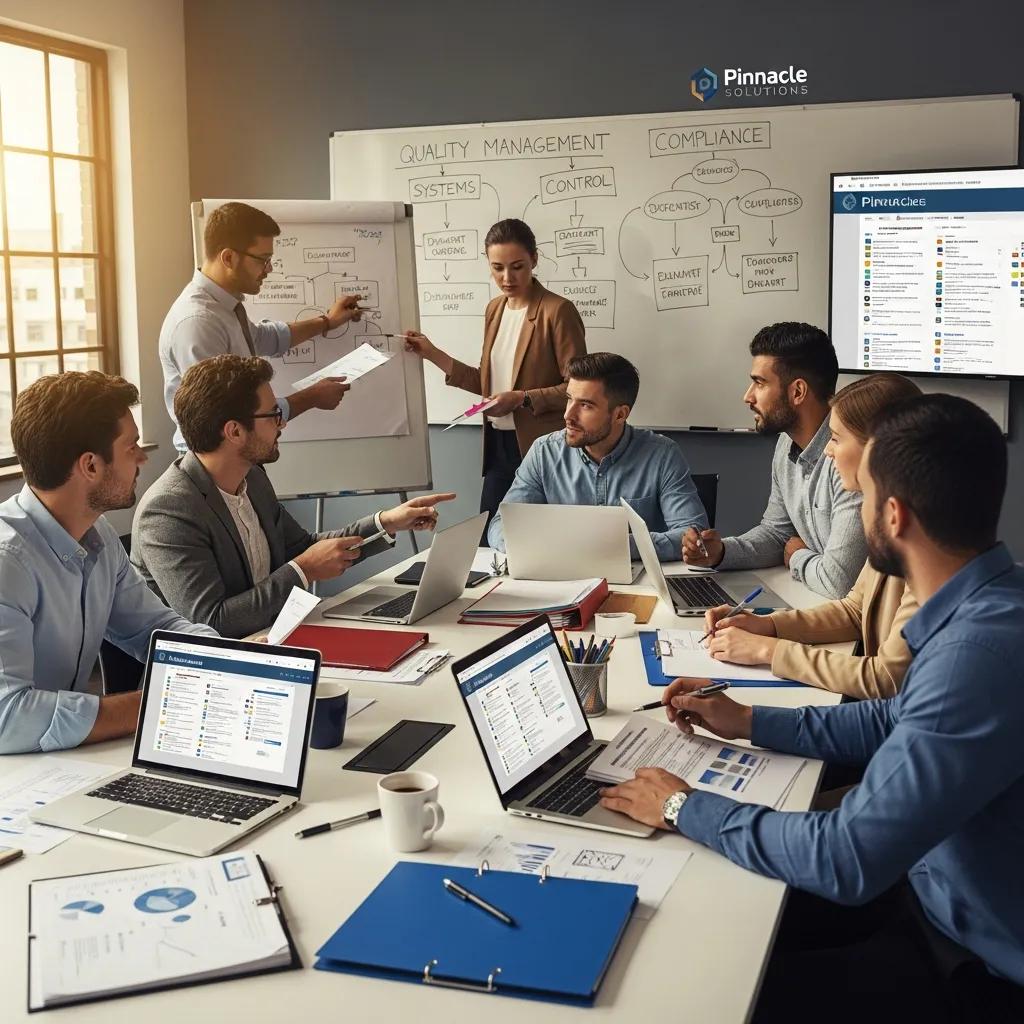
Document and record control in ISO 9001 refers to the governance of documented information that a Quality Management System (QMS) requires, ensuring it is accurate, available and protected to deliver consistent products and services. The mechanism combines creation rules, approval workflows, version control, access permissions and retention policies so that personnel always use the correct documented information and auditors can verify conformity. This control reduces process variation and supports traceability, which in turn lowers the risk of nonconformities and expedites corrective actions. Understanding this concept prepares organisations to map their documents and records to clause 7.5 and to prioritise controls that produce verifiable audit evidence.
How does ISO 9001 define Documented Information?
ISO 9001:2015 treats „documented information“ as any information required to be controlled and maintained by a QMS, including documents and records that demonstrate conformity. Clause 7.5 requires organisations to determine what documented information is necessary, how it will be created, updated and controlled, and to ensure appropriate protection and retention. Practically, forms, procedures, work instructions, quality plans and records such as inspection logs are all documented information when they are required to ensure process consistency. For example, a release checklist must include an owner, version number, approval signature and retention period so that evidence is available during an audit and daily operations use the current version.
Why is ISO 9001 Document Control Essential for Your Quality Management System?
Effective document control is essential because it links governance to operational reliability, compliance and customer trust, ensuring that processes are performed to the documented standard and evidence is available for audits and contracts. When documents are controlled, organisations reduce errors caused by obsolete instructions, accelerate onboarding, and maintain a defensible audit trail that demonstrates due diligence. These controls also support procurement and tender requirements where key clients or regulators demand documented evidence of control and retention as a condition of contract award. Demonstrating robust Dokumentenlenkung is therefore not only a quality initiative but a business imperative for market access and sustaining client relationships.
How does effective document control ensure compliance and audit readiness?
Effective document control ensures compliance by maintaining version histories, approval records and access logs that auditors can verify to confirm processes were followed as documented. Version control provides clear evidence of who approved changes and when, access controls demonstrate segregation of duties, and retention policies show that required records are available for the mandated period. A short audit-readiness checklist includes confirmed owners for critical documents, a searchable indexed repository, and documented disposition rules for obsolete records that preserve required retention evidence. These mechanisms reduce audit time and build confidence with stakeholders by making evidence retrieval predictable and reproducible.
Further research highlights how specialized systems can streamline these processes, enhancing both management and audit capabilities.
Expert Systems for QMS Document Management & Audits
This study discusses the development of an expert system for the QMS document management and internal quality audits.
An Expert System in Quality Management System Documents Management and Internal Quality Audits, YCA Tang, 2005
What operational efficiencies result from proper records control in QMS?
Proper records control drives measurable operational efficiencies such as faster document retrieval, fewer process errors and reduced time spent on corrective actions because teams use the correct, approved information. Centralised document management and standardized naming and indexing practices shorten search time and accelerate change implementation, which lowers lead times and supports continuous improvement cycles. Organisations often see reductions in rework and nonconformities when version control and distribution rules prevent the use of outdated procedures. These operational gains create a virtuous cycle: improved processes produce better records, and better records enable faster audits and stronger client confidence.
What are the Key ISO 9001:2015 Documented Information Requirements?
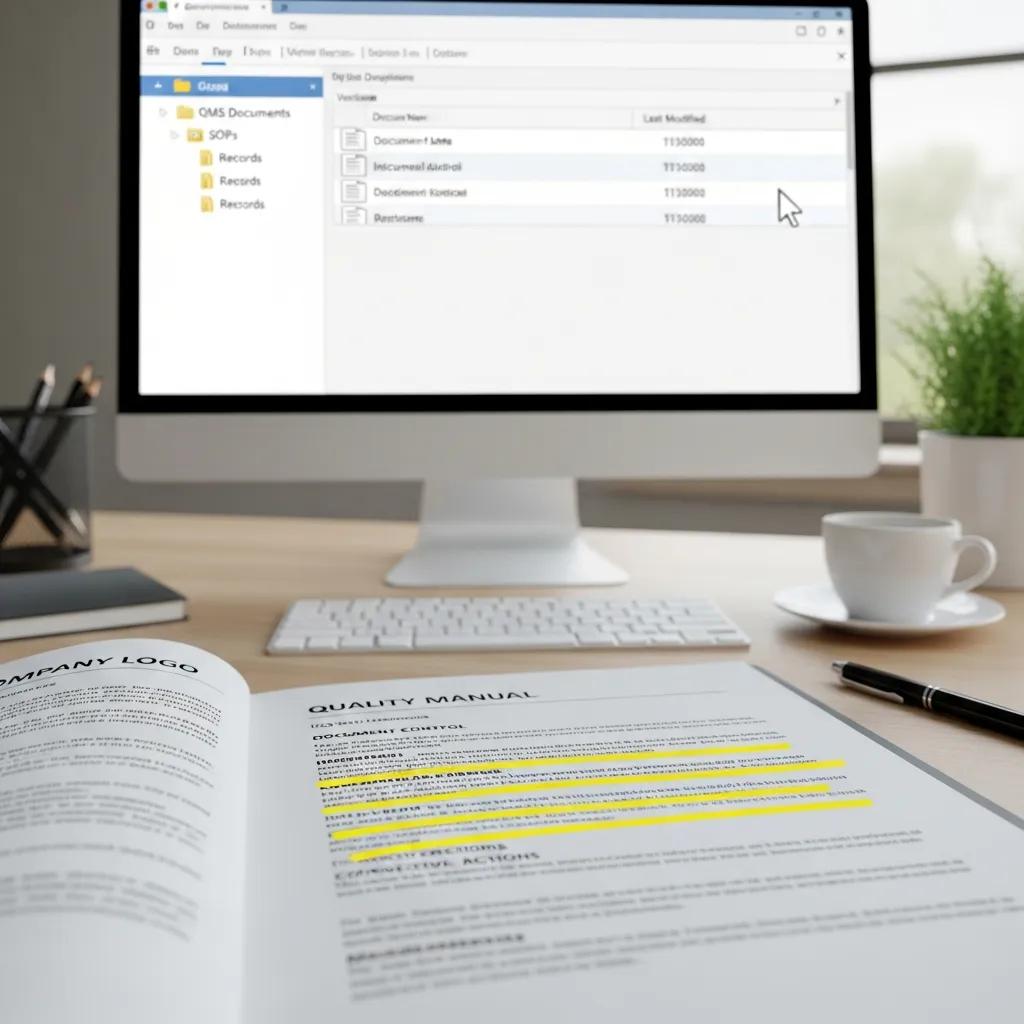
ISO 9001:2015 requires documented information to be identified, created, updated, approved, protected, and retained according to defined controls that maintain integrity and accessibility. Clause 7.5 is the core reference: it mandates that organisations determine the documented information necessary for the effectiveness of the QMS and implement controls proportionate to risk and complexity. Minimum attributes you should maintain for each document type include owner, version number, revision date, approval signature, storage location and retention period; these attributes form the backbone of compliant Dokumentenmanagement. Maintaining these attributes consistently creates audit evidence and supports traceability across processes.
Before the table below, this EAV-style summary maps common document types to essential attributes and example values for quick operational reference.
| Document Type | Required Attributes | Typical Value / Example |
|---|---|---|
| Procedure | Owner, Version, Approval, Location, Retention | Owner: QMS Manager; Version: v2.1; Retention: 5 years |
| Work Instruction | Owner, Effective Date, Access Permissions, Revision History | Owner: Process Lead; Effective: 2025-07-01; Access: Role-based |
| Record (inspection/test) | Recorder, Timestamp, Storage Location, Retention Period | Recorder: Inspector ID; Timestamp: ISO 8601; Retention: 3 years |
What are the document creation, updating, and approval procedures?
Document creation, updating and approval procedures should be formalised into a simple workflow that assigns responsibility for drafting, reviewing, approving and publishing documents, with controls for emergency changes. A recommended numbered workflow is an effective featured-snippet format:
- Draft by owner using approved templates
- Review by stakeholders with tracked comments
- Approval by authorised approver with electronic sign-off
- Publish to controlled repository with version assigned
- Communicate change and archive superseded versions
Governance must define who may initiate changes, who must approve them, and how exceptions are handled so the process remains auditable and defensible. Implementing templates and mandatory metadata fields reduces variability and accelerates approvals while preserving the audit trail necessary for compliance.
How should records be identified, stored, protected, and retained?
Records should be uniquely identified with a naming convention and version number, stored in a secure, indexed repository, protected by access controls and backups, and retained according to a documented retention schedule tied to regulatory or contractual requirements. Identification standards typically include document type code, owner initials, version and date to make retrieval deterministic. Storage options may be electronic within a Document Management System (DMS) or controlled physical archives; either approach must include protection measures such as role-based permissions, encryption where required, and regular backups. Retention schedules should be recorded in a disposition policy with evidence that retention and lawful destruction are executed per policy, ensuring auditability and legal defensibility.
How to Implement an Effective Document Control System for ISO 9001?
Implementing an effective document control system requires aligning people, processes and tooling: define scope and responsibilities, establish approval and versioning rules, create distribution processes, and select a DMS or controlled manual approach that enforces policies and produces audit evidence. Begin with a gap analysis mapping current documented information against clause 7.5 requirements, then prioritise high-risk documents for immediate control. Tool selection should balance simplicity and auditable features: metadata enforcement, immutable audit trails, role-based access and automated retention. Clear governance combined with training ensures the system is used consistently across teams and supports continual improvement.
Before the EAV comparison table, the following list outlines key implementation steps to guide teams in turning policy into practice.
- Define Scope and Owners: Map documents, assign owners and set governance roles.
- Standardise Templates: Use mandatory metadata fields and templates for consistency.
- Enforce Versioning: Implement clear version numbering and approval rules.
This numbered process provides a concise how-to that can be used as a checklist for implementation planning and rapid deployment.
| Control Area | Attribute | Recommended Approach |
|---|---|---|
| Document Approval | Tooling | Template + DMS workflow with electronic sign-off |
| Versioning | Enforcement | Automated version stamps in DMS; manual log if offline |
| Access Control | Security | Role-based permissions with regular reviews |
| Audit Trail | Evidence | Immutable logs in DMS; signed records for physical files |
| Retention | Enforcement | Automated disposition in DMS; documented schedule for physical |
What roles and responsibilities are critical in document management?
Critical roles include document owners who maintain content accuracy, approvers who validate suitability, DMS administrators who manage access and backups, and internal auditors who verify controls and evidence. A RACI-style approach clarifies who is Responsible, Accountable, Consulted and Informed for each document type and change activity, which prevents gaps in ownership and ensures timely approvals. For small and medium enterprises, owners and approvers can be combined but should still be distinct from those who administer the DMS to preserve segregation of duties. Regular role reviews and training keep responsibilities current and reduce the risk of orphaned documents or uncontrolled changes.
How to establish version control, accessibility, and distribution processes?
Version control conventions should use simple, predictable numbering such as Major.Minor (e.g., 3.1) together with an approval date and audit trail so users can confirm the current version at a glance. Accessibility policies define who can view, edit or publish documents and should be enforced via role-based access in a DMS or by locked folders and signed logs for physical files. Distribution rules should specify how external documents are released and tracked, including distribution logs or release forms for third-party recipients. Maintaining distribution logs and accessible version history reduces the risk of incorrect procedures being used and supports rapid corrective action when a change is required.
How Does AI Enhance Document and Record Control in ISO 9001 Certification?
AI enhances document and record control by automating classification, extraction of evidence, anomaly detection in revision histories and faster aggregation of audit evidence, which reduces manual effort and improves accuracy. Natural language processing (NLP) can auto-tag documents to required clauses, making search and evidence mapping to clause 7.5 more efficient. Anomaly detection highlights unexpected edits or unusual access patterns that could indicate compliance risk, allowing teams to investigate proactively. Together, these capabilities shorten audit preparation time and improve the defensibility of documented information.
Indeed, the application of artificial intelligence offers significant potential for improving the efficiency and accuracy of quality management systems.
AI for ISO 9001 Quality Management & Compliance
Artificial intelligence can be used to analyze large amounts of data and identify patterns, trends, and anomalies within a quality management system that an organization must meet as compliant with the standard.
Artificial intelligence in industry. Application of ISO 9001., 2023
Before the AI EAV table, here are two illustrative AI use-cases that show measurable benefits in audit efficiency.
- Auto-extraction: AI scans procedures and extracts required metadata and clause references, reducing evidence collection time by a measurable margin.
- Anomaly detection: Models flag unexpected changes or access patterns, enabling early remediation before an audit.
These examples show how AI converts manual tasks into auditable, repeatable processes that improve both speed and accuracy.
| AI Feature | Compliance Benefit | Example Metric / Outcome |
|---|---|---|
| Automated classification | Faster evidence mapping | Clause mapping time reduced by 60% |
| Field extraction | Accurate metadata population | 95%+ completeness on document attributes |
| Anomaly detection | Proactive risk detection | 30% fewer late-change findings in audits |
After outlining AI benefits, it is important to recognise how service providers can support adoption. Stratlane Certification Deutschland combines AI-driven audit tools with experienced auditors to help organisations meet ISO 9001 expectations and prepare defensible evidence for client and regulatory requirements. Their approach illustrates how AI and human expertise together accelerate certification readiness while ensuring industry-specific compliance nuances are addressed. Organisations evaluating AI should therefore prioritise solutions that preserve human oversight and provide transparent audit trails.
In what ways does AI improve audit efficiency and accuracy?
AI improves audit efficiency by automatically extracting required fields from documents, tagging them to relevant ISO clauses, and compiling an evidence pack that auditors can review rather than assemble manually. NLP models identify clause-related language and populate metadata like owner, version and effective date, reducing manual entry errors and accelerating search. Pattern detection algorithms reduce false positives by learning normal change patterns and highlighting only deviations that matter, which focuses auditor attention where it is most needed. The result is measurable time savings in evidence collection and higher confidence in the accuracy of metadata used during certification audits.
How can AI-driven document management systems support compliance?
AI-driven DMS platforms support compliance by enforcing policy checks on document changes, creating immutable audit trails and enabling human-in-the-loop validation to maintain audit defensibility. Automated checks can prevent publication of documents missing required attributes, enforce retention rules and trigger workflows for required approvals. Immutable logs and cryptographic timestamps provide objective evidence of who changed what and when, while human review ensures that AI outputs are validated for contextual correctness. Organisations should design DMS+AI configurations that combine automated enforcement with review gates to meet both operational needs and audit scrutiny.
What Industry-Specific Considerations Affect Document Control in ISO 9001?
Industry-specific considerations affect the level of control, retention periods and traceability required for documented information; regulated sectors typically demand stricter access controls, longer retention and more granular traceability. For example, manufacturing and automotive sectors emphasise batch traceability and component-level records, healthcare prioritises patient confidentiality and retention aligned with data protection laws, and IT organisations emphasise change control and configuration management. Tailoring document control to sectoral risks ensures that the QMS meets both ISO 9001 expectations and external regulatory or contractual obligations.
The need for robust, automated data management is particularly acute in highly regulated industries, where compliance and audit readiness are paramount.
Automating ISO 9001 Data Flows for Compliance & Audits
The increasingly complicated nature of the regulated manufacturing environment demands strong data management architectures on the basis of international standards management. In particular, the defense and aerospace sectors, where the International Traffic in Arms Regulations (ITAR) and the ISO 9001 quality management standards apply, face big issues related to the provision of secure, traceable, and audit-ready data streams within the enterprise systems. The possibility of non-compliance, inefficiency, and slow audits exists with paper-based processes and system design fragmentation. The paper proposes a model of automation of compliance-ready data flows, integrating enterprise resource planning (ERP), manufacturing execution system (MES), and product lifecycle management (PLM) settings with compliance engines based on rules, metadata-driven traceability, and automated audit records. It is an ITAR and ISO 9001-based approach to secure data management, real-time authent
AUTOMATING COMPLIANCE-READY DATA FLOWS IN ITAR AND ISO 9001 CERTIFIED MANUFACTURING SYSTEMS, 2025
How do document control requirements vary across industries like automotive and healthcare?
In automotive, document control often requires strict traceability of parts, lot-level records and stringent change management tied to product safety standards, so retention and versioning must support root-cause analysis and recall actions. Healthcare document control centres on patient record confidentiality, consent documentation and retention aligned to statutory requirements, which means access controls and encryption are paramount. Two mini-case examples illustrate the difference: an automotive supplier must link inspection records to serial numbers for parts, while a clinic must ensure patient records are only accessible to authorised clinicians and retained per healthcare regulations. These sectoral nuances shape the controls and evidence auditors expect.
What are best practices for managing documented information in diverse sectors?
Universal best practices include centralising documented information in a controlled repository, implementing role-based access, defining retention schedules aligned to regulation, and performing regular review cycles to keep content current. Prioritise controls based on risk — for example, emphasise traceability in manufacturing and confidentiality in healthcare — and document these priorities in the QMS so auditors can understand your rationale. Regularly test evidence retrieval procedures and simulate audits to validate that your document control processes deliver timely, complete evidence. These practices create a resilient documented information baseline that supports both operational performance and certification readiness.
- Centralised DMS: Ensures a single source of truth and consistent metadata.
- Role-based Access: Protects sensitive records and enforces segregation of duties.
- Retention Schedules: Align with legal and contractual requirements and automate disposition.
These practices provide a prioritized roadmap for organisations to align document control with both ISO 9001 and sector-specific expectations, making audits and client engagements more predictable and defensible.