ISO 9001 Internal Audits: Comprehensive Guide to Preparation and Execution for Business Leaders
An ISO 9001 internal audit is a systematic, independent evaluation of a Quality Management System (QMS) that verifies conformance to ISO 9001 requirements and uncovers improvement opportunities for business leaders. This guide aims to show that ISO 9001 certification is often required by key clients and procurement processes, and it will equip leaders with practical steps to prepare, execute, report, and follow up on internal audits. Readers will learn how internal audits function as both compliance evidence and a driver for continual improvement, how to design a risk-based audit program, and how to collect objective evidence that supports certification readiness. The article maps the audit lifecycle from planning and auditor competence through execution and corrective action tracking, and it integrates contemporary trends such as AI, cybersecurity, and ESG that shape audit scope in 2024 and beyond. By the end, you will have a structured internal audit approach suitable for management review and third-party certification readiness, and you will understand when to engage accredited certification services to meet client requirements.
To further clarify the foundational concepts, it’s helpful to consider a detailed definition of ISO 9001 and its role in quality management systems.
ISO 9001: International Standard for Quality Management Systems
A quality management system (QMS) is the combination of methods, principles, and processes of quality excellence applied in an organization. A QMS focuses always on meeting and overachieving customer requirements. The QMS has a set of guidelines that are defined by a collection of policies, processes, documented procedures, and records. This system defines how a company will achieve the creation and delivery of the product or service they provide to their customers. When implemented in your company, the QMS needs to be specific to the product or service you provide, so it is important to tailor it to your needs. However, in order to help ensure that you do not miss elements of a good system, some general guidelines exist in the form of ISO 9001 (Quality Management System—Requirements), which is intended to help standardize how a QMS is designed. ISO 9001 is the international standard for quality management systems (QMSs), published by ISO (the International Organization for Standardization).
Audits and quality management systems (QMS), M Helmold, 2023
Why Is ISO 9001 Certification Essential for Your Key Clients?
ISO 9001 certification signals that an organization maintains a documented, consistently applied QMS that reduces supplier risk and supports contractual compliance. Many clients and procurement teams treat ISO 9001 as a minimum assurance for supplier selection because the certification demonstrates consistent process controls, traceable records, and a formal corrective action framework. These assurance mechanisms reduce operational risk and simplify vendor management, which in turn shortens onboarding and accelerates contract negotiations. Understanding these client expectations helps leaders prioritize audit activities that directly affect procurement decisions and commercial eligibility.
ISO 9001 Certification delivers three primary client-focused advantages:
- Procurement Eligibility: Certification often meets buyer prequalification requirements and accelerates tender acceptance.
- Risk Reduction: Consistent processes and documented controls lower the probability of supplier-driven defects and service failures.
- Trust and Credibility: Third-party verification gives clients measurable confidence in supplier quality and transparency.
What Are the Strategic Benefits of ISO 9001 Certification?
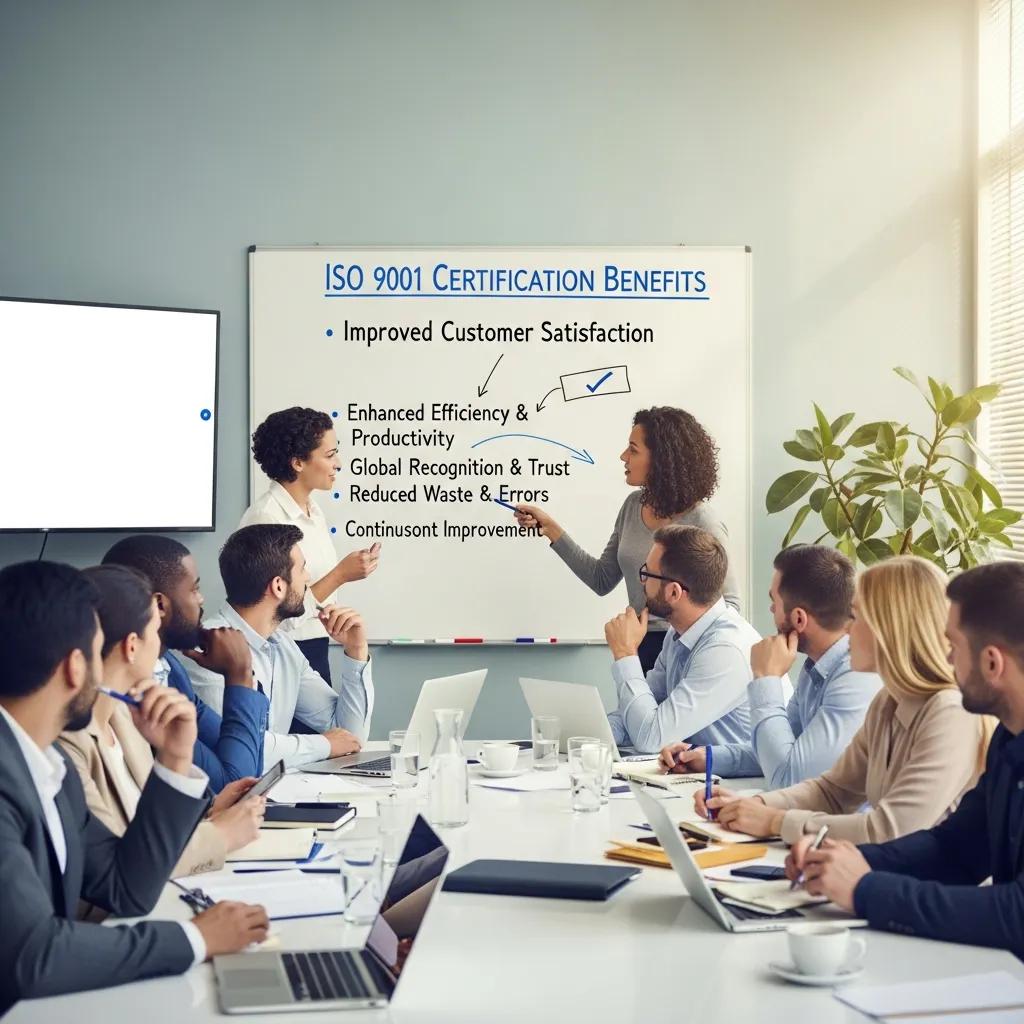
ISO 9001 certification creates measurable strategic value by aligning operational performance with customer expectations and reducing waste across processes. Certified QMS processes establish KPIs for quality, on-time delivery, and defect reduction, enabling leaders to measure and report improvements that resonate with clients and stakeholders. For example, a well-executed certification program can reduce rework rates and shorten customer onboarding cycles, improving margins and customer retention. The strategic alignment between process control and client requirements strengthens commercial positioning and allows management to use audit results as input to strategic planning and resource allocation.
This strategic perspective on certification naturally leads to how the documented QMS and third-party verification build client trust and competitive advantage.
How Does ISO 9001 Build Client Trust and Competitive Advantage?
ISO 9001 builds client trust through third-party verification that validates an organization’s processes, controls, and improvement mechanisms. Documented processes and objective audit evidence enable suppliers to make evidence-based claims during RFPs and tenders, and this differentiation is especially valuable in crowded markets where process maturity matters. Standardized process metrics and controls mean buyers face lower supplier risk, which can translate into preferred supplier status or faster contract awards. Recognizing this link between documented controls and client perception clarifies why internal audits must generate verifiable evidence and management-ready summaries.
Understanding the role of internal audits within the QMS lifecycle is the next step for leaders preparing for certification readiness and continual improvement.
What Is the Role of Internal Audits in ISO 9001 Quality Management Systems?
An internal audit is a planned activity within the QMS that assesses conformity to ISO 9001 requirements, verifies effectiveness of controls, and identifies opportunities for improvement. Internal audits provide the objective evidence organizations need for management review and for demonstrating readiness for external certification audits. They function as an early warning system by surfacing non-conformities and process weaknesses before an external auditor identifies them, thereby reducing certification risk. Regular internal audits also create the data required to evaluate corrective actions, measure improvement over time, and inform resource allocation decisions.
Internal audits support compliance and continual improvement by linking findings to process change and metrics that track effectiveness, which leads into specific examples of audit-to-improvement flows.
How Do Internal Audits Support Compliance and Continuous Improvement?
Internal audits support compliance by systematically identifying deviations from documented processes and regulatory or contractual requirements and by initiating root-cause analysis for each finding. Findings feed into a corrective action process that assigns owners, deadlines, and verification steps, enabling measurable closure and evidence for management review. Over successive audit cycles, organizations track KPI trends—such as defect rates or on-time delivery—demonstrating the effectiveness of corrective actions. This audit-to-improvement feedback loop embeds continual improvement into operational routines and provides tangible evidence for both clients and certification bodies.
Explaining the differences between internal and external audits clarifies their complementary roles in certification readiness and assurance.
What Are the Differences Between Internal and External Audits?
Internal audits are performed by the organization to drive improvement and verify ongoing compliance, while external audits are conducted by independent certification bodies to verify conformity and grant certification status. Internal auditors focus on improvement, root-cause analysis, and preparation of objective evidence; external auditors focus on conformity, impartiality, and formal certification decision criteria. Internal audits can be more frequent and tailored to risk, whereas external audits follow a prescribed certification cycle and sampling approach. Understanding these differences helps organizations design internal audit programs that prepare processes and records for successful external verification.
With the role and differences clarified, leaders must know how to prepare an effective internal audit program that uses risk-based scoping and competent auditors.
How Do You Prepare Effectively for an ISO 9001 Internal Audit?
Preparation starts with a risk-based audit program that defines scope, frequency, objectives, and resource allocation to focus on high-impact processes. An effective preparation sequence includes reviewing QMS documentation, updating or creating process checklists, mapping process owners, and scheduling audits to align with business cycles and management review timelines. Selecting competent auditors and ensuring impartiality are essential steps that preserve audit objectivity and the credibility of findings. A clear audit calendar and checklists reduce surprises and ensure that audit objectives generate actionable evidence for continuous improvement and certification readiness.
The importance of a risk-based approach in modern quality management systems, such as ISO 9001, is further highlighted by expert perspectives.
Risk-Based Auditing in ISO 9001 Quality Management
However, current halal auditing practices remain uniform and checklist-based, lacking differentiation based on the relative risk of ingredients, processes, or suppliers. In contrast, risk-based auditing has become a key component in modern quality and management systems such as ISO 9001, ISO 31000, and ISO 22000. Despite this trend, risk-based methodologies have yet to be formally integrated into halal certification protocols.
A Risk-Based Auditing Framework for Halal Certification Systems: Bridging Gaps in the Current Halal Assurance Practices, R Umar, 2025
Follow these key preparation steps to build a practical internal audit program:
- Risk-based Scoping: Prioritize processes based on risk, customer impact, and previous findings.
- Documentation Review: Verify procedures, work instructions, and records ahead of fieldwork.
- Auditor Selection and Scheduling: Assign competent, impartial auditors and set an audit calendar aligned to management reporting.
Before listing program trade-offs, here is a compact comparison of typical audit program design choices and their implications.
| Program Element | Characteristic | Typical Trade-off |
|---|---|---|
| Scope | Broad process coverage | Wider insight vs. longer audit duration |
| Frequency | Quarterly/annual cadence | Early detection vs. resource intensity |
| Resources | Internal vs. external auditors | Cost control vs. objectivity and specialist skills |
The next step is selecting and training competent auditors who can deliver reliable findings.
What Are the Key Steps in Planning an Internal Audit Program?
Planning begins by mapping organizational processes and applying a risk assessment to determine audit priority and frequency. Define clear audit objectives and criteria, align the audit schedule with production cycles or critical delivery windows, and allocate resources with contingency time for follow-up. Prepare or update process-specific checklists and sampling rationales to guide fieldwork and evidence collection. Establish reporting templates and escalation paths so findings translate quickly into corrective actions and management decisions.
Careful planning reduces surprise findings during fieldwork and ensures that audit results feed directly into management review and certification readiness.
How Do You Select and Train Competent Internal Auditors?
Select auditors based on technical knowledge of the processes being audited, understanding of ISO 9001 requirements, and proven ability to remain objective and evidence-focused. Training should cover audit techniques, root-cause analysis, interview skills, sampling methods, and how to document objective evidence clearly and concisely. Use mentoring, observed audits, and periodic competency assessments to validate auditor readiness and to identify development needs. Impartiality safeguards—such as avoiding audits of one’s own work—preserve credibility and align audit outcomes with management expectations.
Equipping auditors with both technical and interpersonal skills increases the likelihood that audits will yield actionable findings and verifiable evidence for certification bodies.
What Are the Best Practices for Executing an ISO 9001 Internal Audit?
Effective execution centers on collecting objective, triangulated evidence, using sampling rationale, and conducting structured interviews that reveal both compliance and performance gaps. Auditors should rely on documents, records, and direct observations, and should use clear checklists and evidence logs to maintain an audit trail. Interview techniques must be open, non-confrontational, and focused on process behavior rather than personal blame to uncover true root causes. Consistent documentation and impartial wording in findings ensure management can act decisively and that external auditors can trace evidence during certification assessments.
Here are five concise best practices to guide audit execution:
- Plan and communicate scope in advance to ensure readiness and access to records.
- Triangulate evidence by combining document review, interviews, and observation.
- Use sampling rationales to make findings statistically and operationally defensible.
- Document findings impartially with clear evidence references and context.
- Close interviews with next-step agreements to ensure owners understand follow-up expectations.
Before showing evidence mapping, here is a practical table that links evidence types to sample collection techniques and tools.
| Evidence Source | Evidence Type | Practical Example / Tool |
|---|---|---|
| Documents | Process descriptions | Version-controlled SOPs and change logs |
| Records | Transaction logs | Production records, inspection sheets, data exports |
| Observation | Work activity | Direct observation checklists and photo records |
How Do You Gather Objective Evidence During the Audit?
Gathering objective evidence requires planned sampling, use of records and data logs, and clear notes that reference timestamps, document versions, and observer details. Start with document and record review to establish expected behavior, then confirm actual practice through observation and targeted interviews that probe the “how” and “why” of process steps. Use audit software or evidence checklists to capture photographic records, data extracts, and witness statements in a way that can be retraced by others. Preserve objectivity by avoiding assumptions and by citing verifiable artifacts and direct observations in each finding.
Clear evidence collection prepares the organization for effective corrective action and supports claims during external certification audits.
How Are Non-Conformities Identified and Documented?
Non-conformities are identified when objective evidence shows deviation from ISO 9001 requirements, documented procedures, or stated customer requirements, and they must be recorded with precise, factual language. Classify findings by severity—major, minor, or observation—based on impact to product/service conformity or system integrity, and include supporting evidence, relevant clauses, and the sample used. Provide recommended corrective actions and suggest owners and deadlines to ensure timely closure and verification. Well-written findings enable efficient root-cause analysis and clear tracking through the corrective action lifecycle.
Properly classifying and documenting non-conformities ensures corrective actions are actionable and verifiable, which leads into reporting and follow-up mechanisms.
How Should You Report and Follow Up After an ISO 9001 Internal Audit?
An internal audit report should summarize scope and objectives, list findings with objective evidence, recommend corrective actions, and propose priorities for management. Reports must be concise for executives while retaining attachments or evidence logs for auditors and external reviewers, so management review meetings can act on risk-prioritized items. Assign owners, deadlines, and verification steps for each corrective action and track these in a centralized tracker that feeds into continual improvement metrics. Verification of effectiveness is critical; closing a finding requires documented evidence that the corrective action addressed the root cause and prevented recurrence.
The following numbered list outlines essential report elements to include for management and certification purposes.
- Executive Summary: Concise statement of audit scope, high-level findings, and critical risks.
- Detailed Findings: Each finding with objective evidence, clause references, and severity.
- Corrective Action Plan: Owners, actions, due dates, and verification criteria.
A robust report structure ensures audit outputs transition quickly into owned actions and measurable improvement cycles.
Below is a concise corrective-action tracking template showing essential fields for consistent follow-up and verification.
| Item | Attribute | Metric / Template Field |
|---|---|---|
| Finding | Severity | Major / Minor / Observation |
| Root Cause | Analysis Method | 5-Why / Fishbone |
| Corrective Action | Owner & Due Date | Named owner; YYYY-MM-DD |
| Verification | Evidence Type | Test records, re-audit notes |
| Closure | Verification Result | Verified / Not Verified |
Using a standardized tracker reduces ambiguity and speeds verification prior to management review. The next subsection describes lifecycle practices to ensure corrective actions become lasting improvements.
What Are the Essential Elements of an Internal Audit Report?
Essential elements include a clear executive summary, defined scope and criteria, individual findings with objective evidence, and a prioritized corrective action plan with owners and deadlines. Attachments should include evidence logs, sampling rationales, and copies of reviewed records so management and external auditors can reproduce the audit trail. Use consistent templates to make trend analysis straightforward and to feed measurable KPIs into management review, demonstrating continuous improvement. Clear reports accelerate decision-making and help preparation for external certification assessments.
Structured reporting and tracking naturally flow into the corrective action lifecycle, which secures long-term improvement from audit findings.
How Do You Implement Corrective Actions and Drive Continuous Improvement?
Implement corrective actions by first performing a root-cause analysis—using methods such as 5-Why or fishbone diagrams—then designing actions that address systemic causes rather than symptoms. Assign ownership and realistic deadlines, and require documented verification steps that produce evidence of effectiveness, such as re-inspections or process performance metrics. Track KPIs over time to confirm that actions reduce defect rates or improve delivery performance, and integrate lessons learned into training and process updates. This cycle of detect → act → verify embeds continual improvement into the QMS and demonstrates to clients and auditors that the organization responds effectively to identified risks.
Effective corrective action drives culture change and prepares organizations for both internal resilience and external certification scrutiny.
What Are the Emerging Trends Shaping the Future of Internal Audits in 2024 and Beyond?
In 2024 and beyond, internal audits will increasingly incorporate AI-driven analytics, a stronger focus on cybersecurity and cloud controls, and the integration of ESG metrics into audit criteria and supplier assessments. AI and continuous monitoring enable real-time anomaly detection and automated evidence sampling, changing audit frequency and sampling strategies. Cybersecurity concerns require auditors to evaluate cloud controls, access management, and incident detection processes as integral parts of QMS risk. ESG introduces operational metrics—such as supplier environmental performance and social governance—that audit programs must incorporate to meet stakeholder expectations and regulatory shifts.
These shifts require updated auditor skills and audit program designs, which the next subsection explores in practical terms.
How Will AI, Cybersecurity, and ESG Impact Internal Audit Processes?
AI will automate repetitive evidence collection and highlight anomalies in process data, enabling auditors to focus on root-cause analysis and exception investigation. Cybersecurity considerations will expand audit scopes to include system access controls, incident response readiness, and third-party cloud provider assurances. ESG will require auditors to assess related processes, data accuracy, and supplier sustainability claims, integrating those results into management reporting. Organizations that adapt audit scope and auditor competence for these trends will gain faster, more accurate assurance and a stronger position with clients who demand modern risk oversight.
Adapting to these trends also means aligning with new global internal audit standards that emphasize purpose, technology, and collaborative capability.
What Are the Implications of New Global Internal Audit Standards?
New global standards emphasize alignment with organizational purpose, increased collaboration between audit and technology functions, and elevated competency expectations for auditors, particularly in data analytics and risk assessment. Leaders should revise audit policies, update competency matrices, and invest in training that builds data literacy and cybersecurity awareness among auditors. Audit programs should incorporate technology-assisted techniques and define how AI-derived evidence is validated and archived. Implementing these changes ensures audit functions remain credible, effective, and aligned with both certification expectations and client demands.
These evolving expectations make it prudent to consider external certification support when internal capacity or independence is constrained. For organizations seeking accredited certification guidance, Stratlane Certification Deutschland provides ISO certification services supported by experienced industry experts and AI-enabled auditing approaches that help demonstrate compliance, improve operational efficiency, and strengthen brand credibility.
How Will These Standards Affect Your Audit Roadmap?
New standards will prompt organizations to formalize auditor skills development, integrate continuous monitoring, and document how technology supports audit conclusions and evidence retention. Adjusting the audit roadmap to include technology validation steps, cross-functional collaboration, and updated competency gates will keep audit outputs defensible and management-ready. This roadmap shift also affects procurement and client communications, as organizations can present more timely and data-backed assurance to buyers and stakeholders. Leaders who incorporate these standard-driven changes early will streamline certification efforts and better meet evolving client expectations.
For organizations ready to convert audit readiness into certified assurance, Stratlane Certification Deutschland offers accredited ISO certification services that leverage experienced industry auditors and AI-enhanced assessment tools to support certification objectives and improve operational performance.